Skip to content

GigaOm Again Names Scale Computing a Leader in Full-Stack Edge Deployments

Company Recognized as Leader and Fast-Mover in the GigaOm Radar Report for the Second Consecutive Year

INDIANAPOLIS – July 8, 2025 – Scale Computing, a market leader in edge computing, virtualization, and hyperconverged solutions, today announced that GigaOm has named the company a Leader in the GigaOm Radar Report for Full-Stack Edge Deployments. For the second consecutive year, Scale Computing is positioned in the inner-most Leader ring, and has been recognized as a Fast Mover, in the Maturity/Platform Play quadrant of the Radar chart. The report plots vendor solutions across a series of concentric rings, with those closer to the center judged to be of higher overall value.

The demands of a digital world and for near-real-time response are driving the need for more applications to run outside the cloud or data center, in distributed locations that are closer to where they are used by people, devices, and IoT technologies. Full-stack edge computing deployments deliver a cloud-like experience to these edge locations, which are otherwise difficult to manage at scale. Cloud-managed and cloud-connected, these hyperconverged infrastructure (HCI) solutions provide all the necessary tools to run applications at customers’ preferred locations for local data collection and processing.

“Scale Computing offers a full-stack edge solution that delivers virtualization, servers, storage, backup, disaster recovery, and fleet management, all in a single, easy-to-manage platform that scales seamlessly and puts computing power at the edge of the network, where organizations need it most,” said Jeff Ready, CEO and co-founder of Scale Computing. “As the future of IT moves rapidly to the edge, Scale Computing is honored to once again be named a Leader in the GigaOm Radar report for Full-Stack Edge Deployments. We’re proud to empower businesses globally with solutions that are easy to use, easy to manage, and easy to deploy—from branch offices to factory floors to distributed retail locations. For organizations looking to scale their Edge AI capabilities, SC//Platform offers a future-proof solution that integrates seamlessly with existing infrastructure, simplifying the complexities of edge AI adoption and enabling enterprises to harness the full potential of AI-driven operations at the edge.”

Scale Computing Platform (SC//Platform) is recognized for bringing together simplicity and scalability in a single offering to replace existing IT infrastructure, providing high availability for running workloads and enabling enterprises to run applications and process data at the edge of their networks. As more enterprises transition to agentic AI-driven operations, SC//Platform’s integrated autonomous management, decentralized AI processing, and AI-driven optimization capabilities empower organizations to deploy AI at the edge with confidence, ensuring resilience, adaptability, and operational simplicity.

Together with its companion Key Criteria report, GigaOm’s Radar Report provides an overview of the market, identifies leading full-stack edge deployment offerings, and helps decision-makers evaluate solutions to make more informed investment decisions. The new report examines 16 of the top solutions and dives into what technology needs and best practices should be considered when looking at full-stack edge deployments. Scale Computing scored well on a number of decision criteria, including:

  • Cloud-like management: Scale Computing HyperCore (SC//HyperCore), powered by the Autonomous Infrastructure Management Engine (AIME), handles day-to-day administrative and maintenance tasks automatically, monitors the system for security, hardware, and software errors, and remediates errors where possible.
  • Plug-and-play provisioning: SC//HyperCore enables seamless programmatic deployment of containers.
  • Visibility and monitoring: Scale Computing Fleet Manager (SC//Fleet Manager), a cloud-hosted monitoring and management tool built for hyperconverged edge computing infrastructure at scale, can monitor fleets from one to 50,000 SC//HyperCore-based clusters, empowering administrators to centrally configure clusters of edge computing infrastructure prior to nodes arriving on-premises with cloud-like simplicity.

To learn more about Scale Computing and view a complimentary copy of the GigOm Radar Report for Full-Stack Edge Deployments, please visit scalecomputing.com/landing-pages/gigaom-radar.

About Scale Computing
Scale Computing is a leader in edge computing, virtualization, and hyperconverged solutions. Scale Computing HC3 software eliminates the need for traditional virtualization software, disaster recovery software, servers, and shared storage, replacing these with a fully integrated, highly available system for running applications. Using patented HyperCore™ technology, the HC3 self-healing platform automatically identifies, mitigates, and corrects infrastructure problems in real-time, enabling applications to achieve maximum uptime. When ease-of-use, high availability, and TCO matter, Scale Computing HC3 is the ideal infrastructure platform. Read what our customers have to say on Gartner Peer Insights, Spiceworks, TechValidate and TrustRadius.

About Version 2 Limited
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

ISO 27001 vs. SOC 2: What’s the difference?

Summary: ISO 27001 or SOC 2? Discover which fits your business best, compare key differences, and see how NordLayer supports both compliance standards.

ISO 27001 vs. SOC 2: Which compliance standard is better for your organization? This question often comes up when companies need to prove they take data security seriously, especially in fast-growing or highly regulated industries.

Both SOC 2 and ISO 27001 offer trusted frameworks for protecting sensitive information, but they take different paths to get there.

SOC 2 specifies criteria for how companies should manage controls to protect customer data from unauthorized access, cybersecurity incidents, and other risks. ISO 27001 goes deeper, providing a framework for implementing an end-to-end security system that covers people, technologies, and processes.

Not sure which one fits your business best? You’re not alone. In this guide, we’ll compare ISO 27001 vs. SOC 2, how they differ, what they have in common, and how to choose the right security compliance standard for your organization.

What is ISO 27001?

ISO 27001 is a global standard for managing information security. Created by the International Organization for Standardization (ISO) and the International Electrotechnical Commission
(IEC) outlines how to build a strong information security management system (ISMS). It addresses areas such as risk assessment, access control, and incident response.

The framework categorizes its controls into four key themes: organizational, people, operational, and technological. If your business handles customer data, ISO 27001 demonstrates that you have structured, reliable systems that help keep that information safe.

To get ISO 27001 certification, an accredited third-party auditor must confirm that you meet all the compliance requirements. This certification is a good fit for companies that want to build trust, meet regulatory expectations, and protect sensitive information.

Comparison table of ISO 27001 and SOC 2

What is SOC 2?

SOC 2 stands for Systems and Organization Controls 2. It’s a security compliance standard created by the American Institute of Certified Public Accountants (AICPA) to help companies keep customer data safer from data breaches, unauthorized access, and other cyber threats.

A SOC 2 report proves your company’s security measures are effective. It’s like a trust badge that shows you handle, process, and store customers’ data responsibly and securely.

Who benefits from a SOC 2 report?

  • Cloud service providers
  • SaaS companies
  • Digital financial companies
  • Healthcare organizations

If you’re in one of these industries, having SOC 2 compliance will give you a competitive edge.

ISO 27001 vs. SOC 2: Key differences

One big difference between ISO 27001 and SOC 2 is how compliance is verified. ISO 27001 gives you an official certification. Pass the requirements, and you’re certified—simple as that.

SOC 2 works a bit differently. You don’t get a certificate. Instead, an independent auditor writes a SOC 2 attestation report, giving their expert opinion on whether you meet the SOC 2 compliance criteria.

So, how do ISO 27001 and SOC 2 differ? Both certification and attestation involve a deep dive by an external auditor. Certification feels more formal, but in some industries, ISO 27001 carries more weight.

Here is a summary of the main differences between SOC 2 and ISO 27001:


SOC 2

ISO 27001

Issuing/ standard body

ISO/IEC ANSI-ASQ

National Accreditation Board (ANAB)

Presentation

An attestation that results in a detailed report of your security controls

A certification that shows you’ve passed the ISO 27001 audit

Target market

United States

International

Core requirements

Trust Service Criteria:
Security, Availability, Confidentiality, Processing Integrity, And Privacy

Clauses 4-10 of the framework, including the ISMS scope, statement of applicability, risk management, and continual improvement

Audit results

SOC 2 attestation report, made available only under NDA

SOC 2 reports are valid for 12 months and require a new SOC 2 every year

ISO report that includes a 1-page certification that can be made public

Recertification is required after 3 years

Timeline

1–4 months for the Type I report and 6–12 months for the Type II report

Approx. 3–12 months

Cost

Varies by the size and complexity of an organization

Typically $10–60k

Varies by the size and complexity of an organization

Typically $10–25k

Let’s take a closer look at ISO 27001 vs. SOC 2 to understand them better.

Compliance requirements

SOC 2 and ISO 27001 share quite a few security controls, but they don’t ask for the same level of implementation.

Both standards say you need to apply internal controls that are relevant to your business. But ISO 27001 tends to be stricter. You’ll need to meet more criteria and cover a broader set of controls to be fully ISO 27001 compliant.

SOC 2 is a bit more flexible. It’s based on five Trust Services Criteria—but only one (Security) is required in every SOC 2 report. The other four (Availability, Confidentiality, Processing Integrity, and Privacy) are optional, depending on what your company does.

Location: Which standard do your customers expect?

Both SOC 2 attestation and ISO 27001 certification are respected in the security and technology world, but where you do business can influence which one you need.

If your clients are in North America, SOC 2 is usually the go-to. It’s the standard most U.S. and Canadian companies expect.

On the other hand, ISO 27001 is more common internationally. So if you’re working with customers in Europe, Asia, or other global markets, ISO 27001 is likely the better fit.

Timeline: How long does it take to get compliant?

SOC 2 and ISO 27001 differ not only in what they ask of you but also in the amount of time it takes to complete.


ISO 27001

SOC 2 Type 1

SOC 2 Type 2

Timeline

6-12 months

1-4 months

3-12 months

What does it involve?

Auditors review your documentation and check your ISMS to ensure it complies with ISO 27001

Auditors look at your security controls at a single point in time

Auditors review your security controls over 3-12 months to see how they work in practice

So, if your organization needs to demonstrate compliance quickly, SOC 2 Type 1 offers a faster path. However, for clients who require long-term assurance of your security practices, SOC 2 Type 2 or ISO 27001 may provide the depth and credibility they expect.

Audit process: What to expect with ISO 27001 vs. SOC 2

Both ISO 27001 and SOC 2 follow a structured process. You’ll need to define your security goals, run a gap analysis, implement key controls, collect documentation, and set up a system for ongoing improvement.

The difference lies in who audits you.

  • ISO 27001 requires an accredited certification body to certify your compliance.
  • SOC 2 must be audited by a licensed CPA firm.

Renewal timelines also differ:

  • SOC 2 Type 2 reports are valid for 12 months, typically renewed every year.
  • ISO 27001 certificates last for three years, with annual surveillance audits and a full recertification audit in year three.
ISO 27001 and SOC 2: More in common than you think

SOC 2 and ISO 27001 focus on core principles like data security, confidentiality, integrity, and availability.

Both require organizations to implement strong security measures and undergo independent audits to prove it. In fact, there’s up to 80% overlap between the two frameworks, so working toward one puts you well on the way to meeting the other.

While neither is mandatory, getting certified or attested shows clients and partners that your data protection practices are trustworthy.

Feature

ISO 27001 & SOC 2 similarities

Focus

Protecting data security, confidentiality, integrity, and availability

Framework type

Risk-based approach to managing information security

Security controls

Require the implementation of internal controls and policies

Audit requirement

Independent third-party audit or assessment

Outcome

Demonstrates trust and security posture to clients

ISO 27001 and SOC 2: Which one is right for you?

Choosing between ISO 27001 and SOC 2 depends on your goals, clients, and the maturity of your current information security setup. Both standards help service organizations demonstrate strong, reliable security practices, and each is designed to meet different business needs.

When to choose ISO 27001

Go with ISO 27001 if you’re building an information security management system (ISMS) from the ground up. This standard is globally recognized, making it ideal if you work with international clients or want to show that your data protection measures meet global expectations.

  • It’s a great fit for organizations looking for a structured, long-term approach to security.
  • Stakeholders and partners often view ISO 27001 certification as a strong signal of trust.
  • It’s more rigorous and requires more resources, but it builds a robust foundation.

When to choose SOC 2

SOC 2 is a better option if your organization already has an ISMS and wants to validate its controls. It’s especially relevant for service organizations that operate primarily in North America.

  • SOC 2 offers more flexibility, letting you focus audits on specific Trust Services Criteria.
  • It’s a lighter, faster, and often more cost-effective route for companies that want tailored insights into their information security practices.
  • It’s a strong choice if you need to meet client demands without committing to global certification yet.

When to choose both

For some organizations, the best answer is both.

Use ISO 27001 to establish a robust, globally recognized information security management system. Once that’s in place, conduct regular SOC 2 audits to keep improving and get detailed feedback on how well your controls work.

Together, ISO 27001 and SOC 2 give you full-spectrum credibility, offering both the structured foundation and ongoing validation your clients expect, no matter where they are. It’s a smart move for growing companies that take data protection seriously and want to stay competitive in multiple markets.

Choosing between ISO 27001 and SOC 2 isn’t a one-size-fits-all decision. It really depends on your goals, resources, and where your clients are.


How NordLayer helps you stay ISO 27001 and SOC 2 compliant

Whether you’re building an ISMS from scratch or fine-tuning existing controls, NordLayer supports your compliance journey. We have security solutions to meet both compliance standards.

  • Access controls: Network Access Control (NAC) solutions like Cloud Firewall and Device Posture Security help manage access to sensitive data, ensuring that only authorized users and devices can access your network.
  • Encryption: NordLayer encrypts traffic in transit using the AES-256 and ChaCha20 algorithms to help you meet the data security standards required by both frameworks.
  • Secure access to data in the cloud: Whether you’re using AWS, Google Cloud, or Microsoft Entra ID, we help secure your cloud environments with Site-to-Site network connectors and SaaS security solutions.
  • Network visibility: With event logging, real-time monitoring, and device posture monitoring, NordLayer helps you monitor network access and maintain audit logs for up to 60 days.
  • Threat prevention: NordLayer’s Threat prevention features help restrict access to untrusted websites and users, detect and stop malicious downloads, and prevent potentially harmful malware or other cyber threats from infecting your devices.

NordLayer is designed for modern, fast-growing organizations that want flexibility without sacrificing control. Whether you’re pursuing ISO 27001, SOC 2, or both, we support your compliance journey.

Contact our sales team to find out how NordLayer can help you achieve your goals.

ISO 2700 vs. SOC 2: Frequently Asked Questions

SOC 2 vs. ISO 27001: Which makes more sense for your business?

SOC 2 is great if you work mostly with U.S. clients and want a flexible audit. ISO 27001 is better for global businesses needing a structured security system. Pick the one that fits your goals, or go for both.

Can a company become ISO 27001 and SOC 2 compliant at the same time?

Yes, it can. These two security standards share a lot, especially when it comes to information security controls and data protection. Combining the processes can save time, reduce duplicated effort, and give your business a stronger, more unified approach to service organization security.

When might ISO 27001 not be enough?

ISO 27001 may fall short if clients specifically require a SOC 2 report, or if you need detailed, customer-facing proof of control performance over time. In U.S. markets, SOC 2 often holds greater practical relevance.

How to achieve SOC 2 and ISO 27001 compliance?

Start by defining your security goals, conducting a gap analysis, and implementing required controls. For ISO 27001, work with an accredited certification body; for SOC 2, use a licensed CPA firm. Maintain continuous monitoring and documentation.

Disclaimer: This article is for informational purposes only and not legal advice. Use it at your own risk and consult a licensed professional for legal matters. Content may not be up-to-date or applicable to your jurisdiction and is subject to change without notice.


About Nord Security
The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

About Version 2 Limited
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

Phishing-as-a-service: Tools, tactics, and risks for organizations

Symbolic illustration of phishing as a service system, with interconnected circles representing the attacker’s toolkit and workflow

Summary: Phishing-as-a-service lets anyone launch advanced attacks using ready-made kits. Learn how it works, the risks it poses, and how to defend.

SaaS models have spread to the dark web, and that’s a problem. Criminals can now buy or sell the technology needed to mount diverse cyberattacks, including large-scale phishing campaigns.

Phishing-as-a-service (PhaaS) is a critical cyber risk for all companies. Attacks that were once too complex for low-skill hackers now have an affordable price tag. This article will introduce how PhaaS works, what kits offer, and how to respond.

What is phishing-as-a-service (PhaaS) and who uses it?

Phishing-as-a-service allows unskilled cyber attackers to run phishing attacks by purchasing or renting advanced tools. PhaaS kits created by specialist developers enable novice attackers to build fake websites or send believable emails from trusted contacts.

Phishing-as-a-service streamlines phishing activities. Previously, threat actors needed to build websites, implant payloads, and research targets to create social engineering content. PhaaS provides ready-made phishing kits via familiar subscription models.

PhaaS emerged due to the rising demand for phishing technologies from professional criminal collectives and fraud rings. However, malicious insiders may also purchase and use PhaaS kits to damage their employers and steal sensitive data.

Common features offered in phishing kits

Phishing-as-a-service kits include the tools to contact, manipulate, and attack targets. Common elements of phishing kits include:

  • Customizable templates. Developers include email templates or web pages from legitimate brands. Phishers can enter basic details for each target, or customize the content if needed. Advanced templates offer responsive designs for mobile devices and desktops, and may also include geolocation tools to tailor phishing emails and pages to different regions.
  • Fake login pages. Developers create sites resembling portals for reputable brands (for instance, Google Mail). These phishing domains harvest login credentials from unsuspecting visitors. Advanced kits may include Captcha filters to add credibility.
  • Data harvesting tools. Kits provide backend tools to harvest information from phishing pages and securely store exfiltrated data. Developers may offer encrypted storage via Telegram as a core function or an optional add-on.
  • SMS spoofing tools. Kits allow users to send large quantities of SMS messages from seemingly trusted sources. This is particularly effective when phishers aim to capture one-time passwords and gain access to internal networks.
  • Email spoofing tools. Spoofing allows phishers to bypass email security filters. Phishing tools create fake sender addresses that resemble legitimate contacts.
  • Obfuscation tools. Phishing kits include tools to avoid detection by security systems or make analyzing phishing pages more complex. For example, kits may use URL redirection or content cloaking to avoid filters flagging sites as dangerous.
  • Domain spoofing. Kits include tools to create fake websites that resemble legitimate versions. They may use homoglyphs or typosquatting to generate domains that contain spelling errors but superficially appear convincing.
  • Analytics dashboards. Advanced phishing-as-a-service kits include dashboards to monitor key metrics. For example, analytics tools track click-through rates, rates of successful phishing attempts, and how often victims open malicious attachments. Dashboards may also enable A/B testing to fine-tune phishing techniques and help attackers work around security filters.
  • Customer support/documentation. Some phishing-as-a-service vendors offer onboarding and operational assistance. Kits often feature step-by-step tutorials to evade security measures, research potential victims, and harvest stolen data.
  • Authentication bypassing. Advanced kits like Tycoon 2FA use fake login portals and reverse proxies to create authentic sessions using intercepted credentials – potentially bypassing multi-factor authentication controls.
  • Automatic updates. High-quality phishing kits automatically update tools to work around the latest anti-phishing software.
  • Integrations. Phishing-as-a-service is part of a wider cybercrime ecosystem. For instance, phishing kits integrate with keyloggers and infostealers to gather information and enhance social engineering attacks.

Like standard SaaS, phishing-as-a-service kits provide everything users need to begin operations while minimizing the need for IT expertise. Developers sell flexible payment options, streamline tools for novices, ensure regular updates, and support customer queries.

About NordStellar
NordStellar is a threat exposure management platform that enables enterprises to detect and respond to network threats before they escalate. As a platform and API provider, NordStellar can provide insight into threat actors’ activities and their handling of compromised data. Designed by Nord Security, the company renowned for its globally acclaimed digital privacy tool NordVPN.

About Version 2 Limited
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.
20 Thought Leaders Shaping the MSP Industry in 2025

The Guardz team has curated a list of 20 MSP thought leaders we truly admire.

Whether you’re looking to compare IT solutions, scale marketing efforts, build continuous revenue streams, or learn about the latest breaking industry trends, these 20 elite MSP superstars will provide you with all the insights you need to scale your business and succeed. 

Paul Green

Paul Green is one of the most recognized leaders in the MSP industry. His MSP Marketing Edge newsletter provides a wealth of insights on everything from growth strategies and lead generation to relationship building. Paul’s MSP Marketing Podcast releases new episodes every Tuesday, so make sure you tune in to catch up and become a master of your craft. 

Follow Paul on LinkedIn 

Robin Robins 

Robin has worked with over 10,000 IT business owners from all over the U.S. and in 37 different countries. She has also been a top speaker at many industry-focused events such as CompTIA’s BreakAway, Channel Partners Conference and Expo, and ASCII’s boot camps. Her annual Bootcamps feature some of the biggest celebrity names you can imagine. Robin will teach you how to build a winning MSP system. 

Follow Robin on LinkedIn 

Dave Sobel

Dave Sobel is the host of MSP Radio and The Business of Tech Podcast, where he discusses the latest MSP news, cybersecurity incidents, and goes in-depth on the future of AI for IT, in addition to interviewing some of the industry’s top minds. Dave provides practical advice and valuable strategies any MSP can implement to grow a thriving, sustainable business. One of his latest episodes, “AI to Drive 50% of Business Decisions by 2027,” will certainly make you rethink the possibilities of AI for growth. 

Follow Dave on LinkedIn

Richard Tubb

If you run an MSP or IT consulting business, you have definitely come across Richard Tubb, and if not, we highly recommend following him. His TubbTalk Podcast is among the best in the industry. Richard has also authored the IT Business Owner’s Survival Guide and has over two decades of experience running successful consulting practices.

Follow Richard on LinkedIn

Kathryn Rose

Kathryn Rose is a leading voice in the MSP community. She is the Founder of channelwise, which provides on-demand expert advice for MSPs, and Co-Founder of the Channel Marketing Association (CMA). Kathryn has also been a recipient of many prestigious awards, including the Women in Tech Global Ally Award, Alliance of Channel Women Leadership Award, and the CompTIA Advancing Women in Technology Mentor of the Year Spotlight Award.

Follow Kathryn on LinkedIn

Paco Lebron

Paco Lebron is the Managing Partner and Co-Founder of MSP Unplugged, along with Co-Hosts Rick Smith and Corey Kirkendoll. With over 275 episodes and over a decade running, you’ll find whatever you’re looking for to run a successful IT business, including choosing the right tools for your security stack, pricing strategies, and deep perspectives on AI. 

Paco is also the Founder of ProdigyTeks and the CEO of the MSP Owners Group.

Follow Paco on LinkedIn

Taher Hamid

Taher Hamid is the Founder and Camp Leader of MSP Camp, which provides valuable content and marketing campaigns to help MSPs grow. Taher is also the co-organizer of ScaleCon2025, which brings some of the top MSP leaders together for a 3-day growth-centered conference. ScaleCon2025 will take place September 25th – 27th in New Orleans, so make sure you RSVP your seat today. 

Follow Taher on LinkedIn 

Jennifer Bleam

Jennifer Bleam helps MSPs build scalable marketing and sales systems and grow profitable businesses. Jennifer is also the author of Simplified Cybersecurity Sales For MSPs: The Secret Formula For Closing Cybersecurity Deals Without Feeling Slimy, and has coached over 1,000 MSPs with successful results. She is also the Owner and Founder of MSP Sales Revolution. 

Follow Jennifer on LinkedIn

Steve Taylor

Steve Taylor is the Founder of RocketMSP, one of the top IT channels and MSP podcasts on YouTube. Steve has over 15 years of web design experience, which he combines with technical knowledge to help MSPs get the most out of their cybersecurity investments. 

Steve is also the Lead Content Manager for Alternative Payments and has honed his reputation as a trusted voice in the MSP community.

Follow Steve on LinkedIn

Megan Killion

Megan Killion is a revenue-driven marketer and Chief Consultant at MKC Agency. Her 30-60-90 day plan has helped MSPs double or even triple their revenue, contributing to over $550 million in pipeline generated throughout her illustrious career. We highly recommend checking out her MSP Confidential podcast episode, Build or Buy Marketing?

Follow Megan on LinkedIn 

Harrison Baron

Harrison Baron is the CEO of Growth Generators and the Host of the Brutally Honest Podcast. Harrison understands what it takes for MSPs to build scalable systems and attract more high-value clients. The Growth Generators YouTube channel helps MSPs succeed at every stage, from startup to exit. Check out the episode on The Best Way to Sell Cybersecurity Services in 2025 to learn how to handle common objectives and sell compliance-driven security solutions.

Follow Harrison on LinkedIn 

Zamir Javer

Are you looking to scale your MSP business and add $250K – $2M+ in ARR? Zamir Javer has the answers for you. Zamir is the CEO of Jumpfactor Marketing, with over 15 years of experience, resulting in $1.6 billion in revenue generated for MSPs. Zamir has a specialty for helping MSP & Channel firms generate multiple 7 & 8 figures of revenue in 12 months through advanced MSP marketing strategies. 

Follow Zamir on LinkedIn 

Nigel Moore

Nigel Moore is the CEO and Founder of The Tech Tribe, one of the largest MSP communities out there, with over 3,500 connected members. Nigel began his IT journey over two decades ago and has become a prominent figure in the industry since. 

Follow Nigel on LinkedIn

Erick Simpson

Erick Simpson is the CEO of Channel Mastered and MSP Mastered, and creator of the MSP Mastered® Methodology, a framework trusted by 30,000+ IT Solution Providers.

Some of his accolades include being named a Channel Futures’ “7 Thought Leaders Defining the MSP Market,” Jay McBain’s “100 Most Visible Channel Leaders,” and Syncro’s “#1 MSP Business Growth Resource in North America. 

You can subscribe to Erick’s newsletter here.

Follow Erick on LinkedIn 

Chris Wiser

Chris Wiser is the Founder and CEO of 7 Figure MSP™. Chris has helped MSPs grow from 0 to 6 figures in MRR with built systems. Chris understands how to scale businesses and cut seat count for service professionals. If you want the numbers, Chris will give you the confidence to sell and think like a seasoned pro. 

Follow Chris on LinkedIn 

Justin Esgar

Justin Esgar is an IT rockstar and an “all around good guy” who we follow. Justin is the host of All Things MSP podcast, where he provides valuable business strategy tactics with Eric Anthony. You’ll find the episode on How One Toxic Client Changed My MSP Approach very inspirational. Maybe you can relate, too? 

Follow Justin on LinkedIn

Luis Giraldo

Luis Giraldo is the  Chief Evangelist of ScalePad and host of MSP Confidential podcast. Be sure to check out the episode on Turning Around an Unprofitable MSP, where you’ll pick up golden nuggets on various pricing models and strategies. The Pumpkin Plan for MSPs is another episode we truly enjoyed. 

Follow Luis on LinkedIn

Jeffrey Newton

Jeffrey Newton is an 18-year MSP veteran and Host of the MSP Insider Show, where he has interviewed some of the top names and minds in the industry. Check out his Whiteboard Series for some hidden gems you won’t want to miss out on.  

Follow Jeffrey on LinkedIn 

Damien Stevens

Damien learned how to build an MSP the hard way, from losing a client’s data. Damien is the CEO of Servosity and the Host of MSP Mindset podcast. Damien isn’t afraid to share his journey and past experiences with others who have also built successful MSP businesses, from the ground up. Learn how an MSP retains clients for decades and why niching down is your best bet. Top MSPs share their secrets with Damien. 

Follow Damien on LinkedIn 

Kyle Christensen

Kyle Christensen is the Co-Founder of Empath and is a master of sales. Empath provides a bunch of valuable resources and templates that MSPs can use for sales processes and QBRs.  Get the scoop on how to grow your MSP with Kyle. 

Follow Kyle on LinkedIn 

Stay in the MSP Circle with Guardz 

Guardz helps MSPs overcome daily operational challenges by translating security outcomes into measurable business impact

Follow Guardz on LinkedIn to keep up with the latest MSP industry trends, valuable growth insights, and strategies to build a long-term sustainable business.

Make sure you hit that subscribe button! 

Learn more about the Guardz AI-native Unified Detection and Response platform here. 

About Guardz
Guardz is on a mission to create a safer digital world by empowering Managed Service Providers (MSPs). Their goal is to proactively secure and insure Small and Medium Enterprises (SMEs) against ever-evolving threats while simultaneously creating new revenue streams, all on one unified platform.

About Version 2 Limited
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

Deep web vs dark web: Key differences business and security teams need to know

Deep web vs dark web

Summary: Uncover the critical differences between the deep web and dark web, understand their cybersecurity risks, and learn why proactive monitoring is essential to protect your business from modern cyber threats.

The internet is far more than the visible web. Like the mass of an iceberg, most information and web pages lie below the surface.

The hidden corners of the web can be “deep” – buried beneath the surface, but easy to uncover. However, they can also be “dark” – allowing criminal activity to flourish without surveillance.

Understanding the difference between the deep web and the dark web could be critical to your enterprise cybersecurity. This article will explain how the deep and dark web differ and provide valuable tips for securing sensitive data.

What is the deep web?

The deep web includes web content that is not indexed by search engines. This may seem trivial, but it amounts to vast amounts of data.

For instance, Google appears comprehensive. However, its web crawler index is less than five percent of the World Wide Web. The rest remains on the deep web, and you can’t reach it via traditional search engine results.

Pages on the deep web include password-protected sites like private databases, internal company pages, academic journals, and medical records. Web browsers can often access these pages with the correct credentials, but search engine crawlers cannot process them.

Most deep web content is not malicious. Universities and medical providers need to keep confidential content out of the public eye. Website owners often use the robots.txt file to manage traffic and determine what data search engines can access.

The critical takeaway when comparing deep web vs dark web content is that the deep web is publicly accessible without special browser tools. Anyone with the right credentials can gain access. That’s why criminals prefer the more private environment of the dark web.

What is the dark web?

The dark web is a section of the deep web protected by multiple layers of encryption.

Users can only access dark web servers via special browsers like Tor (the Onion Router). The Tor browser uses randomization to route traffic through virtual tunnels before granting access. This architecture anonymizes users and complicates dark web monitoring.

Ordinary browsers cannot access dark web sites due to unique registry operators. Web crawlers cannot penetrate the encryption protecting dark web servers. Without Tor or other specialist tools, access is impossible.

The dark web emerged in 2000 as a decentralized platform for anonymous communication. In theory, it remains a valuable tool – enabling secure communication for whistle-blowers and individuals in repressive states. However, it has also become a haven for illegal activities.

Dark web marketplaces allow data thieves to sell credentials and other sensitive information. Hackers plan data breaches on dark web forums, while merchants sell many types of illegal goods to customers worldwide.

What is the surface web?

Both the dark web and the deep web exist beneath the surface web. The surface web includes websites indexed by search engines like Google or Bing.

For most internet users, the surface web is all they see. However, the visible web is only a small fraction of all web traffic. 90–95% of web content is submerged and wholly or partially inaccessible via browsers like Google Chrome.

Layers of the web

Deep web vs dark web: key differences

The table below provides a quick deep web vs dark web comparison to understand the differences between the two:


Deep web

Dark web

Access method

Accessible via normal web browsers.

Only accessible via special tools (such as the Tor browser or the Invisible Internet Project)

Size

Massive, containing more than 90% of the internet, consisting of hundreds to thousands of exabytes of data, eclipsing both the surface web and dark web.

Relatively small subset of the deep web, estimated at 0,01–5% of the total internet or around 150,000 websites, with only a few thousand unique sites globally.

Visibility

Visible to web browsers, provided users have the appropriate credentials.

Invisible to ordinary web browsers due to strong encryption.

Threat level

Relatively low. Deep web content may include confidential data, requiring robust access controls and encryption. However, most content is benign and carries a low threat level.

High. Criminal collectives routinely use dark web sites for illegal activities like planning cyber attacks, sharing leaked credentials, and selling exploit or ransomware-as-a-service kits. If credentials appear on dark web forums, companies should anticipate their use in future attacks.

Legal exposure

Low. Companies often use the deep web in everyday operations. Deep web sites may host illegal content (such as torrents). However, using the deep web for legitimate reasons is uncontroversial.

Many dark web sites carry a high legal risk due to illegal activities. Using Tor to browse the dark web is legal, although participation is not advisable.

Why the difference matters for businesses

The differences above matter for one core reason: the dark web functions as a clearinghouse for illegal activities. Cyber threats hatched on the dark web steal data, disrupt business operations, and lead to severe regulatory and reputational damage.

Attackers may collaborate on dark web forums to share information and create sophisticated phishing campaigns, use off-the-shelf exploit kits to leverage backdoors, or mobilize stolen login credentials in brute-force attacks.

This situation challenges risk analysts and security teams to discover leaked credentials and gather threat intelligence. Companies need to update their threat prevention techniques to monitor dark web environments.

Dark web threats also pose a critical compliance challenge. Regulators penalize businesses that put customer data at risk. Data protection increasingly requires active dark web monitoring to manage compliance risks.

These factors make integrating dark web security into your risk management strategy critical. Security teams need to upgrade their capabilities. Analysts need security tools to track dark web activities, while engineers must implement alerting systems and controls to counter threats before they escalate.

How to monitor dark web activity for business security

The next cybersecurity threat to your critical systems and data could be incubating on the dark web as you read this. Without visibility and dark web intelligence, security teams can only wait and hope their network defenses are sufficiently robust.

Fortunately, monitoring solutions work around this problem, giving security analysts advanced warning of dark web discussions and potential threats.

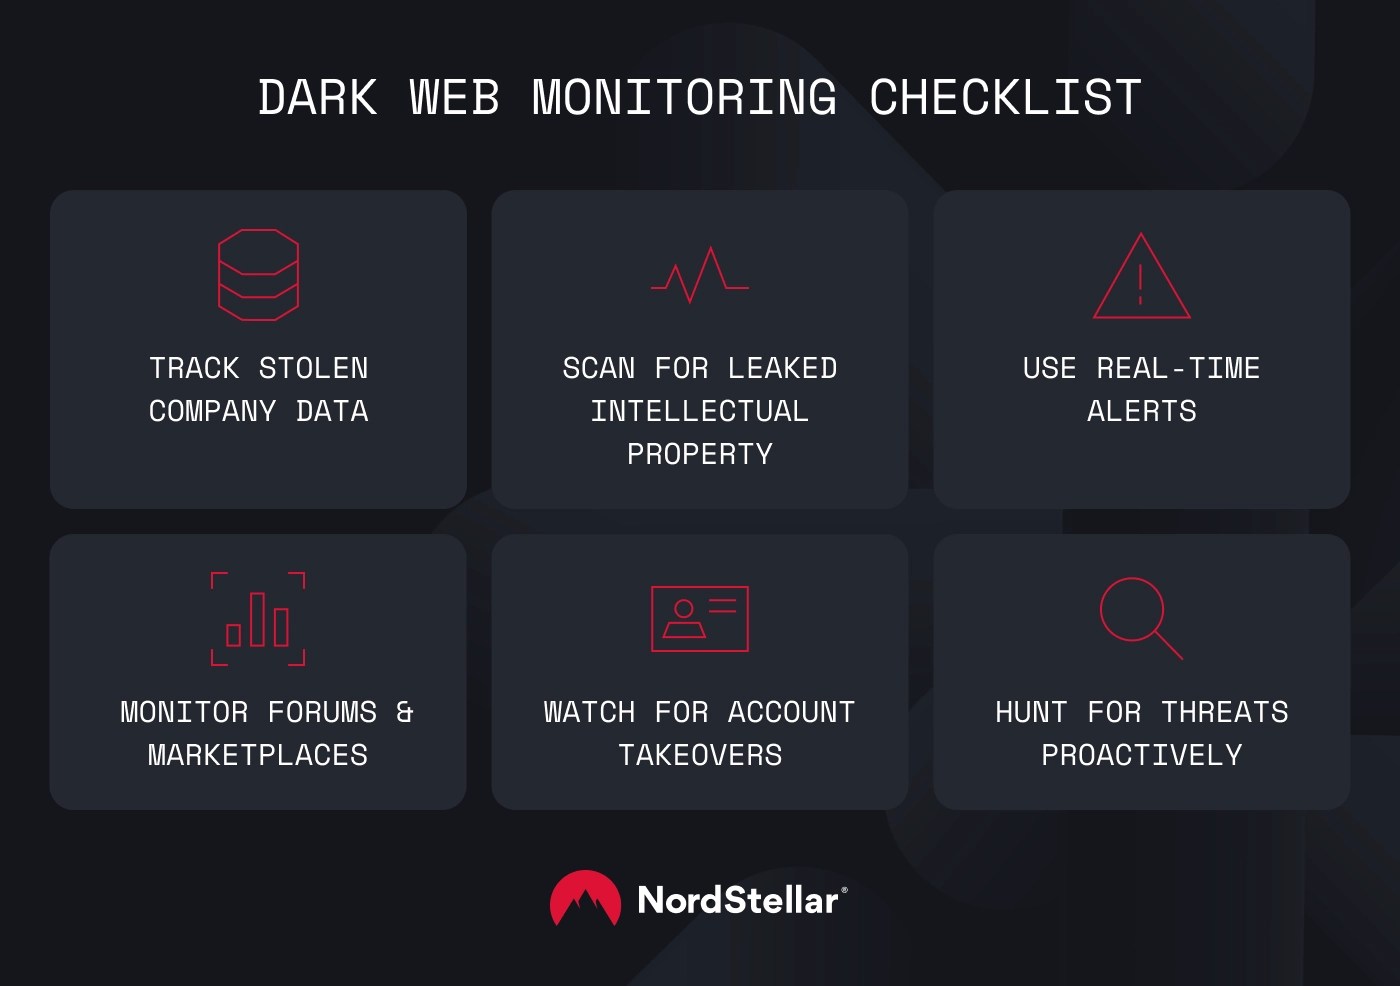
Dark web monitoring checklist

Dark web monitoring tools search for your information. They detect stolen employee logins, customer data, postal addresses, social security numbers, and other valuable personal data relating to your business operations.

Monitoring tools can also scan for intellectual property and other confidential information, helping you manage the threat posed by malicious insiders and corporate espionage.

Moreover, dark web monitoring happens in real time. Monitoring tools detect compromised data and automatically generate alerts. Security teams gain time to mitigate potential threats (for example, by requesting password changes for affected users).

NordStellar’s threat intelligence platform is a great example. Data breach monitoring continuously tracks marketplaces and forums, informing security teams when sensitive data appears on the dark web. Meanwhile, account takeover prevention monitors privileged employee and customer accounts for stolen credentials or suspicious activity. Active scanning identifies hijacks at an early stage before damage results.

Security analysts can also use monitoring tools for threat-hunting expeditions. Cyber threat intelligence helps analysts learn about active groups and attack techniques – generating research outcomes to improve the company’s security posture.

Companies should actively monitor the dark web for security threats. However, it’s important to stress that not all security actions on the dark web are legally safe or advisable from an ethical perspective.

Firstly, we should clarify what is legally permitted when investigating dark web threats. Using Tor and accessing dark web servers is legal. Companies can passively monitor activity and data sales on dark web marketplaces.

There’s nothing wrong with simply accessing dark web sites. Most countries allow free access, although the Tor browser is illegal in China, Russia, and Iran.

However, engaging with threat actors on the dark web creates risks wherever you are. Exposed investigators could receive inaccurate information or provoke cyberattacks. If discovered, automated scanning tools could mark companies as targets for reprisals by criminal groups.

Investigators could also accidentally encounter illegal content while browsing marketplaces and forums. This creates a legal risk (possession of harmful images or confidential data). Monitoring dark web forums also poses ethical questions.

For instance, should you continue to monitor forums despite knowing they host illegal transactions? Or should you inform law enforcement agencies and trust them to intervene?

These operational, legal, and ethical issues make clear policies about accessing the dark web are critically important. Security teams (and anyone else tasked with dark web access) should know how to do so safely – and how to report legal queries if they arise.

We would also advise consulting your legal team when writing dark web security policies. Legal advice ensures you stay on the right side of the law while benefiting from dark web threat monitoring.


Incident examples: When corporate data hits the dark web

The dark web is more than a distant threat hidden deep within the internet. As a couple of real-world examples show, it’s an active site for the preparation and monetization of cyber attacks.

AT&T’s unexpected dark web data breach

In March 2024, communications giant AT&T discovered that 76 million customer records were being sold via dark web marketplaces. The data included SSNs, home addresses, and login credentials of current and past clients.

Although a vast database was available for sale, the company stated that it had found no evidence of data breaches. This highlights the need for proactive monitoring that anticipates breaches, not waiting for the symptoms of cyber attacks.

LinkedIn: An entire social media ecosystem exposed on the dark web

Social media platforms have also suffered dark web data breaches. In 2021, LinkedIn disclosed the exposure of 700 million user records. The data included phone numbers, email addresses, and other personally identifiable information – a gold mine for phishers.

In this case, attackers leveraged code flaws in the platform’s API, allowing them to scrape confidential information about users and their connections.

Although the company has not disclosed details of the impact, the incident likely dented LinkedIn’s reputation as a trusted platform for networking and professional communication. It may also have influenced a gradual decline in ad revenue, harming the platform’s finances.

Colonial Pipeline: Using the dark web as a market for RaaS products

The 2021 Colonial Pipeline ransomware attack shut down a critical energy pipeline on the Eastern Seaboard, leading to a $4.4 million ransom payment. Attackers used stolen employee credentials to access an unused Virtual Private Network account that remained accessible and active.

The critical facts are that attackers used stolen credentials purchased on the dark web. Attackers also used a ransomware-as-a-service (RaaS) kit supplied by the DarkSide collective via dark web marketplaces.

Proactive threat intelligence gathering may have enabled Colonial Pipeline to detect attack planning and locate stolen credentials. However, the company relied on legacy security systems and did not account for dark web threats.

Final thoughts on managing deep and dark web exposure

The surface web is deceptive. Underneath lies a bottomless ocean of deep web content. And within that ocean, the protected dark web provides a secure refuge for illegal activities.

As we’ve learned, these illegal activities could target your company. Data from your employees or customers could be changing hands on dark web marketplaces while criminals build phishing profiles or plan data theft attacks.

Managing deep and dark web exposure is now a fundamental online safety requirement. Security teams should assume their data is available via onion sites and use monitoring platforms like NordStellar to verify the degree of exposure.

Dark web monitoring complements access controls, network segmentation, and intrusion detection and response tools. Dark web intelligence and endpoint protection protect against hidden threats, while employee training helps manage phishing risks.

Ready to strengthen your defenses against hidden online threats? Don’t wait for a breach to act – contact the NordStellar team today and proactively update your data security strategy.


About NordStellar
NordStellar is a threat exposure management platform that enables enterprises to detect and respond to network threats before they escalate. As a platform and API provider, NordStellar can provide insight into threat actors’ activities and their handling of compromised data. Designed by Nord Security, the company renowned for its globally acclaimed digital privacy tool NordVPN.

About Version 2 Limited
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

Portnox Unleashes Fast, Frictionless, Cloud-Native ZTNA

Secure Access, Simplified. No Agents, No Clients, No Passwords—No Problem.


AUSTIN, TX, July 8, 2025 — Portnox, a leading provider of cloud-native access control solutions, today announced the launch of its innovative Zero Trust Network Access (ZTNA) solution. In today’s distributed work environment, employees require access to critical applications from various locations and devices, often over untrusted networks. This expanded threat landscape presents significant security challenges for IT teams. To support rapid adoption, Portnox is also introducing a free version of its ZTNA solution—offering access for unlimited users to an unlimited number of web-based applications.

Legacy ZTNA deployments are notorious for sluggish performance, bloated agents, and deployment headaches that rival traditional VPNs. Purpose-built for agility and simplicity, Portnox’s latest innovation eliminates the friction, lag, and complexity that have come to characterize conventional ZTNA and VPN architectures. Portnox ZTNA offers a unified access control approach, delivering secure remote access to any web-based application without the traditional complexities and exposures.

Leveraging modern zero trust principles, Portnox ZTNA extends robust security capabilities to the application layer, ultimately simplifying IT operations.

Key Advantages of Portnox ZTNA:

  • Instant Access with Minimal Latency: Delivers blazing-fast, high-performance connectivity to internal applications—no lag, no waiting—ensuring users remain productive without the sluggish delays common in legacy ZTNA and VPN solutions.
  • No Client or Agent Required: Users access internal web applications via standard browsers and familiar URLs, eliminating the need for legacy clients.
  • Passwordless Authentication: Provides seamless and secure access, removing the burden and risk associated with passwords.
  • Role- and Location-Based Access Controls: Ensures users can only access the resources they need, based on their role and location.
  • Endpoint Risk Posture Checks: Continuously verifies the security compliance of devices before granting access.
  • Automated Remediation: Instantly addresses non-compliant or risky endpoints.
  • Zero Network Impact: Requires no configuration changes to remote worker networks or corporate firewalls. All connections are outbound-only, simplifying secure access and minimizing the attack surface.
  • Access to Web-Based Applications: Provides secure remote access to web-based applications.

“Portnox ZTNA fundamentally changes how organizations approach remote access security,” stated Denny LeCompte, CEO of Portnox. “We’ve engineered a solution that not only significantly strengthens security but also enhances the user experience—because the best security is virtually invisible: fast, seamless, and frictionless. By eliminating the reliance on traditional VPNs and streamlining access controls, we empower businesses to embrace a true zero trust model with remarkable simplicity.”

Portnox ZTNA offers a modern, secure alternative to traditional VPNs for accessing web-based applications. It establishes a secure, outbound-only tunnel, eliminating the need for VPN clients or complex firewall modifications. This approach simplifies secure remote access without compromising security or user experience.

While today’s launch focuses on delivering high-speed, passwordless access to web-based applications, Portnox ZTNA is only just getting started. Future releases will broaden the scope of the solution to encompass secure zero trust access to a wider array of enterprise resources—including legacy applications with no web client. This continued expansion reflects Portnox’s commitment to providing holistic, cloud-native access control for every user, device, and application—no matter where they reside.

Portnox ZTNA is a core component of the Portnox Unified Access Control Platform, which also includes RADIUS authentication, Network Access Control (NAC), and TACACS+, delivered in a single, cost effective, cloud-native solution. Together, these capabilities provide organizations with a centralized, highly scalable ecosystem for managing and enforcing zero trust access across modern hybrid environments.

The free version of Portnox ZTNA—available now—enables organizations to securely connect unlimited users to unlimited web-based applications. While this free offering includes only community support , organizations can upgrade to Enterprise Support and access all to-be-released features. To use the free version, installation of Portnox’s lightweight endpoint posture assessment tool, AgentP, is required.

Who Benefits from Portnox ZTNA?

  • End users enjoy fast, seamless, secure access to applications and data without cumbersome VPNs.
  • IT decision-makers gain enhanced control and visibility over access attempts and enforce identity-based policies.
  • Organizations across industries like finance, healthcare, education, and technology benefit from robust security and streamlined access management.

To learn more about Portnox ZTNA, visit: /portnox-cloud/ztna/ 


About Portnox
Portnox provides simple-to-deploy, operate and maintain network access control, security and visibility solutions. Portnox software can be deployed on-premises, as a cloud-delivered service, or in hybrid mode. It is agentless and vendor-agnostic, allowing organizations to maximize their existing network and cybersecurity investments. Hundreds of enterprises around the world rely on Portnox for network visibility, cybersecurity policy enforcement and regulatory compliance. The company has been recognized for its innovations by Info Security Products Guide, Cyber Security Excellence Awards, IoT Innovator Awards, Computing Security Awards, Best of Interop ITX and Cyber Defense Magazine. Portnox has offices in the U.S., Europe and Asia. For information visit http://www.portnox.com, and follow us on Twitter and LinkedIn.。

About Version 2 Limited
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.
How to Maximize the Value of Your CMDB

A Configuration Management Database (CMDB) constitutes the backbone of IT Service Management (ITSM). It is a comprehensive map of the IT infrastructure that enables organizations to manage IT resources more efficiently, ensure compliance, and make informed decisions. 

Despite its proven importance, many organizations fail to fully exploit the potential of their CMDB, and this tool risks transforming from a strategic resource into a source of frustration and inefficiency. The truth is that having a poorly utilized CMDB solution or one unsuited to business needs can be worse than not having one at all. 

Inaccurate or obsolete data leads to wrong decisions, slows down incident resolution, and reduces user satisfaction. However, when properly used and maintained, a CMDB simplifies ITSM operations and offers countless benefits. 

Understanding the Role of the CMDB 

Fundamentally, a Configuration Management Database functions as a central hub for storing and organizing detailed information about the elements that make up an IT environment. These elements, both tangible and intangible, support service delivery and infrastructure stability. 

Key Components of a CMDB 

Configuration Items (CI): these are unique entries that represent physical or logical IT resources or services. Each CI is cataloged with distinctive attributes, such as version, owner, and lifecycle status. 

Systemic interactions: a distinctive feature of any effective CMDB is its ability to describe how different components interact with each other. 

Descriptive metadata: information associated with each element, such as deployment environment, maintenance schedule, or ownership. Metadata enhances usability and enables accurate queries. 

Difference Between CMDB and Asset Management 

Although they sometimes overlap, CMDB and Asset Management systems have different objectives. Asset Management is aimed at financial oversight and contractual aspects of IT resources, such as purchase dates and depreciation, while a CMDB is oriented toward understanding system behavior and service architecture. Together, the two offer a comprehensive view of IT resources, but it is the CMDB that provides the information necessary for efficient incident resolution and planning. 

With a properly managed CMDB, IT teams gain meaningful insights into how infrastructure components are connected to each other, enabling more informed decision-making and smoother operations. This foundational knowledge is essential for adopting practices that enable real value from the investment. 

Get the latest ITSM insights! Explore AI, automation, workflows, and more—plus expert vendor analysis to meet your business goals. Download the report now!

CMDB Implementation: The Most Common Pitfalls 

Today many CMDB initiatives fail to live up to expectations. This discrepancy between reality and expected performance is rarely due to inadequate technologies. Much more often, it is the result of underestimated operational challenges and execution not aligned with real business needs. Recognizing the most common pitfalls can help organizations fully exploit their CMDB’s potential by adopting proactive measures in a timely manner. 

The recurring reasons why many organizations fall into the trap of underutilizing their CMDB are: 

  • Lack of clear objectives: implementing a CMDB without defined purposes leads to abnormal expansion of the scope of application and data overload. 
  • Poor accuracy and data inconsistency: obsolete or incomplete data concerning CIs undermines trust in the CMDB. This is why regular audits and automated detection are essential. 
  • Overly complex mapping: trying to map every CI and every relationship from day one adds unnecessary complexity and increases the risk of errors. 
  • Manual processes more easily subject to errors: relying on manual updates slows down teams and introduces discrepancies. 
  • Integration with other IT systems: seamless connectivity with monitoring, asset, and ITSM tools often requires advanced customization, which requires significant expertise to achieve. 
  • Insufficient governance and ownership: without clear definition of responsibilities between teams, CMDB maintenance quickly ends up being neglected. 
  • Lag behind the evolution of the IT landscape: with the proliferation of cloud, containers, and microservices, the CMDB must adapt or risks becoming irrelevant. 

Recognizing these critical issues is the first step toward adopting CMDB best practices and improving its performance. By addressing these problems with a clear strategy, robust tools, and continuous stakeholder engagement, organizations can get the most out of a CMDB while improving operations. 

Best Practices for Maximizing CMDB Value 

To fully exploit the potential of a configuration management database, organizations must go beyond simply implementing the tool and adopt a strategic approach. CMDB best practices are aimed at making the database accurate, relevant, and aligned with broader IT and business objectives. They are fundamental for maximizing its value and avoiding the most frequent errors. 

Define clear objectives: start small and scale gradually. Begin with a clear articulation of why a CMDB is needed and the expected business outcomes. It’s a “start-small” philosophy: first model only the most critical services, applications, or servers, demonstrate their value, and then expand to include network devices, databases, and the rest of the assets as the process matures. 

Establish solid governance, ownership, and stakeholder engagement. Governance remains the keystone of a reliable CMDB, but it must extend beyond IT operations. If the database is to reflect the organization’s real priorities, it is essential to designate those responsible for data management, service owners, and CMDB managers and actively involve stakeholders from security, finance, and business departments. 

Automate data collection and updating. Replace error-prone manual entry with automatic detection and integration tools that identify CIs and update attributes and lifecycle status in real time. It’s good practice to connect the CMDB to monitoring platforms, IT asset management, cloud service providers, and DevOps pipelines so that changes are captured the moment they occur. 

Focus attention on data quality: verify, refine, repeat. Evaluating data quality is not a one-time activity. It’s necessary to define standards for naming, classification, and mandatory attributes; validate data at every acquisition point; perform scheduled audits to detect obsolete or conflicting entries. It’s better to use dashboards to monitor completeness, accuracy, and timeliness, so you can act before quality deteriorates. 

Define clear CI relationships and categories. The true power of a CMDB lies in understanding how components interact with each other. Categories and naming conventions must be consistent to make the data model intuitive, easy to query, and ready for impact analysis. 

Seamless integration with ITSM processes. Incorporating the CMDB into incident, change, problem, and release workflows ensures that every ticket is enriched with current configuration data and technicians can immediately assess upstream or downstream impact. 

Monitor, measure, and communicate performance. Monitoring metrics such as CI accuracy, update frequency, change success rate, and mean time to incident resolution serves to have a precise measure of the value produced and identify optimization opportunities. 

Foster a culture of continuous improvement. Encouraging feedback, keeping documentation updated, investing in continuous training, and reviewing governance policies as technology and the business evolve means, essentially, treating the CMDB as a living system in constant evolution. 

Real Benefits of CMDB Optimization 

A CMDB is at the foundation of the entire service management lifecycle. When governed by the practices we have described, the CMDB can evolve to strengthen every aspect of ITSM. The benefits are evident. 

Holistic oversight and greater efficiency: by collecting detailed information about infrastructure and services in one place, teams gain a reliable end-to-end perspective, useful for planning upgrades or tracking problems. Identifying underutilized or duplicate resources helps reduce waste for greater efficiency. 

Faster incident response: the resource map stored in the CMDB reveals at a glance which business applications or services are impacted when a component malfunctions. This broad and detailed view accelerates classification, reduces downtime, and improves customer satisfaction. 

Greater risk awareness in case of changes: before implementing a patch or update, teams can perform real-time assessments of change impact, drastically reducing the likelihood of unexpected interruptions, enabling smoother workflows and a higher degree of preparation for audits. Accurate change impact analysis reduces downtime. 

Faster root cause identification: for persistent or recurring problems, historical configuration snapshots reveal which patterns repeat and allow identification of underlying causes. This makes it possible to intervene to implement lasting solutions instead of ineffective ones. 

To achieve these results requires continuous management, cross-functional collaboration, and constant commitment to improvement. In this context, technology can prove to be an extraordinary enabling element supporting change. 


About EasyVista  
EasyVista is a leading IT software provider delivering comprehensive IT solutions, including service management, remote support, IT monitoring, and self-healing technologies. We empower companies to embrace a customer-focused, proactive, and predictive approach to IT service, support, and operations. EasyVista is dedicated to understanding and exceeding customer expectations, ensuring seamless and superior IT experiences. Today, EasyVista supports over 3,000 companies worldwide in accelerating digital transformation, enhancing employee productivity, reducing operating costs, and boosting satisfaction for both employees and customers across various industries, including financial services, healthcare, education, and manufacturing.

About Version 2 Limited
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

Protecting ePHI in the Cloud

Protecting ePHI in the Cloud: HIPAA-Compliant Cloud Backup Strategies for US Healthcare

Managing electronic protected health information (ePHI) in the cloud has become necessary as healthcare organizations progressively choose cloud technologies. This method raises data remote access, cost-effectiveness, and accessibility.

However, it also comes with compliance and security issues. Failing to protect ePHI, even in backups, for covered entities under the Health Insurance Portability and Accountability Act (HIPAA) runs a risk of significant fines, legal action, mistrust development, and damage to patient relationships.

Thus, providers must ensure that their backup plans are safe, tested, and monitored closely against government rules. This post explores the most practical approaches and insights relevant to U.S. healthcare institutions.

HIPAA Requirements for Backing Up ePHI

ePHI protection is governed by the Health Insurance Portability and Accountability Act (HIPAA). This act also specifies how ePHI must be backed up and recovered should a disaster or failure strike. HIPAA outlines critical backup-related criteria but does not specify certain technologies:

  • Procedures must be in place for data backup to generate and preserve exact, retrievable copies of ePHI.
  • In data recovery plans, organizations must specify how ePHI would be rebuilt following a cybercrime, system outage, or natural disaster.
  • Critical systems must be able to operate in emergency conditions to protect data integrity in emergency mode plans.
  • Backup and recovery strategies must be routinely tested and changed depending on changing risk.
  • Only authorized staff members should access ePHI; audit trails are in place to track interactions.

Meeting these criteria in a traditional on-premise solution is tough enough. In a cloud-based setting, the stakes are even higher, and the strategies more complex.

On-Prem vs. Cloud Backup for HIPAA

Feature On-Prem Backup Cloud Backup 
Initial Cost High (hardware, staffing) Lower (subscription model) 
Scalability Limited by physical resources Virtually unlimited 
Maintenance Manual, resource-intensive Managed by CSP 
Redundancy May require a separate off-site site Built-in multi-region redundancy 
Disaster Recovery Requires dedicated DR planning Often included with DRaaS 
Physical Security Controlled by the IT team Dependent on CSP’s data center practices 
BAA Requirement Not applicable Mandatory with CSP 
Compliance Flexibility Complete control, slower changes Fast updates, shared responsibility 


Cloud backup offers greater flexibility and cost efficiency. However, it shifts part of the security responsibility to your provider. Vetting and partnering with the right cloud service provider (CSP) is critical.

Why Cloud Backup Requires Special Attention

Cloud backup offers agility and cost savings, but it also brings new levels of complexity, especially around shared accountability. Many healthcare businesses wrongly assume their cloud provider manages HIPAA compliance by default. In truth, compliance is a joint effort.

Cloud-specific risks include:

  • Multi-tenancy: Data hosted on shared infrastructure increases exposure.
  • Remote Access: Greater accessibility can lead to increased attack surfaces.
  • Data Sovereignty: The physical location of your data may affect compliance with US regulations.

Understanding your and the provider’s roles is crucial for protecting ePHI.

How to Build a HIPAA-Compliant Cloud Backup Strategy

An effective cloud backup plan has to be proactive, tested several times, and compliant with HIPAA. Here’s how you approach it:

Choose the Right Cloud Provider

Not every cloud vendor is prepared to meet HIPAA’s requirements. You’ll need a provider that:

  • Offers a signed Business Associate Agreement (BAA)
  • Demonstrates a proven track record with healthcare clients
  • Provides transparent security practices and compliance certifications

Seek vendors with industry-standard certifications, including HIPAA, HITECH, and SOC 2 Type II.

Encrypt Data at All Times

HIPAA necessitates the safeguarding of ePHI both at rest and in transit. This means

  • Enabling AES-256 encryption for stored backups
  • Using TLS or SSL protocols for data transfer
  • Implementing secure key management systems

This ensures that the data remains unreadable even if unauthorized actors access backups.

Ensure Data Redundancy and Availability

Cloud backups must be:

  • Geo-redundant in order to withstand regional outages.
  • Supported by Recovery Point Objectives (RPOs) and Acceptable Recovery Time Objectives (SLAs) specifications.
  • Capability of automatic and frequent backups with choices for long-term storage.

Redundancy isn’t just a performance booster; it’s a compliance measure.

Implement Strong Access Controls

Unauthorized access is one of the most common causes of HIPAA breaches. Limit exposure by:

  • Using Role-Based Access Controls (RBAC) to grant access based on job roles
  • Enforcing the principle of least privilege
  • Deploying Multi-Factor Authentication (MFA) for cloud portal access
  • Logging and auditing all interactions with backup systems

This creates a controlled, traceable environment around your sensitive cloud data.

Conduct Regular Testing and Validation

A backup that doesn’t work is a liability. HIPAA requires regular testing and revision of all backup and disaster recovery procedures. Best practices include:

  • Simulating disaster scenarios to test recovery speed and integrity
  • Documenting results and updating policies accordingly
  • Involving IT and compliance teams in every phase of the testing process

Testing ensures that your cloud-based recovery plan isn’t just theoretical—it’s reliable when needed.

Common Pitfalls to Avoid

Even well-intentioned organizations can fall into traps that undermine their HIPAA backup strategy. Watch out for these frequent mistakes:

  • Assuming all cloud storage is HIPAA-compliant. A vendor’s offering of encryption or redundancy does not automatically satisfy all compliance criteria.
  • Failing to sign a business associate agreement (BAA) means your cloud provider is not legally obligated to follow HIPAA.
  • Using consumer-grade backup tools. For instance, the Standard edition of Dropbox or Google Drive lacks the restrictions required for healthcare data and isn’t built for HIPAA compliance.
  • Ignoring backup monitoring calls for regular validation of completion, integrity, and accessibility.

Steering clear of these traps calls for diligence, teamwork, and vendor responsibility.

The Role of Immutable Backups and Air-Gapping

Healthcare organizations should consider including immutable backups (copies of data that cannot be changed or deleted for a designated period) for extra security. These backups can stop ransomware attackers from either encrypting or destroying recovery information.

In tandem, air-gapping techniques (storing backups in physically or logically separated environments) offer another layer of protection. Appropriately utilized techniques enable you to keep HIPAA compliance even in worst-case situations.

To Sum Up: Compliance is a Continuous Process

Adoption of cloud backup systems only modifies your HIPAA responsibilities rather than absolving them. Protecting ePHI in the cloud calls for a well-crafted backup plan that strikes a compromise between security, performance, and compliance.

To recap, a HIPAA-compliant cloud backup strategy should:

  • Built with a vetted provider that offers a BAA
  • Include encryption, access controls, and redundancy.
  • Be tested and monitored regularly.
  • Align with HIPAA’s administrative, physical, and technical safeguards

Cloud backup compliance reflects your company’s dedication to data protection, patient safety, and regulatory responsibility, more than just a checkbox. Your patients and operations will be less vulnerable in the face of growing risks, the more solid your plan is.

About Storware
Storware is a backup software producer with over 10 years of experience in the backup world. Storware Backup and Recovery is an enterprise-grade, agent-less solution that caters to various data environments. It supports virtual machines, containers, storage providers, Microsoft 365, and applications running on-premises or in the cloud. Thanks to its small footprint, seamless integration into your existing IT infrastructure, storage, or enterprise backup providers is effortless.

About Version 2 Limited
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.
Cybersecurity as a Business Enabler – CISO’s Driving Business Value, Productivity, and Cost Efficiency

For many organizations, cybersecurity has historically been seen as a necessary expense, like an insurance policy, rather than a strategic investment. But that outdated mindset is shifting rapidly. In today’s hyper-connected world, effective security is a business enabler. It accelerates digital transformation, safeguards productivity, protects revenue, and, when approached strategically, drives measurable cost savings in cybersecurity.

Forward-thinking organizations are now optimizing their cybersecurity budget through smarter investments, tool consolidation, and security automation, transforming security from a cost center into a value driver.

As one security leader put it:

“The conversation changes when you translate security risks into business terms such as business downtime, revenue impact, regulatory exposure. That’s when security becomes not just about protection, but a core part of how the business stays productive and competitive.”

‍

Beyond Protection: Enabling Business Continuity and Resilience

Security teams are often asked to report on patch rates, incident detection times, or technical vulnerabilities. These metrics, while important for the security team, rarely resonate at the executive or board level unless translated into business outcomes.

The real question executives care about is simple: “If something goes wrong, how quickly can we detect it, contain it, and recover, and what does that mean for the business?”

Containing an incident quickly can be the difference between a minor disruption and a multi-million-dollar crisis. One security leader drew a parallel from their experience in emergency services:

“When somebody calls the emergency number, how quickly can you get help to that person, which can be the difference between life and death? That’s a massive service-level commitment. It’s the same with cyber incidents. Faster detection and response mean reduced impact and faster recovery.”

This is why modern security strategies emphasize not just prevention, but detection, containment, and recovery, all directly tied to business resilience.

‍

Aligning Security with Business Priorities

The fundamental question executives care about isn’t technical; it’s risk, legal, operational, and financial:

  • How does security help keep services running?
  • How does it reduce risk without slowing the business down?
  • How can we achieve cybersecurity cost savings without increasing exposure?
  • How do we make the most of our cybersecurity budget in a resource-constrained environment?

‍

To answer these, security leaders are embracing risk-based budgeting but prioritizing investments that directly reduce business risk and support critical operations, rather than spreading resources thin across low-impact areas.
‍

“Risk-based budgeting helps us avoid spending on security for security’s sake. It focuses us on what actually protects the business and drives value, leading to a return on investment.”

‍

Tool Consolidation and Security Automation: Doing More with Less

The average enterprise security stack has grown bloated and complex, with overlapping tools, redundant functionality, and spiraling costs. Not only is this expensive, but it also slows response times and creates operational blind spots.  Managing a multitude of tools presents a significant resource challenge, hindering the team’s ability to develop the necessary skills and knowledge for effective oversight and visibility.

‍

Tool consolidation addresses this challenge head-on, streamlining security operations, reducing vendor complexity, and unlocking efficiency gains.
‍

By consolidating platforms and introducing security automation, organizations can:

✔ Reduce tool sprawl and associated costs
✔ Improve visibility and control
✔ Accelerate incident detection and response
✔ Free up security teams to focus on higher-value tasks
✔ Drive measurable cybersecurity cost savings
‍

“Tool consolidation and automation aren’t just about saving money, though they do that. They improve resilience and keep the business moving by making security more efficient and less reactive.”

‍

Legacy Technology Divestment: Reducing Risk and Cost

Outdated, unsupported, or redundant technologies introduce both security vulnerabilities and hidden operational costs. Yet many organizations hesitate to part ways with legacy systems due to perceived complexity or sunk costs.

However, strategic legacy technology divestment delivers significant benefits:

  • Reduced attack surface and security risk
  • Lower maintenance and licensing costs
  • Simplified technology architecture
  • Greater agility and scalability
  • Alignment with modern security and compliance standards

‍

As security leaders increasingly tie technology decisions to business outcomes, shedding outdated systems becomes a key component of both risk reduction and cybersecurity cost savings.

“Clinging to legacy technology isn’t just a technical debt issue; it’s a business risk. And divesting from it is often one of the fastest ways to cut costs and improve security.”

‍

The Domino Effect of Poor Access Management

Many of the most damaging breaches share a common root cause: weak or unmanaged access controls typically related to identities and credentials.

‍

Whether it’s stolen credentials sold for a few dollars on the dark web or privileged access abuse, attackers exploit identity gaps as their easiest entry point. From there, poor internal controls, such as a lack of network segmentation or weak separation of duties, allow them to escalate privileges, move laterally, and access critical systems.

“It’s literally a domino effect. That initial access is the first domino falling. But the last domino could be your ERP system, your customer data, or your intellectual property, and when that last domino falls, the business impact is massive.”

‍

By managing access more effectively, including privileged accounts, third-party access, and machine identities, organizations not only reduce their risk but also improve operational efficiency and simplify regulatory compliance.

‍

Predicting the Shift: Cyber Accountability in the Boardroom

Regulatory changes, such as new disclosure requirements, are forcing security into sharper boardroom focus. Leaders predict that organizations will face tougher scrutiny, not just on whether incidents occur, but on how well access controls, credential management, and privileged user rights are governed.

This creates both a challenge and an opportunity. Security leaders who can proactively frame these controls as business enablers protecting critical services, enabling faster recovery, and safeguarding productivity will be seen not as blockers, but as strategic contributors.

The key is to avoid overwhelming executives with technical details. Instead:

✅ Keep the conversation business-centric
✅ Explain how controls directly support operational continuity
✅ Connect risks and security investments to measurable business outcomes
✅ Demonstrate readiness through realistic scenarios and response plans

As one leader advised:
‍

“There’s going to be a tug of war. In calm times, you keep it macro, business-focused. But in a crisis, boards will dive into the weeds asking detailed questions like, ‘How did we let this happen?’ Be prepared for both.”

‍

The Future of Security as a Competitive Advantage

Modern security isn’t about saying no, it’s about enabling the business to move faster, innovate confidently, and stay productive, all while managing risk.

Organizations that embrace risk-based budgeting, pursue tool consolidation, leverage security automation, and commit to legacy technology divestment are finding they can both improve security and achieve real, measurable cybersecurity cost savings.

Security, when aligned to business goals, does more than reduce risk. It:

✔ Supports faster, safer digital transformation
✔ Enables employees to work productively and securely
✔ Reduces downtime and the financial impact of incidents
✔ Builds customer confidence and market credibility
✔ Enhances the organization’s ability to adapt, recover, and grow
‍

“We’ll never eliminate all risk, but we can align security to the business, reduce costs, improve resilience, and make security a true competitive advantage.”


Bottom Line:
Security isn’t just about protecting the business. It’s about enabling it to operate, innovate, and grow safely, confidently, and with resilience built in.

About Segura®
Segura® strive to ensure the sovereignty of companies over actions and privileged information. To this end, we work against data theft through traceability of administrator actions on networks, servers, databases and a multitude of devices. In addition, we pursue compliance with auditing requirements and the most demanding standards, including PCI DSS, Sarbanes-Oxley, ISO 27001 and HIPAA.

About Version 2 Limited
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.
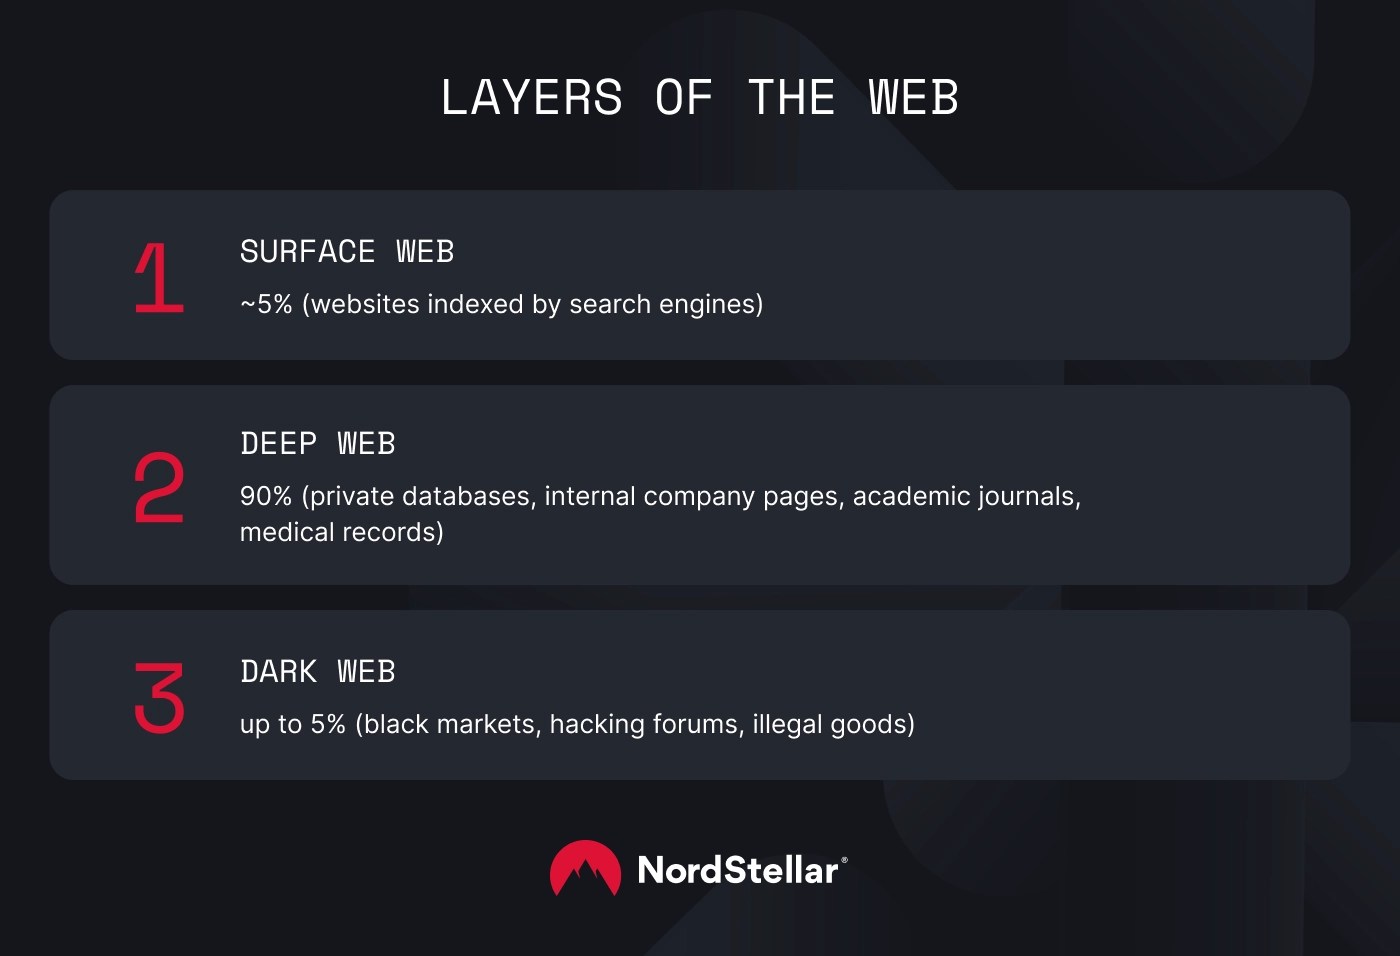
17 Common Indicators of Compromise

On a sunny summer vacation day, your childhood self is running around a playground looking everywhere for a small piece of paper as part of a treasure hunt. Each clue you find leads to another, then another, until you finally locate the hidden treasure. Investigating a security incident is similar to this process, but instead of clues written on paper, your clues are digital artifacts that attackers left in your systems.


These digital artifacts are called indicators of compromise (IoCs). Like every good mystery novel reminds you, every criminal makes a mistake, leaving behind clue. IoCs can be anything from unusual login to unauthorized file changes, the tiny changes to your complex systems that they hope will go unnoticed.


For security teams, knowing the most common indicators of compromise can improve key threat detection and response (TDIR) metrics, like mean time to investigate (MTTI) and mean time to contain (MTTC).


What are indicators of compromise (IOCs)?

Indicators of Compromise (IoCs) are the clues that threat actors leave behind after gaining unauthorized access to systems, networks, and devices. Security teams can search their environments for these clues to confirm a security incident or data breach. By monitoring IoCs in real-time, security teams proactively mitigate risk.


IoCs fall into the following four categories:

  • Network-based: unusual traffic patterns that indicate potential phishing, malware, unauthorized access, or other sophisticated attacks with symptoms like suspicious IP address or malicious domain names
  • Host-based: activities on individual systems or endpoints, like unexpected changes in system settings, processes, or permissions
  • Email-based: signs of phishing or malware in suspicious emails, including malicious attachments, strange email addresses, spoofed sender information, spikes in spam, odd messages from known contacts, or unusual email patterns
  • Behavioral: suspicious user behavior that can indicate an account takeover, like odd login actions or unusual network traffic.
  • Third-party: threat intelligence that provides insight into new and evolving threats, often providing ana application programming interface (API) so security teams can incorporate the data into their security information and event management (SIEM) solution


17 Common Indicators of Compromise

By detecting unusual system behavior as quickly as possible, you can reduce an incident’s severity and potential impact. By looking for these common IoCs, you can take a more proactive approach to security.


1.   Network traffic anomalies

Network traffic anomalies can indicate potential data theft or connection to a threat actor’s command and control (C2) infrastructure. For example, a sudden spike in data transfers can indicate attackers exfiltrating sensitive information.

2.   Unusual sign-in attempts

As part of monitoring user access, you should look for unusual sign-in attempts that can indicate an account takeover attack or credential stuffing attack. Some examples of this behavior include login attempts from unexpected geographic locations or multiple failed logins in a short timeframe.

3.   Geographical anomalies

Most organizations know where their employees work or know their travel patterns. Any geographical anomaly, like user access or server communications, can indicate a potential incident. Additionally, some geographic regions are known to be a haven for cybercriminals, so you may want to focus monitoring for those areas.

4.   Privilege account irregularities

Privileged accounts, both human and machine, have more access to sensitive data, resources, and assets than standard accounts. Attackers target these accounts so they can gain unauthorized access to sensitive information or move laterally across networks.

5.   Changes to systems configurations

To weaken defenses or evade detection, attackers often make unapproved changes to system configurations. For example, these new changes may indicate that malware introduced a backdoor so attackers can maintain their presence in systems and achieve objectives.

6.   Unexpected software installations or updates

Typically, IT departments define the approved software that users can install. When people install unauthorized software, they may be adding malicious applications to devices. When users are unaware of unauthorized downloads, it might be a malware infection that attackers can use to gain unauthorized access or to deploy additional malware, like ransomware.

7.   Numerous requests for the same file

As organizations moved to the cloud, they implemented access controls around resource and file access. Multiple requests for access to the same file can indicate that attackers are attempting to gain initial access or are using unauthorized access to explore networks and systems.

8.   Unusual Domain Name Systems (DNS) requests

Unusual and high volumes of DNS queries can indicate a malware infection and attackers trying to download data, especially when the requests come from unexpected geographic locations. These indicators are most common when attackers install malware on a server and create a connection to their C2 infrastructure.

9.   Swells in database read volume

Increased database read volume can indicate that attackers are exploring your systems to find sensitive data. Before attackers steal sensitive information, they have to explore databases to find it. When attackers attempt to steal this information, their activities will generate a higher read volume than normal.

10.   HTML response sizes

Web applications often have larger HTML response sizes when attackers are trying to deploy an attack against them. For example, in a SQL injection attack, the database connected to the application will try to send more data than usual, increasing the HTML response size.

11.   Mismatched port-application traffic

Applications typically define the accepted ports for transmitting data. For example, ports 0 though 1023 are often used by common, widely used services, like system processes, operating systems, and default applications. If an application is using an usual port, an attacker may be trying to evade detection.

12.   Suspicious registry or system file changes

After gaining an initial foothold, attackers often make changes to registries and system files to establish and maintain persistence. For example, attackers often install additional malware and tools once they have unauthorized system access.

13.   Influx of spam emails

A sudden increase in spam emails can be related to an attack in two different ways. Attackers may compromise an email account and use it to send emails to other employees. Additionally, spam emails are often part of phishing attacks, so a sudden influx of these messages may indicate that attackers are targeting the organization.

14.   Moved or aggregated data

When attackers are preparing to exfiltrate data, they often try to create a collection point to evade detection. With data transferring quickly from one or two locations, security teams may not detect the issues until the attackers complete the process. For example, attackers may try to move files to a recycle bin’s root folders where no one would think to look.

15.   Non-human website traffic

Threat actors often use bots to deploy attacks, like brute force or Distributed Denial of Service (DDoS) attacks. Some indicators of non-human website traffic include:

  • Abnormally high pageviews and bounce rates
  • Anomalous session durations
  • Traffic spikes from unexpected locations

16.   Changes to mobile devices

Attackers increasingly target mobile devices because employees often use them for work. For example, a smartphone that starts running slowly might have a mobile malware on it. If your organization provides and manages mobile devices, looking for configuration changes and new profiles can help identify a potential attack.

17.   System outages or reduced performance

When attackers deploy a DDoS attack, they send high volumes of requests to servers. Clogged with so many requests, the servers are unable to respond, disrupting services. In some cases, threat actors use a DDoS attack to distract security teams so they won’t detect a different attack, like a ransomware deployment.


Graylog Security: Cut Through the Noise with Contextual Risk Scoring

While IoCs provide valuable insight into activities happening across your environment, they often lack context which can lead to false positives. For example, an offline network device could be causing network latency or a system outage, not a DDoS attack. Without context, security teams find themselves investigating alerts that may be unrelated to a security incident or data breach.


Graylog Security’s contextual risk scoring, powered by Detection Chains, amplifies real threat and suppresses the rest. By leveraging threat intelligence and our risk scoring, you can prioritize responded based on asset criticality and connect the dots between alerts to reduce alert fatigue.


To see how Graylog Security gives you the SIEM that never asks you to compromise, contact us today.

About Graylog
At Graylog, our vision is a secure digital world where organizations of all sizes can effectively guard against cyber threats. We’re committed to turning this vision into reality by providing Threat Detection & Response that sets the standard for excellence. Our cloud-native architecture delivers SIEM, API Security, and Enterprise Log Management solutions that are not just efficient and effective—whether hosted by us, on-premises, or in your cloud—but also deliver a fantastic Analyst Experience at the lowest total cost of ownership. We aim to equip security analysts with the best tools for the job, empowering every organization to stand resilient in the ever-evolving cybersecurity landscape.

About Version 2 Limited
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.