Skip to content

Threat intelligence tools: Everything you need to know

Threat intelligence tools: Everything you need to know

Cyber threats aren’t showing any sign of slowing down — and businesses of all sizes are feeling the pressure to keep up. That’s where threat intelligence tools come in. They help turn complex threat data into clear, actionable insights security teams can use to protect their systems and respond faster. In this article, we’ll cover what threat intelligence tools actually do, the features that matter, and how they can support your security strategy — whether you’re a startup or a global company.

What are threat intelligence tools?

Threat intelligence tools are cybersecurity solutions designed to collect, analyze, and deliver information about potential and active threats targeting an organization. These tools provide insights into attacker behavior, indicators of compromise (IOCs), and malware signatures.

It’s important to note that threat intelligence doesn’t come from a single source. It gathers data from internal logs, open-source intelligence (OSINT), commercial feeds, and underground forums. Once the data is collected, it’s organized and turned into useful insights that help your security team make smarter and faster decisions.

Some tools are built for overall monitoring, while others focus on specific use cases like phishing attempts or brand impersonation. Whether embedded into a larger platform or used independently, threat intelligence tools help organizations detect and respond to cyber threats with more context.

If you’re new to the concept of threat intelligence, it’s useful to know that these tools are often part of a broader security picture that helps reduce blind spots across your systems.

How do threat intelligence tools work?

Threat intelligence tools work by constantly collecting and analyzing data from many different sources to spot both known and potential threats. They handle the initial investigative work: gathering raw data, highlighting possible threat actors or attack patterns (when attribution data is available), and presenting the information clearly so your security team can act on it.

The process usually starts with data collection. The tool gathers information from various sources, including OSINT feeds, malware databases, social media, hacker forums, and internal system logs — across different endpoints, networks, and cloud setups. After collecting the data, the tool links details like IP addresses or file signatures to known hackers, attacks, or vulnerabilities.

From there, the cyber threat intelligence is delivered in practical formats: alerts in your SIEM, detailed threat reports, or risk scores inside firewalls and endpoint protection systems. Some platforms even work with attack surface management tools to show where your systems might be exposed.

Many of these tools integrate with incident response systems, automating quick actions — like blocking a domain or isolating a compromised device. This means less time wasted and a faster path from detection to action.

Key features of effective threat intelligence tools

Effective threat intelligence tools collect vast amounts of data and turn it into actionable cyber threat intelligence. The goal is to avoid overwhelming security teams with noise and deliver the right information at the right time in an easy-to-use way. A few key features help the best tools do this well:

Broad data collection

The most reliable cyber threat intelligence tools gather data from a wide variety of sources, including internal telemetry, commercial threat feeds, OSINT, and dark web monitoring channels. Such diversity is key, as it provides a full view of the threats, helping companies identify potential risks before they impact their systems. By pulling intelligence from multiple angles, these tools minimize blind spots and deliver richer insights that reflect the full scope of potential cyber threats.

Real-time alerting and contextualization

Effective tools do more than simply flag suspicious indicators. They add meaningful context to every alert, for instance, spotting threat actor groups, typical attack vectors used, timelines of related incidents, and historical patterns. Providing this context helps security analysts quickly evaluate a threat’s severity and relevance, speeding up response times and reducing alert fatigue. Real-time updates ensure teams can act on the latest cyber threat intelligence without delay, improving overall threat detection and mitigation.

Automated correlation and enrichment

Instead of delivering isolated or raw data points, top-tier tools automatically correlate new IOCs with past activity and enrich them with additional external intelligence. This process involves linking related events, assigning risk scores, and categorizing threats by severity. Automated enrichment helps security teams prioritize the most critical alerts and understand the broader attack context. As a result, it helps support more strategic and effective defense actions.

Integration with existing infrastructure

The best threat intelligence tools integrate with an organization’s existing cybersecurity stack — including security information and event management (SIEM), security orchestration, automation, and response (SOAR) platforms, firewalls, and endpoint detection and response (EDR) solutions. This integration allows valuable threat insights to be delivered directly to the tools security teams use daily, enabling faster detection and response. For companies with complex, layered defenses, smooth integration is essential to maintain operational efficiency and maximize the value of threat intelligence.

Filtering and prioritization

A huge number of threat indicators are generated daily, which is why effective filtering and prioritization features are essential. Quality cyber threat intelligence tools allow teams to customize filters based on severity levels, geographic relevance, industry-specific threats, or particular vulnerabilities within their environment. Doing so reduces noise and ensures that security resources are dedicated to the most relevant risks, which helps companies stay proactive instead of reactive.

Support for threat hunting and forensics

Beyond routine alerts, advanced tools provide access to raw threat data and powerful analytics that help security teams conduct investigations. Threat hunters and incident responders use these features to track suspicious activity, uncover hidden IOCs, study attack patterns, and investigate incidents in detail. Doing so helps uncover sophisticated threats and strengthen overall security.

Reporting and collaboration features

Strong threat intelligence platforms have easy-to-use reports, clear dashboards, and collaboration tools that help security teams in security operations centers (SOCs) work together smoothly. These features enable teams to track upcoming trends, share insights, and document response activities. Collaborative environments also support better decision-making and allow companies to keep on refining their security strategies based on threat data.
About NordStellar
NordStellar is a threat exposure management platform that enables enterprises to detect and respond to network threats before they escalate. As a platform and API provider, NordStellar can provide insight into threat actors’ activities and their handling of compromised data. Designed by Nord Security, the company renowned for its globally acclaimed digital privacy tool NordVPN.

About Version 2 Limited
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

Cyber storage: The new standard for SaaS data protection

In today’s high-risk digital landscape, storing data isn’t enough. You need to protect it—actively, intelligently, and independently. At Keepit, we’ve redefined what data storage means for the cloud era. We don’t just offer storage. We deliver cyber storage: a  built specifically to safeguard your SaaS data from the growing threat of cyber attacks and operational disruption.

Let me explain what that really means—and why it matters. 

Independent and dedicated: The foundation of real resilience 

Independence isn’t a buzzword. It’s a foundational requirement. Most backup solutions today are still entangled in the same infrastructure used for production data—especially when they rely on public cloud providers like Microsoft or AWS. That shared infrastructure model might look convenient on paper, but it creates a single point of failure in practice. 

Keepit is different. We’re . Our cloud doesn’t live inside the same hyperscaler platforms it’s meant to protect you from. We built our own infrastructure from the ground up, and we own every layer—from hardware to application. That means we’re not at the mercy of another company’s supply chain, network behavior, or internal vulnerabilities. 

What does “dedicated” mean in this context? It means that once your data enters a Keepit region, it never leaves that region. Your backups are replicated across two data centers in that region, ensuring not just compliance with data sovereignty but maximum resilience in the face of regional outages. 

Cyber storage = Storage + Protection 

Data storage alone doesn’t equal data protection. Cyber storage does. That’s why Keepit combines long-term, efficient backup storage with built-in, proactive protection mechanisms. 

Our architecture is . Once backup data enters our system, it’s immediately encrypted and can’t be altered—not by us, not by your admins, not by attackers. There’s also a 30-day delete lock on all data, protecting against accidental deletion, insider threats, and ransomware tactics. 

And we don’t stop there. Our Merkle tree-based architecture ensures that every version of your data is intact, accessible, and verifiable—without relying on legacy full/incremental backup structures. We call it “incremental forever,” and it gives you access to every backup like it’s a full snapshot, while minimizing load and risk. 

Security first, Zero Trust always 

Security isn’t a feature—it’s our architecture. Keepit is secure by design. We’ve embedded Zero Trust principles across our platform, infrastructure, and operations. 

Let’s be clear:  isn’t a checklist. It’s a mindset—and a moving target. You start with identity and context. You assume breach. And you design controls that minimize exposure at every level: user, device, network, application, and data.

From a Keepit perspective, this means role-based access controls, strict SAML-based identity management, secure device access, and IP-based controls at the platform level. It means nobody—not even Keepit employees—can access customer data unless explicitly authorized. 

It also means we can help our customers move closer to their own Zero Trust goals by ensuring the storage layer doesn’t become a blind spot. When storage is also part of your protection posture, Zero Trust has a stronger backbone. 

Full stack control = Full stack visibility 

Most vendors outsource key parts of their operations to hyperscalers. Keepit doesn’t. We own our entire stack. That gives us unmatched visibility into performance, anomalies, and potential risks—across software, hardware, and operations. 

With our , we flag suspicious patterns like spikes or drops in backup volume, mass deletions, or unexpected behavior across monthly snapshots. It’s built-in threat monitoring—not a bolt-on tool—and it’s tuned to detect precisely the kinds of subtle threats that evade traditional alerting systems. 

This is part of our Intelligent Threat Monitoring and Instant Response framework. Because when you own the stack, you don’t just wait for threats to appear—you go find them. 

Built-in risk governance 

We’ve built governance into the core of our product—not layered it on as compliance theater. Our secure and logged access controls offer fine-grained administrative roles, auditable logs, and immutable audit trails accessible through the platform or via integration with your SIEM (e.g., Splunk or Microsoft Sentinel). 

And with no subprocessors and no third-party access to data, we eliminate weak links in the chain. Everything stays in-region, encrypted, and controlled. 

Why cyber storage now? 

The reality is, businesses are under siege. You’re managing more data across more platforms, and the threat landscape is getting more sophisticated by the day. Breaches, insider threats, supply chain compromise—it’s all in play. 

Traditional backup models weren’t designed for this world. They assume trust where there shouldn’t be any. They treat storage as a static, low-risk layer. We know better. At Keepit, we’ve built cyber storage as an active participant in your cyber resilience strategy. Not just something you “have”—but something you use to stay protected, stay operational, and stay in control. 

To wrap up: The storage story has changed 

Cyber attacks don’t discriminate. They don’t wait. And they don’t stop at the edge of your infrastructure. Your backups need to be more than safe—they need to be ready. That’s why cyber storage is the new standard. 

At Keepit, we live and breathe data protection. That’s why we didn’t build on someone else’s cloud. We built our own. Because your data deserves its own home—and your organization deserves a partner that’s all-in on keeping it safe. 

Ready to shift from traditional storage to cyber storage? 

Let’s talk. 

About Keepit
At Keepit, we believe in a digital future where all software is delivered as a service. Keepit’s mission is to protect data in the cloud Keepit is a software company specializing in Cloud-to-Cloud data backup and recovery. Deriving from +20 year experience in building best-in-class data protection and hosting services, Keepit is pioneering the way to secure and protect cloud data at scale.

About Version 2 Limited
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

Helpdesk Ticketing Systems: Criteria, Use Cases, Benefits, and Tips


Effective customer support and service are crucial for companies and their clients. As a key element of customer service, the helpdesk—closely related to but not to be confused with the proactive nature of a service desk—handles incoming requests.

In addition to the skills of the support staff, software support plays a vital role. With the right tools, issues and requests can be easily recorded, categorized, and routed to the appropriate teams.

This article outlines how businesses can choose the most suitable helpdesk ticket system.

The 6 Most Important Criteria for Helpdesk Ticket Systems

Several criteria are important when it comes to helpdesk ticket systems. Companies should define their own focus areas based on their specific needs and expectations.
Here are the six key factors to consider:

#1: User-Friendliness

Intuitive systems are essential—they should offer a smooth experience for both support teams and customers. The system must simplify and streamline services. Complex handling is a serious drawback. A good helpdesk system should support and integrate multiple channels like email, chat, and phone seamlessly.

#2: Workflows and Automation

Effective helpdesk software includes preconfigured workflows that teams can work with efficiently. It’s also valuable when the system can assign tickets to the right team or individual based on predefined rules. Templates for automatic confirmations, responses, and escalation rules can save significant time.

#3: Scalability and Stability

The software should scale as your organization grows. An increase in tickets, users (agents), and data should not be a problem. Even during peak usage, the system should remain stable and responsive.

#4: Security and Compliance

While operational support is the main focus, security is just as critical. Granular role-based access controls protect sensitive data from misuse. The system must also comply with legal regulations such as data retention requirements and the General Data Protection Regulation (GDPR).

#5: Flexible Licensing Options

Helpdesk software typically comes in two models: cloud-hosted (web-based) and on-premises (locally installed). Each model has its own benefits: cloud solutions are low-maintenance and less error-prone, while on-premises solutions offer full control. Ideally, vendors should offer both, giving customers the freedom to choose.

#6: Integration and Customizability

Often overlooked, but crucial: how well does the system fit into your organization’s existing tech stack? APIs are essential for integrating the helpdesk with tools like CRM systems or knowledge bases.

Other important features include ticket categorization (e.g., via Kanban view), reporting and analytics, self-service portals, and AI capabilities such as automatically generated ticket summaries.

Use Cases for Helpdesk Ticket Systems

Helpdesk systems offer daily benefits in many areas—especially in IT Service Management (ITSM), customer support, HR support, project management, and facility management. In fact, helpdesks can add value across nearly all business functions.

They are especially valuable in customer service environments like contact centers and IT support. When managing high volumes of tickets and conversations, helpdesks bring clarity, transparency, and traceability—especially when requests come from various channels (phone, email, social media, messaging apps).

Why Should Companies Use Helpdesk Software?

Helpdesk software allows businesses to work efficiently, stay organized, and provide better service. Customers receive quicker, higher-quality support, and employees benefit from streamlined workflows. Structuring, organizing, documenting, and optimizing communication saves time and resources and boosts customer satisfaction.

Good reason to use Dedicated Helpdesk Software

Here are the most important reasons to use helpdesk software:

  • Efficient communication management
  • Improved cost-efficiency
  • Centralized handling of requests
  • Better-informed support teams
  • SLA tracking and control
  • Transparent and traceable communication
  • Easy access to answers via knowledge bases
  • Simplified cross-team collaboration
  • Process automation
  • Scalable and customizable workflows
  • Role-based access control and security features
  • Continuous improvement through analytics and feedback

Every company can benefit from helpdesk software in its own way. The importance of each factor will vary depending on specific use cases.

Generally speaking: The larger the support operation and the higher the request volume, the more beneficial a software solution becomes.

Key Factors for Evaluation

To properly assess helpdesk systems, companies need to focus on the right criteria. The basic principle: choose a system that brings the most value to your organization. Ideally, users should benefit from intuitive handling and a system that runs without major disruptions.

Critical evaluation criteria include:

  1. Features and Functions:
    • Service portal / interface
    • Knowledge management
    • Search
    • Dashboard
    • User roles and permissions
    • Ticket status, assignment, and prioritization
    • Automation
    • Process management
    • Data encryption
    • Reporting and tracking
  2. User-friendliness
  3. Customer service
  4. Cost-performance ratio
  5. Referral rate
  6. Hosting model (Managed/Cloud vs. On-Premises)
  7. Go-live time (implementation duration)

No one-size-fits-all solution exists. Companies must compare their requirements with what each system offers.

That said, a sound comparison is possible based on standardized criteria. Recommendations can also serve as a valuable starting point to identify which solutions to evaluate more closely.

The Most Important Benefits of Helpdesk Ticketing Systems

There are strong reasons to use helpdesk software. While specific features may vary between providers, several universal benefits stand out:

#1: Centralization

Helpdesk software brings together processes such as multi-channel communication, knowledge management, asset tracking, documentation, reporting, and analytics in one place. For customer service, this means unifying support channels like email, phone, and chat—enabling seamless transitions between channels.

#2: Better Customer Service

Companies use helpdesks primarily to improve communication with customers. The quality of service has a major impact on how a business is perceived. The right helpdesk solution simplifies processes for everyone involved, resulting in faster and smoother service experiences.

#3: Automation

Automation reduces manual effort and frees up time for more important tasks. Many routine tasks in helpdesk operations incur opportunity costs. AI chat, workflow automation, auto-generated tickets, self-service portals, and knowledge bases speed up processes and boost efficiency.

#4: Contextualization

Context is key—especially in helpdesk communication. A good system connects related information, making conversations and documents easy to track and reference. This ensures that users can fully understand the background of each ticket.

#5: Knowledge Management and Documentation

Access to accurate information is either a major asset or a major headache. Strong knowledge management via a well-structured knowledge base, along with solid documentation, is essential for a successful helpdesk system.

#6: Analytics

Analytics provide valuable insights to help improve service management over time. Agents can track ticket status, identify trends, and understand their performance—enabling targeted optimizations.

Tips for Choosing the Right Helpdesk Solution

Here are some key tips to guide your decision-making process:

#1: Prioritize Individual Needs

Different organizations have different goals, industries, team structures, and use cases. Go beyond general criteria and define what your team needs most. Ask yourself: Which system helps us best achieve our goals?

#2: Focus on the Cost-Value Ratio

More features for less money is a common goal. However, balance is key. A low-cost system isn’t always the best value, and a higher-priced solution may deliver more value. Focus on the benefit first, price second.

Don’t just consider upfront costs. Look at the Total Cost of Ownership (TCO)—a metric that reveals long-term differences between providers.

#3: Usability Is More Than a Buzzword

Many vendors claim their system is user-friendly. But true usability means users can leverage the system’s full potential without obstacles. Powerful features are worthless if no one can use them effectively. Often, it’s the simple tools that bring the biggest wins.

#4: Consider the “Concurrent Agents” Licensing Model

“Concurrent agents” refers to the number of agents logged in at the same time. This model is especially cost-efficient for companies with high agent turnover (e.g., call centers). You pay only for the maximum number of simultaneous users, not the total number of agents.

Example: A call center with 100 agents in 4 shifts only needs 25 concurrent licenses.

#5: Prioritize Practical AI and Automation

AI and automation are only valuable if they’re useful in practice. Don’t implement features just for the hype—make sure they solve real problems and improve outcomes.

#6: Don’t Underestimate Go-Live and Support

A fast, smooth implementation is critical. Often, helpdesk software is acquired to address urgent issues. The faster the “go live,” the sooner teams can benefit. Post-implementation support also plays a vital role in ongoing success.

#7: Don’t Compromise on Security and Compliance

Security threats and data breaches are very real risks. Helpdesk systems must offer robust security features (like encryption) and help users comply with regulations such as GDPR.

Conclusion: Helpdesk Software Offers Versatile Benefits

Helpdesk ticket systems offer value in many ways and across many functions. When aligned with a team’s or organization’s needs, they provide substantial benefits for both staff and customers.

Not all factors will matter equally in every case, but decision-makers should prioritize the most relevant criteria and advantages. Key blind spots—such as implementation time, user-specific usability, and total cost of ownership—deserve special attention.

About OTRS

OTRS (originally Open-Source Ticket Request System) is a service management suite. The suite contains an agent portal, admin dashboard and customer portal. In the agent portal, teams process tickets and requests from customers (internal or external). There are various ways in which this information, as well as customer and related data can be viewed. As the name implies, the admin dashboard allows system administrators to manage the system: Options are many, but include roles and groups, process automation, channel integration, and CMDB/database options. The third component, the customer portal, is much like a customizable webpage where information can be shared with customers and requests can be tracked on the customer side.

About Version 2 Limited
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

Enhance Security with SAML: Pandora FMS Now Supports Azure Entra ID

In modern enterprise environments, access management is key to ensuring security and regulatory compliance (ENS, ISO 27001, NIS2, etc.). That’s why Pandora FMS has added support for Azure Entra ID, enabling authentication through SAML (Security Assertion Markup Language). With this integration, we provide simplified and secure access to our platform using Single Sign-On (SSO).

What is SAML and Why Is It Important?

SAML is an open XML-based standard that enables the exchange of authentication and authorization data between an Identity Provider (IdP) and a Service Provider (SP). This means users can authenticate once and gain access to multiple applications without needing to log in repeatedly.
Implementing SSO with SAML in Pandora FMS provides several key benefits:

  • Enhanced security: Reduces reliance on weak or reused passwords, lowering the risk of compromised credentials.
  • Improved user experience: Enables seamless access across different platforms, simplifying the login process for employees, partners, and customers.
  • Regulatory compliance: Supports the adoption of Zero Trust policies and centralized access management.

Integration with Azure Entra ID

Compatibility with Azure Entra ID allows Pandora FMS to integrate with Microsoft’s identity solution, providing centralized control over user authentication. This enables:

  • Centralized authentication for all users in enterprise environments.
  • Automated access management based on roles and permissions defined in Entra ID.
  • Reduced security risks through multi-factor authentication and advanced access policies.

Implementing this functionality allows organizations to align their infrastructure with modern security principles, reduce the attack surface, and ensure controlled access to critical systems.

Configuration in Pandora FMS

To configure SAML with Azure Entra ID in Pandora FMS, communication between both platforms must be established by defining the identity provider and the service provider. This involves creating and configuring an application in Entra ID, assigning the appropriate permissions, and integrating it with the SAML settings in Pandora FMS.
The detailed configuration procedure, including specific steps and advanced options, is available in the Pandora FMS technical documentation, where each required parameter for implementation is thoroughly explained.
With this new feature, we strengthen identity management security and efficiency within Pandora FMS. Compatibility with Azure Entra ID is another step in our commitment to enterprise security, helping organizations optimize authentication and improve access control.

The integration of Pandora FMS with Azure Entra ID not only enhances security but also complements the monitoring capabilities for Microsoft Azure infrastructures. Credential and access management, combined with advanced monitoring, allows businesses to optimize operations and effectively reduce risk.


About Version 2 Limited
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

About PandoraFMS
Pandora FMS is a flexible monitoring system, capable of monitoring devices, infrastructures, applications, services and business processes.
Of course, one of the things that Pandora FMS can control is the hard disks of your computers.

ESET Annual Report 2024: Profit and revenue growth continues, R&D investment delivers strong returns

  • Global revenue growth of 9 per cent year-on-year to €691 million, with the EMEA region leading with 15 per cent
  • Adjusted EBITDA of €100 million, reflecting 7 per cent year-over-year growth
  • Total B2B revenue growth of 13 per cent, Enterprise of 21 per cent, and Services of 56 per cent

BRATISLAVA — June 30, 2025 — ESET, a global leader in cybersecurity solutions, today announced its financial results, with significant growth in key regions and markets, continuing profitability, and ongoing investment in science-led innovation.

“While many speak of long-term vision and longevity, few live it. 2024 saw ESET’s third consecutive decade of growth — a rare milestone in the technology sector, and one that reflects our progressive mindset, customer trust, and product excellence,” said Richard Marko, CEO of ESET. “We saw particularly strong momentum in the EMEA region, where our cybersecurity solutions continue to gain traction. This was further reflected by strong performance within our B2B segment, where overall revenue grew by 13 per cent, Enterprise grew by 21 per cent and ESET Services experienced exceptional growth of 56 per cent. As threats evolve, so does our commitment to meeting our customers’ need for innovation and resilience.”

R&D delivers immediate AI benefits for threat detection and response

In 2024, ESET’s 847-member-strong technologists and Global Research and Development team worked to revamp ESET LiveGuard Advanced (ELGA), our proprietary cloud-based security module that uses behavioral analysis to prevent targeted attacks and new or unknown threats. This essential work also leveraged our latest developments in Artificial Intelligence (AI), advancing both scanning and filtering and further reducing ELGA’s computing requirements in comparative tests.

Further development of ESET AI capabilities in 2024 saw us introduce ESET AI Advisor, which allows  detection and response teams to leverage multi-agentic AI in incident response and risk analysis. This empowers organizations to fully capitalize on extended detection and response (XDR), taking care of threats before they have a chance to become full-scale security incidents. ESET AI Advisor has also been built into ESET Inspect, the company’s XDR-enabling module of the ESET PROTECT Platform, which proved its worth during MITRE’s 2024 Enterprise ATT&CK® Evaluations.

“Our long-term investment in research and development continues to benefit an increasing number of customers and make a profound impact,” said Richard Marko. “Threat actors are making increased use of artificial intelligence and automated tooling; in turn, ESET’s attention to, and investment in, AI have not only helped us counter those malicious forces, but have boosted revenue growth in 2024, in particular within the B2B segment.”

Threat research and threat intelligence, usability, and defense enhanced for business customers and service partners

ESET Research remains at the core of our efforts, informing not only the prevention-enhancing capabilities and R&D of our products (such as ESET Threat Intelligence), but also providing a better understanding of the threat landscape and empowering business and consumer security, globally.

ESET Research Highlights:

Among our many successes are the research pieces pursued by our award-winning Malware and Threat Research team. Of note are:

  • The discovery of Operation Texonto, a Russian-aligned disinformation and PSYOPs operation targeting Ukrainian readers — including a Ukrainian defense provider and an EU agency
  • Identification of NGate malware that enables attackers to clone near-field communication data from victims’ physical payment cards to target banking customers
  • Examination of the actions of the Russian-aligned Gamaredon APT group and GoldenJackal cyber espionage group that are operating in Ukraine and conducting attacks across Europe
  • Research publication on RedLine Stealer’s backend modules as part of the joint investigation into the MaaS group’s activities with Dutch police, the FBI, and Eurojust in late 2024.

“In 2024, ESET deepened relationships with several significant government customers and added new partnerships, particularly in the field of cyber threat intelligence. The dividends show as we continue to work closely with law enforcement partners, including Europol, ENISA, and CISA, to help defend businesses, individuals, and societies,” said Roman Kovac, Chief Research Officer at ESET.

A great dividend of research on our ongoing product development efforts in 2024 was the introduction of two managed detection and response (MDR) services — one for SMBs and one for enterprises — while also securing several strategic partnerships. This investment contributed to double-digit revenue growth in the SMB and MSP spaces, as well as in the Enterprise segment.  This growth was also reflected by our sharpened strategies addressing the complex cybersecurity needs of large enterprises, critical infrastructure, and government institutions. This, too, can be seen in ESET Corporate Solutions’ accelerated delivery of tailored solutions for high-stakes environments.

Among the developed or expanded partnerships in 2024 were:

Progress. Protected.

In 2024, ESET continued to redefine what is possible in cybersecurity through cutting-edge research and development. At the heart of this innovation is our deep commitment to AI and machine learning — powering smarter, faster, and more adaptive threat detection systems. Through continuous collaboration with academia and relentless in-house innovation, ESET ensures that our AI-powered solutions not only meet today’s cybersecurity demands, but anticipate tomorrow’s.

Moving forward, ESET’s commitment to a cloud-first strategy, robust managed detection and response (MDR) capabilities, and AI-native prevention-first technologies remains central to its vision — ensuring resilience, adaptability, and leadership in an increasingly sophisticated threat landscape.

For further information about ESET’s successes in 2024, please read the full 2024 ESET Annual Report here.

About ESET
For 30 years, ESET® has been developing industry-leading IT security software and services for businesses and consumers worldwide. With solutions ranging from endpoint security to encryption and two-factor authentication, ESET’s high-performing, easy-to-use products give individuals and businesses the peace of mind to enjoy the full potential of their technology. ESET unobtrusively protects and monitors 24/7, updating defenses in real time to keep users safe and businesses running without interruption. Evolving threats require an evolving IT security company. Backed by R&D facilities worldwide, ESET became the first IT security company to earn 100 Virus Bulletin VB100 awards, identifying every single “in-the-wild” malware without interruption since 2003.

About Version 2 Limited
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

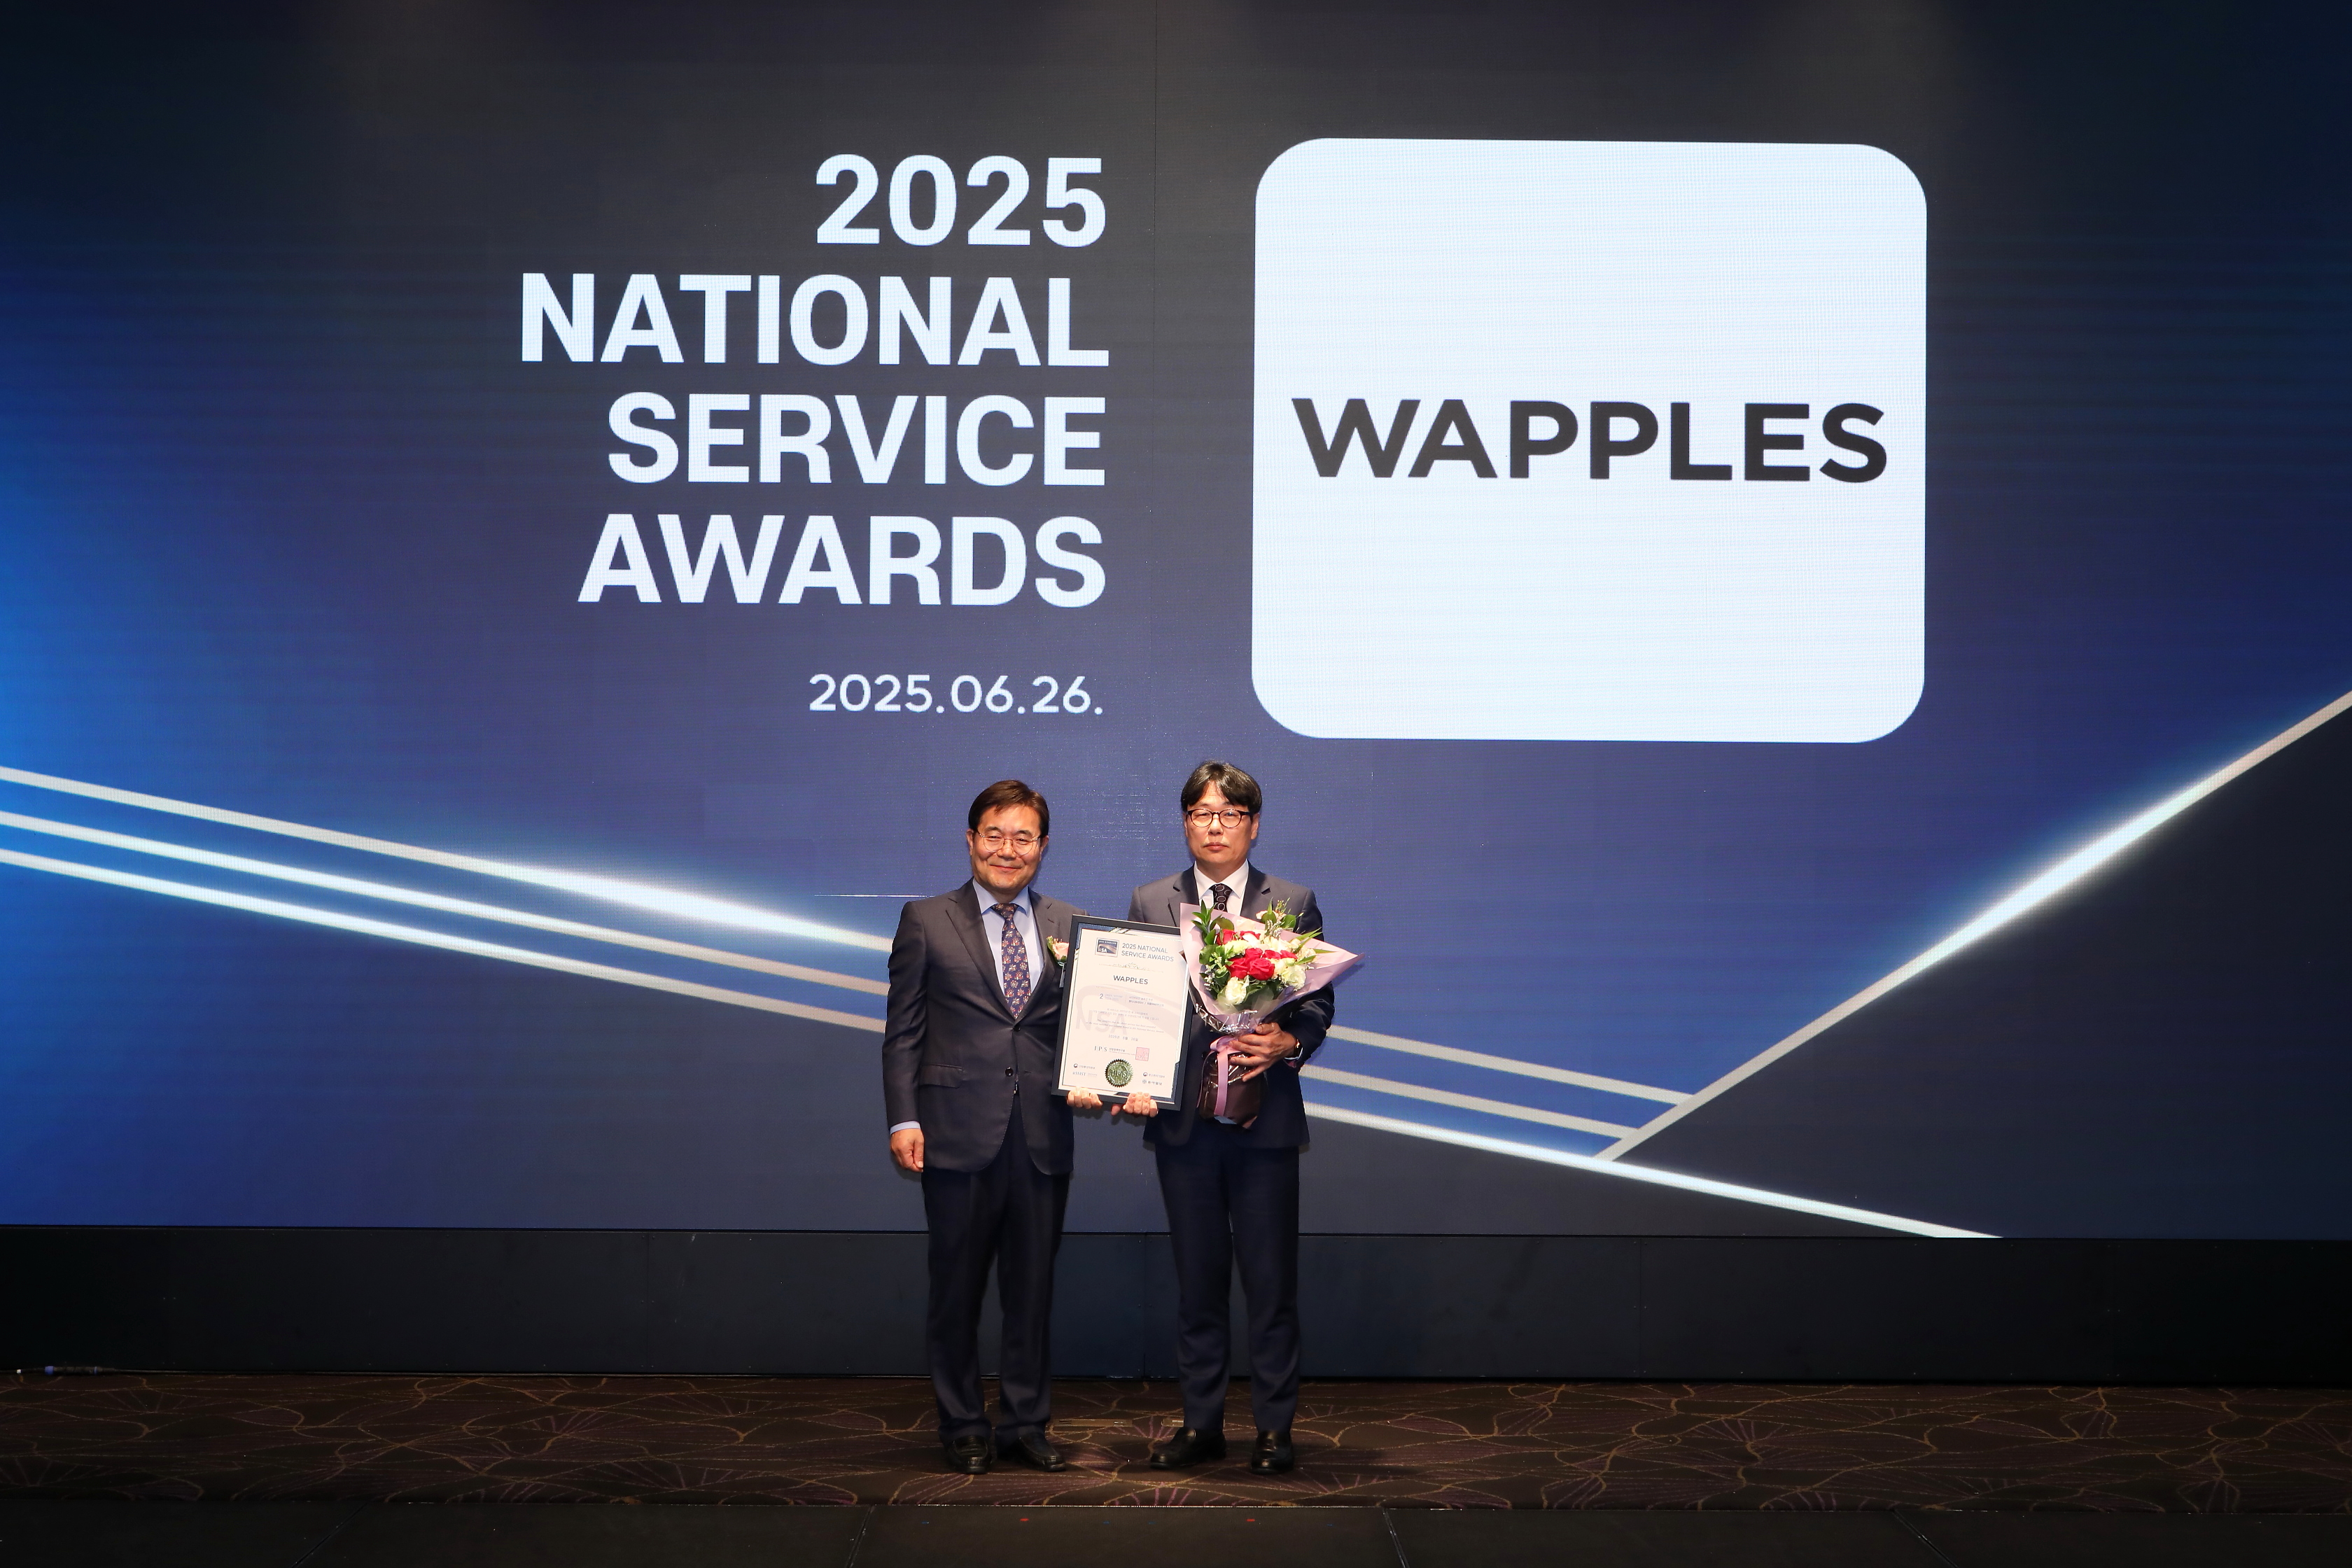
WAPPLES Wins 2025 National Service Awards for the Second Consecutive Year

WAPPLES Wins 2025 National Service Award

Penta Security’s WAPPLES Marks 20th Anniversary with Second Consecutive National Service Award Win

Intelligent WAAP solution honored for superior customer satisfaction and market leadership, reaffirming its status as the sole winner in the award’s cybersecurity category.

Penta Security’s intelligent WAAP (Web Application and API Protection) solution, WAPPLES, has once again been honored at the 2025 National Service Awards, winning the Cybersecurity Solution category for the second consecutive year. This recognition coincides with the 20th anniversary of WAPPLES, marking two decades of market leadership and innovation in web security.

The National Service Awards recognize organizations that have earned exceptional consumer support, evaluating them on criteria such as customer satisfaction, competitive advantage, and service management. The cybersecurity category was established in 2024, with WAPPLES being its inaugural and, to date, only winner.

Since its launch in 2005, WAPPLES has maintained its position as the #1 web security solution in the Korean market for 17 straight years, renowned for its high detection accuracy and low false positive rate. Today, it is a top-tier global WAAP solution deployed in 171 countries and serves as the core engine for the Cloudbric SECaaS platform, which protects over 700,000 internet businesses worldwide.

“Winning this award as we celebrate the 20th anniversary of WAPPLES is incredibly meaningful,” said a spokesperson for Penta Security. “It validates two decades of customer trust and our commitment to innovation. We will continue to build on this legacy to deliver the highest level of satisfaction and security.”

About Penta Security
Penta Security takes a holistic approach to cover all the bases for information security. The company has worked and is constantly working to ensure the safety of its customers behind the scenes through the wide range of IT-security offerings. As a result, with its headquarters in Korea, the company has expanded globally as a market share leader in the Asia-Pacific region.

As one of the first to make headway into information security in Korea, Penta Security has developed a wide range of fundamental technologies. Linking science, engineering, and management together to expand our technological capacity, we then make our critical decisions from a technological standpoint.

About Version 2 Limited
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

Project Dependency Mapping: A Strategic Pillar for IT Success

Project Dependency Mapping is the process through which interdependency relationships between different projects, tasks, teams, and resources are identified, documented, and managed. This, to put it in rather technical and cold terms. 

Let’s say it in simple words: it’s the tracking activity that allows you to know which part of the work depends on another, what blocks could arise, and how to intervene in advance. 

In short, it’s a fundamental discipline for every modern IT organization that wants to ensure effective planning, reduce delay risks, and optimize the use of available resources. To put it another way: for any company that doesn’t want to be left behind. 

In the current IT ecosystem, where software implementations, infrastructure rollouts, update management, and cybersecurity continuously intersect, this process becomes an indispensable lever for: 

  • Ensuring correct and optimized resource allocation. 
  • Avoiding delivery delays. 
  • Preventing operational bottlenecks. 
  • Fostering collaboration between teams, eliminating organizational silos. 
  • Planning all processes with precision and flexibility. 
  • Reacting agilely to changes and priority shifts. 

We will return extensively to all of this in the rest of the article, but we want to emphasize a central point from the outset: it’s not just about coordinating technical tasks, but about building an integrated vision that relates times, responsibilities, tools, and strategic objectives. A more general paradigm shift. A decisive step toward full digital maturity. 

Project Dependency Mapping, in fact, allows for solid governance, greater predictive capacity, and operational flexibility that can make the difference, especially in dynamic and interconnected environments… which are exactly the environments where today’s main market challenges are played out. 

Project Dependency Mapping – Why It’s Crucial in IT Strategy 

In the lifecycle of an IT project, every phase can be impacted by other ongoing initiatives: so far, all quite intuitive. Yet, dependencies are not always visible to the naked eye. Some of these are evident; a few examples? A software release that depends on the completion of a testing phase, the start of a deployment activity that requires the completion of infrastructure configuration, or the integration of an ERP module subordinated to the delivery of an API package from another team. But there are also several dependencies that, instead, can be much less visible: a security policy that delays a cloud migration, a system update that gets postponed because the network team is working on another priority project, or an approval request tied to an IT budget blocked by an internal decision-making process still in progress… just to cite only a few common cases. 

In such a context, therefore, mapping dependencies means primarily making all this visible, so it can be kept under control. But not only that. 

The most important point, actually, is another and goes beyond: moving from reactive to proactive management of IT processes. And this is where Project Dependency Mapping directly connects to an effective IT Governance concept. Think about it: in the end, it’s precisely the tool that allows transforming digital complexity into a competitive advantage. 

Get the latest ITSM insights! Explore AI, automation, workflows, and more—plus expert vendor analysis to meet your business goals. Download the report now!

The Main Types of Dependencies to Monitor 

Let’s say it clearly: it’s impossible to provide an exhaustive list of all the types of dependencies to keep under control with Project Dependency Mapping systems. Much depends on the individual company and the context within which it operates. However, it’s certainly possible to identify the main types, valid for all types of business. We list them below: 

  • Temporal dependencies. Simply put, one activity cannot start until another is completed. 
  • Logical dependencies: that is, based on causal relationships. Let’s see some examples: a hardware configuration necessary to test software; the preparation of development environments before being able to start debugging an application; or the need to complete the requirements gathering phase before defining the system architecture. 
  • Resource dependencies. A very common situation, where multiple projects share the same team and/or the same infrastructure. 
  • Organizational dependencies. A point that may or may not be connected to the previous one. Here we mainly talk about dependencies related to decisions, approvals, or budgets managed by other departments. 
  • Technical dependencies: that is, linked to compatibility between systems or the need to integrate new technologies. Also in this case, here are some practical examples: legacy software that needs middleware (therefore a “bridge”) to communicate with a new cloud platform; a third-party library that must be updated before proceeding with application deployment; or, again, the need to synchronize integration between ERP and CRM systems to ensure correct data flow. 

Technological Vanguard in Project Dependency Mapping 

Let’s start again from an awareness, which is a rather obvious consequence of what we have examined so far: mapping dependencies manually is practically impossible in complex business realities. Dedicated and tailored tools are needed. Above all, efficient integration with the most advanced ITSM software or Project Portfolio Management (PPM) platforms is needed. 

And here we come to practice: solutions like EV Service Manager allow integrating project data with those related to – for example – ticketing, incident management, asset management, and service requests, facilitating dependency identification and automation of alerts and priorities. 

Not only that. Even more crucial becomes integration with monitoring solutions like EV Observe, which allow automatically detecting changes in infrastructure and IT flows, anticipating potential conflicts between projects and systems. 

In short, we can imagine the infrastructure itself as a complex network of dependencies (and interdependencies). An holistic but also detailed vision is needed. Automation is needed (a crucial theme we return to in the next paragraph), but also an “orchestra direction” that allows teams to make increasingly informed strategic decisions. 

The Decisive Added Value of Automation and AI 

The introduction of Artificial Intelligence and automation allows a further step forward in Project Dependency Mapping. To put it very synthetically: with this turning point, systems not only track dependencies but learn from them. 

Thanks to Machine Learning, in fact, it’s possible not only to automatically register new interdependencies based on collected data, but also to optimize project decisions with increasingly sophisticated predictive capabilities. 

Is this something that concerns the future? No; it’s the present. And it already has many practical implications, including: 

  • Analyzing recurring patterns of failure or delay. 
  • Proactively suggesting new priorities. 
  • Simulating alternative planning scenarios with relative pros and cons. 
  • Improving workload forecasting. 
  • Recognizing weak signals in operational flows to activate corrective actions before a problem becomes critical. 
  • Integrating Project Dependency Mapping with real-time monitoring dashboards for instant visibility on the impact of every variation. 
  • Offering strategic insights to stakeholders, through automatic reports on constraints, bottlenecks, and optimization opportunities. 

The list could go on much longer (but would deserve more in-depth and separate treatment). 

Before moving on to best practices for implementing Project Dependency Mapping, we want to emphasize another decisive aspect, which has to do with continuous improvement. Artificial intelligence, in fact, favors standardization of analyses, reducing subjectivity in priority evaluation and facilitating faster alignment between teams. How? By learning from previous versions of similar projects, capitalizing on experience to improve future performance. A bit like we humans have always done… but with infinitely greater computing power. 

Best Practices for Implementing Effective Project Dependency Mapping 

As we always like to emphasize in our blog, best practices should not be confused with a universally valid recipe. Much depends on the characteristics of one’s organization, the context in which it is immersed, the bases from which one starts, legacy systems, and the specific objectives one sets. 

Having made this necessary premise, however, pillars valid for all types of realities can be identified when it comes to implementing effective and continuously evolving Project Dependency Mapping. We list them below: 

  • Define a coherent framework. Use recognized standards like those of ITIL to structure workflows and dependencies between services. 
  • Involve all stakeholders. Every team must be aware of its own dependencies and how its work impacts (and depends on) that of others. 
  • Use dynamic dashboards. Interactive and real-time visualizations allow understanding connections between tasks, projects, and departments intuitively. 
  • Plan periodic reviews. Dependencies change. The mapping must be constantly updated to reflect the continuously evolving reality. 

Conclusion 

In an increasingly distributed, complex IT context driven by continuous change, ignoring interdependencies between projects is an unforgivable error. Project Dependency Mapping is not just a set of technical tools: it’s a strategic discipline. And those who master it are able to transform complexity into value. 

Get the latest ITSM insights! Explore AI, automation, workflows, and more—plus expert vendor analysis to meet your business goals. Download the report now!

About EasyVista  
EasyVista is a leading IT software provider delivering comprehensive IT solutions, including service management, remote support, IT monitoring, and self-healing technologies. We empower companies to embrace a customer-focused, proactive, and predictive approach to IT service, support, and operations. EasyVista is dedicated to understanding and exceeding customer expectations, ensuring seamless and superior IT experiences. Today, EasyVista supports over 3,000 companies worldwide in accelerating digital transformation, enhancing employee productivity, reducing operating costs, and boosting satisfaction for both employees and customers across various industries, including financial services, healthcare, education, and manufacturing.

About Version 2 Limited
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.