





Why GREYCORTEX Mendel Is the Essential Member of Your Network Security Product Family
There are several basic tools for securing network infrastructure that should not be missing from any organization. Let’s take a look at the role of GREYCORTEX Mendel in all those products protecting the data and network in your company.
Antivirus software, firewalls and intrusion prevention systems (IPS) should be an integral part of any organization’s cybersecurity solution. Nowadays, however, they are often not enough. That’s where Mendel steps in.
GREYCORTEX Mendel stands on several levels:
- It is a unique tool that sees, visualizes and analyzes everything in your network – devices, access and all communications.
- It is a great extension to the functionality of standard cybersecurity tools: antivirus, firewalls and network performance monitoring. They are crucial, but there are some threats that even they cannot detect. The reason is simple: attackers are often ready for these standard systems.
Mendel Sees and Visualizes in the Context of Time and Events
Imagine a tool that sees all the devices in your network, how they are communicating together, what protocols they are using and where your data is going. With Mendel, you can see all of that. You can also view the details of a specific device, its communication and where it is connected to at the moment, and also yesterday or a year ago.

With this unique analysis, you can uncover a sophisticated attack on your infrastructure before it really happens. That’s because you can relate current events to events that happened before, even in the more distant past.

Let’s take a look at an example of an attack that may go unnoticed by a standard detection mechanism: Advanced malware is not detected on the end device, but that device shows behavior that could endanger the network – for example, trying to access somewhere it has not accessed before. It could be spyware or an APT in your internal domains that is gradually spreading across your network through a domain, while the infected machines start accessing unusual devices and data sources and performing lateral movement. Mendel can identify and notify you of such unusual behavior.
More Reliable End-Point Security
Because end-points are an easy target, often provide valuable data and are an entry point for gaining deeper access to your network, they are the frequent initial targets of cyber-attacks.
Commonly known end-point attacks include:
- network mapping
- data exfiltration (sending data in non-standard or encrypted channels, communication with control devices)
- Dictionary attacks, password data breaches
- Data mining (reading important information, mining data from a database, mining users from information systems or from a domain controller)
Mendel flags such attacks as dangerous behavior and recognizes the threat that might not have been recognized by endpoint security or that is well hidden by the attacker. Even if antivirus software is deployed, Mendel monitors the communication of your devices and reveals any anomalies in it. All of that using a broad database specializing in network cyber threats that include not only known threats but also signatures of unusual behavior.
A Smarter Firewall
We can understand a few things that fall under the term firewall: standard firewalls and smart solutions known as an IPS.
Traditional firewalls stand first in the line of defense and secure broad traffic filtering. They adjust network transitions and the availability of network services and are mostly used on the external perimeter – in some cases within the internal network. They are often open or insufficiently configured.
In such cases, Mendel plays the role of an auditing tool – controlling the function of the firewall itself and checking its configuration. You can use this feature for verifying and controlling the communication matrix in your internal network and critical systems. It helps you understand who is connecting where, who is using what and who is behaving differently than they should.
Smart solutions such as IPS see more deeply into your network, can detect known threats and block them. Also here, Mendel provides you a double-check by monitoring the operation of web proxies and email gateways. This means no potential threat can pass. Even in this case, Mendel’s advantage is its extensive database of threats, consisting of multiple sources and signatures that verify not only known attacks but also security policies and potentially dangerous access to data sources, such as administrative sharing. This approach is much more effective for the detection of vulnerabilities than just a database of known threats from one vendor.
This way, Mendel shows much more – not only what needs to be blocked but also unwanted or insecure applications and access to risky services. You’ll get a much better overview of what is going on and what is going through your network and how.
The Danger of Unknown Threats
In all mentioned cases, Mendel not only deals better with detecting known threats, its strength lies in also detecting unknown threats. How? Mendel recognizes different types of actions using behavioral analysis.
Right after anomalous behavior or an unknown threat is detected, the system notifies you, for example, by email. It’s then your choice. You can either take the necessary steps or you can connect Mendel to the firewall API and it will block the unwanted communication automatically for you.
A Huge Help for Monitoring Network Performance
At the next level, there are tools for internal system monitoring. In this case, Mendel shows a clear overview of the network – how it is loaded and used, who is accessing it, what services are operating and what the performance of applications and transmission lines is.
Imagine seeing just how loaded your information system, domain controller, Wi-Fi network or data center are!

GREYCORTEX Mendel helps you increase the reliability of your network. Even industrial control systems can get the right amount of control, so any attack or even a major network failure has no catastrophic consequences.
Antivirus software shows you current threats. A firewall displays the current settings and whether it is leaking something or not. But nothing will clearly show you events in your network an hour, a week or a year ago. In a nutshell, Mendel sees, visualizes and (thanks to data storage of up to the last several years) also analyzes current as well as past events.

What is the Zero Trust security model, and why is its adoption growing?
Zero Trust promotes the concept that organizations should not trust any entity inside or outside their network perimeters in a predetermined fashion.
Adoption of the Zero Trust security model is picking up steam at last. In February 2020 – before the pandemic swept the world – a survey of more than 400 IT security decision makers conducted by Cybersecurity Insiders and Pulse Secure revealed that 72% of organizations were planning to either assess or implement Zero Trust in their security strategy during the course of the year. Then, in May 2021, President Biden’s Executive Order on Improving the Nation’s Cybersecurity threw down the gauntlet by acknowledging the broken state of the US’s federal model of cybersecurity and the need to implement a Zero Trust Architecture.
In this article, we briefly explain Zero Trust, what is needed to implement it, and why interest in it is growing.
What is Zero Trust?
According to Forrester, which created this concept back in 2010, in contrast to the traditional, perimeter-based security model that builds on the premise of “trust but verify,” Zero Trust says organizations should never trust any entity, whether internal or external. In other words, “never trust, always verify.” The Zero Trust model builds security around each of the key resources and entities of an organization: data, networks, devices, workloads, and people.

Figure 1 – The Zero Trust model builds security around each of the key resources of an organization.
In the traditional IT security model, the security posture of an organization should be like a castle guarded by a moat, which represents the network. In such a setup, it is difficult to gain access to an organization’s resources from outside the network. At the same time, everyone who is inside the network is considered trusted by default. The problem with this approach, however, is that once an attacker gains access to the network, and thereby becomes trusted by default, all the organization’s resources are ripe for the picking.
In contrast, the Zero Trust model assumes that attackers are inside the network just as much as outside. For this reason, trust cannot be given indiscriminately to users and devices by default.
 Figure 2 – Animated graphic that exemplifies the traditional perimeter-based security model

Figure 3 – Animated graphic that exemplifies the Zero Trust security model
What does an organization need to do to implement the Zero Trust model?
There are three core areas of capability that an organization should develop as it implements the Zero Trust model:
- Visibility: Identify devices and resources that should be monitored and protected. It is not possible to protect a resource that you do not know about. Having visibility into all your resources and access points is indispensable.
- Policies: Establish controls that only permit specific people to have access to specific resources under specific conditions. In other words, a granular level of policy controls is required.
- Automation: Automate processes to ensure the correct application of policies and enable the organization to rapidly adapt to any deviations from standard procedures.
Building on the foundational capabilities outlined here, we can define Zero Trust as a security model that builds defenses around each of the following entities: data, networks, devices, workloads, and people.
What is driving the renewed interest in and adoption of the Zero Trust model?
With a Zero Trust environment, not only do you have control and knowledge of all your data (all the time), but in the event of a security breach, you can quickly detect when and where attackers may have pilfered your data, as Forrester explains. Considering that the 2020 Cost of a Data Breach Report by IBM and the Ponemon Institute revealed the average cost of a data breach globally to be US$3.86 million and the average time to identify and contain a breach 280 days, the Zero Trust model appears rather attractive.
On the other hand, with the continued growth of the bring your own device (BYOD) and remote work phenomena, more and more employees need to have access to their organization’s internal resources from any place at any time. It is worth highlighting that the pandemic saw a gigantic increase in brute-force attack attempts against the remote desktop protocol (RDP), demonstrating the high interest of cybercriminals in taking advantage of the current remote work situation.
Another component driving Zero Trust is the growing adoption and use of storage services in the cloud. The cloud often hosts the data, resources, and even the critical services of organizations.
Other vectors that have proven fatal for the perimeter-based security model are supply-chain attacks – as was the case with NoxPlayer, an Android emulator used by gamers to play mobile games on their PCs and Macs – outsourcing of services, and employee turnover, among others.
How to Pick an Endpoint Security Solution in a cluttered market
In today’s crowded market, picking an endpoint security solution that fits your business needs is not an easy task. Competition is good to spur innovation, but how can IT managers decide when there are so many vendors out there that claim to offer the best solutions?
To distinguish a good security solution from the bad, you should assess these three critical areas: real-world performance, the vendor’s vision, and end-user reviews. Thankfully, you don’t have to start from scratch as there are various independent market research reports available that can help you to make up your mind.
Let us show you why ESET checks all the right boxes and scores extremely well in all three areas.
Real-world performance
Independent testing labs undertake tests to assess the real-world performance and usability of various security solutions in the market. They often use large samples of in-the-wild threats for testing to provide accurate performance indicators. As these reports are data-driven, it allows you to take out the guesswork and make an informed decision to ensure you pick the right security solution for your business.
Here’s what the leading independent testing labs have to say about ESET security solutions.
AV-TEST
AV-Test is an independent evaluator with over 15 years of testing security solutions under its belt. In their March – April 2021 report, AV-Test assessed the capabilities of 18 business endpoint security solutions on several critical considerations, namely protection against malware infections, the impact of security software on computer speed and usability. ESET received a perfect total score of 18/18 for all three categories and had been doing so in the past three assessments conducted by AV-Test.
 Figure 1: ESET received the perfect score for the third time running
In the Protection Test, over 17,000 malware samples consisted of zero-day attacks, web threats and prevalent malware were used to evaluate the effectiveness of security software in a real-world setting. ESET recorded an impressive 100% protection against such threats in the tests conducted in March and April 2021.
This was achieved without compromising the computer’s performance as indicated by a six out of six rating in the Performance Test, which assessed the system load on various tasks such as slower copying of files and slower launch of standard software.
As false alarms can disrupt work routine, AV-Test also measured the number of false positives flagged or blocked when visiting websites and using legitimate software. ESET recorded zero false positives in more than the 1.7 million samples tested.
IT managers should keep in mind that a security solution can be fast but inaccurate with high false positives and a low detection rate. It can also be accurate but consume too many resources for scanning, which slows down PCs. ESET emerged as the top solution because it is both fast and accurate.
AV-Test’s assessment showed that ESET’s endpoint protection solution is suitable for all types of PCs, including low and mid-performance ones. It strikes the perfect balance between accuracy, speed, and resource consumption for optimal performance. As a business owner, you could even potentially stretch your PCs’ lifespan.
MRG Effitas
MGR Effitas’ 360 Degree Assessment & Certification is another test report that is useful to measure the efficacy of an endpoint security solution. In Q3 2020, MGR Effitas tested eight endpoint security solutions, and only five fulfilled its strict standards of excellence.
Do security solutions autoblock malware, or do they also require user’s intervention? Unlike other tests, MRG Effitas also evaluates a solution’s autoblock and behaviour block (postpone the execution of a file that is suspected malicious while awaiting user input). Solutions that missed malware were also given a second opportunity after 24 hours in a second scan.
If you want a solution that autoblocks, ESET is the right choice for you. ESET scored the highest with respect to autoblock with 98.51% vs. the reported average of 93.78% for the ‘In the Wild 360 / Full Spectrum test’. When combined with malware blocks that required user intervention, ESET scored 100%. It was one of only two vendors with a 100% detection rate on the first scan.
Thanks to our high auto-block rate, ESET had the lowest behaviour block of almost a third vs. the other vendors. This means end-user can expect minimal pop-up disruption as most of the threats had been blocked automatically without the user’s input.
 Figure 2: ESET scored the highest autoblock for the In the Wild 360 test
ESET’s solution was the only security solution that obtained a 100% block rate (automatic and behaviour block) for all of the samples tested in every threat category, namely in the wild, ransomware, financial malware, and PUA/adware. ESET auto-block capability was unmatched as our solution scored 100% auto-block in 3 out of 5 categories. No other vendors came close.
What’s even more impressive was ESET’s solution achieved this with a small memory footprint at merely 190.1Mb vs. 402.6Mb for the second vendor and 300Mb lower than the average. These tests were conducted based on the ‘enterprise’ environment, highlighting that ESET’s solutions are not designed only for SMBs.
SE Labs
SE Labs tests enterprise-grade endpoint security solution capabilities such as ESET Endpoint Security by using a “full attack chain” to evaluate the effectiveness of every layer of detection and protection. In their 21Q1 Enterprise Endpoint Protection report, ESET scored 100% in legitimate accuracy (no mistakes in distinguishing legitimate websites and applications), 99% in total accuracy, and 97% in protection accuracy. As SE Labs put it, “ESET achieved extremely good results due to a combination of their ability to block malicious URLs, handle exploits and correctly classify legitimate applications and websites.
Market Research from Leading Firms
While the aforementioned tests are a good indication of ‘current’ performance, the cybersecurity threat landscape isn’t static. New threats emerge all the time. When choosing an endpoint security solution, IT Managers should ask: Can the vendor enable my business to stay ahead of evolving threats?
The right vendor for your business should continuously develop and invest in their products to ensure your business is always protected from current and future threats. Market research from leading firms can answer these questions and many more.
AV-Comparatives Endpoint Prevention and Response (EPR) 2020
Thanks to the capabilities of the ESET Protect Enterprise bundle, ESET was named a Strategic Leader in the AV-Comparatives’ Enterprise EPR CyberRisk Quadrant. ESET is at the top right of the quadrant!
 Figure 3: ESET’s position in the AV-Comparatives’ Enterprise EPR CyberRisk Quadrant
ESET also scored the highest in Response Capability. Strategic Leaders like ESET were recognised for having a high return on investment and providing a low total cost of ownership (TCO). Why does TCO matter? An organisation doesn’t only pay for the solution but also breach costs and operational accuracy costs. This means a vendor that offers the lowest upfront per agent cost might not necessarily be the cheapest as a business will incur losses or operational costs during a breach or false positive investigation.
According to AV-Comparative, ESET had the lowest 5-year TCO – almost 60% lower than the average of all the vendors evaluated!

Figure 4: Total Cost of Ownership Formula

Figure 5: Key Metrics based on 5,000 clients
Radicati
ESET was recognised as a Top Player in Radicati’s 2020 Endpoint Security Market Quadrant, which evaluates 17 leading vendors in this niche. It was placed in this quadrant for the third year in a row. ESET was also named a Top Player for the second year in a row in Radicati’s 2021 Advanced Persistent Threat (APT) Protection Market Quadrant. This report examines 12 leading security vendors in the market. ESET was one of six vendors to be recognised as a Top Player.

Figure 6: ESET, a Top Player in the Radicati Magic Quadrant
IDC
International Data Corporation is a market research and analysis organisation that evaluates devices, networks, applications, and services across various industries. The IDC MarketScape: Worldwide Mobile Threat Management Software 2020 Vendor Assessment recognised ESET as a global leader in cybersecurity for the second year in a row.
This IDC evaluation states that “ESET is strong in the areas of threat research, especially around Android malware identification and behaviour detection. Organisations looking to consolidate security products and operations around a unified endpoint security model should also consider ESET for its broader portfolio of endpoint and security management tools on top of Mobile Threat Management.”
Forrester
Forrester Research is a market research and advisory company that helps consumers identify high-performance businesses. ESET was included in Forrester’s Now Tech: Enterprise Detection and Response (EDR) Q1 2020 report and was recognised as an Enterprise Architecture EDR solution provider.
End-User Insights
It’s not a secret that we usually check out peer reviews when purchasing a big-ticket item. It is human nature to seek feedback that validates our choices. This principle also applies to our purchase decisions. Luckily, there are so many review sites that specialise in verified end-user reviews.
Gartner Peer Insights and Voice of the Customer
Gartner is a global research and advisory firm that supports different business industries. Voice of the Customer is a report that translates Gartner Peer Insights into actionable insights. It is the go-to review and rating platform for IT managers and decision-makers.
Customer feedback is compiled into an average star rating and individual ratings for several subcategories. ESET scored 4.5 stars out of 5 from 110 reviews, including 4.5 ratings in Evaluation and Contracting and Product Capabilities. Based on ratings and the level of review coverage, ESET is a Customers’ Choice security solution with an overall rating of 4.6.
G2
G2 is a review and rating platform that uses consumer feedback with social data to provide insights for various business software solutions. ESET holds 4.5 stars out of 5 from 415 reviews on G2’s platform. “It is ahead of the competition in Malware Detection and Endpoint Intelligence. ESET is also leading against its competitors in several ratings, including Meets Requirements, Ease of Use, Ease of Setup, Ease of Admin, Quality of Support, and Ease of Doing Business With. The reviews note that ESET has outstanding support and offers “complete protection against hackers, malware, and data loss.”
Thanks to this, ESET maintained its ‘Leader’ position in G2 Grid® for Endpoint Protection Suites, outperforming most of our competitors.

Figure 7: ESET in the Leaders quadrant in G2 Grid® for Endpoint Protection Suites
Summary
There’s no better way to assess a software solution than to consult the evaluation of independent IT experts and the feedback from real users. Combining expert opinions, market research and end-user insights paint a complete picture.
So, how does ESET fare in the market? Well, ESET is leading the pack in all of these areas. IT managers looking for a high-performing solution for business cybersecurity should have ESET on their radar.
ESET Research discovers Bandidos, a new spying campaign in Venezuela
The latest version of Bandook steals sensitive documents and credentials from corporate networks, creates a malicious Chrome extension, and misuses URL shorteners like Rebrandly and Bitly
BRATISLAVA, MONTREAL – ESET Research has recently uncovered a new and still active campaign that uses more advanced versions of the old crimeware Bandook to spy on its victims. The ongoing campaign is targeting corporate networks in Spanish-speaking countries, with 90% of ESET telemetry detections in Venezuela. ESET researchers have found new functionality and changes to Bandook. Because of the malware used and the targeted locale, ESET chose to name this campaign Bandidos.
ESET has seen more than 200 detections for the malware droppers in Venezuela in 2021; however, a specific vertical targeted by this malicious campaign could not be identified. According to telemetry data, the main interests of the attackers are corporate networks in Venezuela: some in manufacturing companies, and others in construction, healthcare, software services, and even retail. Given the capabilities of the malware and the kind of information that is exfiltrated, it seems that the main purpose of Bandidos is espionage.
The prospective victims receive malicious emails with a PDF attachment. The PDF file contains a link to download a compressed archive and the password to extract it. Inside the archive there is an executable file: a dropper that injects Bandook into an Internet Explorer process. The attackers use URL shorteners such as Rebrandly or Bitly in their PDF attachments. The shortened URLs redirect to cloud storage services such as Google Cloud Storage, SpiderOak, or pCloud, from where the malware is downloaded. The main purpose of the dropper is to decode, decrypt, and run the payload and to make sure that the malware persists in a compromised system.
“Especially interesting is the ChromeInject functionality,” says Fernando Tavella, an ESET researcher who investigated the Bandidos campaign. “When the communication with the attacker’s command and control server is established, the payload downloads a DLL file, which has an exported method that creates a malicious Chrome extension. The malicious extension tries to retrieve any credentials that the victim submits to a URL. These credentials are stored in Chrome’s local storage.”
Bandook is an old remote access trojan. There are references to it being available online as early as 2005, though its use by organized groups was not documented until 2016. In 2016, it was reportedly used to target journalists and dissidents in Europe. Then, in 2018, it was used to attack new targets, such as educational institutions, lawyers, and medical professionals. Finally, in 2020, it was seen in attacks against multiple sectors, including government, financial, IT, and energy.
“Previous reports have mentioned that the developers of Bandook might be developers for hire, which makes sense given the various campaigns with different targets seen through the years. We must note, however, that in 2021 we have seen only one active campaign: the one targeting Spanish-speaking countries that we document here. It shows though that it is still a relevant tool for cybercriminals,” opines Matías Porolli, an ESET researcher who worked on the analysis with Tavella.

Overview of a typical attack in the Bandidos campaign
For more technical details about Bandidos, read the blogpost “Bandidos at large: a spying campaign in Latin America” on WeLiveSecurity. Make sure to follow ESET Research on Twitter for the latest news from ESET Research.

Top 5 Ways to Use a Document Camera In a Classroom

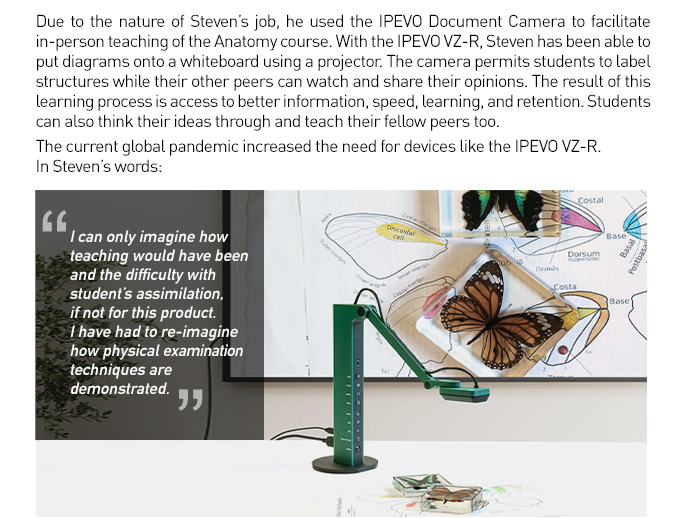
After experiencing a turbulent year due to the pandemic, some schools an businesses look to start welcoming people back into buildings while others intend to stay put. Document cameras emerged as one of the most crucial tools throughout the past year and look to further solidify its importance going forward. The ability to integrate document cameras with various software and hardware is a major contributing factor to its widespread success and popularity.
Below are 5 great uses you can give to document camera in a class or work setting:
Read and Annotate
Document cameras are the go-to tool when it comes to presenting materials. Effortlessly switching between materials and making live annotations results in a much smoother and time-efficient experience all around.

Record Lessons
With the steady increase in technology integration, educators all around the world are using document cameras to record lessons and tutorials. The small and simple yet powerful build of the document camera makes for a quick setup that requires minimal effort and space.

Document Scanning
Scanning stacks of paper may seem like a daunting and time-consuming task but document cameras are able to speed the process up significantly. Once the device is set up in place, scanning documents becomes as simple as sliding it under the lens and clicking a button.

Live Demonstrations
There are multiple instances where crowding around something to catch a glimpse simply doesn’t cut it. Intricate gadgets with small parts, chemical reactions, dissections, and art techniques benefit the most from it. Projecting the image on a large screen ensures that everyone is able to view the demonstration at an optimal angle.

Distance Viewing
For low-vision students, it can often be extremely difficult to follow along with the rest of the class. Simply have the set up the document camera, pointed towards the board, and zoom-in as needed. This is especially useful as the student may also take snapshots throughout the class if necessary.

Though document cameras have been around for quite a while, it wasn’t until the past year did it really pick up mainstream attention. After people started implementing document cameras into their daily routine, they quickly realized just how simple and powerful these tools were whilst providing much-needed versatility. The pandemic may be slowly coming to an end, but document cameras are here to stay.