Skip to content

Emerging Cyber Threat: USB Port Hacking

The USB Trojan Horse: How Juice Jacking and BadUSB Turn Everyday Ports into Major Threats

The humble USB port, a symbol of convenience, is being weaponized by cybercriminals at an alarming rate. From public charging stations to discarded flash drives, these everyday connectors are becoming a major vector for malware and data theft, prompting official warnings from agencies like the FBI and FCC. This is no longer a theoretical threat—it’s a clear and present danger in our digital landscape.

The Modern USB Threat Landscape

Attackers are exploiting USB connections through several sophisticated methods:

  • Juice Jacking: The Public Charging Trap. This well-known technique involves compromising public USB charging stations in airports, hotels, and cafes. By embedding malicious code into these ports, attackers can install malware or siphon personal data and passwords from any device that plugs in to charge. The FBI considers this risk so significant that it has advised the public to avoid these stations entirely.
  • BadUSB and Malicious Drives: Deceptive Hardware. More advanced than simple malware, a BadUSB attack alters a device’s firmware, making it impersonate a trusted peripheral like a keyboard while secretly executing malicious commands. This type of attack is incredibly dangerous as it can bypass standard antivirus software. Hacking groups like UNC4990 have been observed using this method, alongside the simpler tactic of “baiting”—deliberately dropping infected USB drives in public areas, waiting for a curious individual to plug it into a computer.
  • Targeting the Enterprise. These threats are not limited to individuals. A recently discovered vulnerability in the iPhone’s USB-C port demonstrated how malicious code could bypass even Apple’s strict security measures. For organizations, the risk is magnified when employees unknowingly introduce a “bait USB” into the corporate network, potentially compromising the entire system.

A Multi-Layered Defense is Crucial

In response, governments are issuing alerts, and manufacturers are releasing security patches like Apple’s USB Restricted Mode. However, no single solution is foolproof. A robust defense requires vigilance at both the organizational and individual levels.

For businesses, the most effective strategy is to establish clear policies on USB usage, provide comprehensive employee training on these specific threats, and accelerate the transition to secure, cloud-based platforms for data storage and file sharing.

For individuals, the rules are simple: avoid public USB charging ports, carry your own charger and power bank, and never plug in a USB device from an unknown source. Using a “USB data blocker” can also provide a physical barrier against data transfer when using untrusted ports. By treating every unknown USB port and device as a potential threat, we can mitigate this rapidly emerging risk.


About Penta Security
Penta Security takes a holistic approach to cover all the bases for information security. The company has worked and is constantly working to ensure the safety of its customers behind the scenes through the wide range of IT-security offerings. As a result, with its headquarters in Korea, the company has expanded globally as a market share leader in the Asia-Pacific region.

As one of the first to make headway into information security in Korea, Penta Security has developed a wide range of fundamental technologies. Linking science, engineering, and management together to expand our technological capacity, we then make our critical decisions from a technological standpoint.

About Version 2 Limited
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

How to connect multiple offices with a VPN

Summary: A VPN enables companies to securely link multiple sites and provides employees with safe access to internal resources.

If your business has multiple locations, you probably want them all to stay connected, right? You need information to flow smoothly between sites, without any hiccups. But it’s not like you can achieve that by just plugging in a few cables. It doesn’t work like that.

What you need is to set up—that is, digitally build—a robust and secure network that can connect multiple offices without ever putting your company’s data at risk. That’s where a VPN enters the scene. Let’s show you how you can use it to create a secure connection between your sites.

Why companies need to connect multiple offices securely

It doesn’t matter if your company connects just two offices or a dozen—once you’ve got one network linking multiple locations, someone might be looking for a way to get into one site and use it as a gateway to others.

That is, if your connection isn’t properly secured, cybercriminals could potentially break into your internal systems from any of the connected sites. Even if not, they might try to intercept sensitive data as it moves between locations. Either way, it could lead to stolen customer information, leaked intellectual property, or exposed communication like internal emails.

And that’s not all. A weak connection between company offices can open the door for malware or ransomware to spread. Just one compromised location can put your entire network at risk. That kind of breach can bring all your operations to a halt and cost you a lot of time and money.

Last but not least, there’s compliance. As you know, many industries have strict data privacy rules—like GDPR, HIPAA, and many others. So, if your office-to-office communication isn’t well protected, you could end up not being compliant with the regulations, which can lead to fines, legal issues, or damage to your reputation.

 
How you can connect to the company network via VPN

Most people think of a VPN—short for Virtual Private Network—as software that hides their device’s IP address and keeps their internet activity private. And that’s true—but VPNs can do more than that. For example, employees can use them to connect securely to their company’s internal network.

So, how does it work from the user’s perspective? This is done using a VPN client—an application that allows your device to connect securely to a VPN server. But instead of connecting to a public or random server, you’re connecting to your company’s own virtual private network.

Of course, that VPN server isn’t open to just anyone. The company must first give you access rights or configure your account to allow VPN access. Then, each time you try to log in, you’re verified, usually through authentication methods such as passwords, TOTP (time-based one-time password) codes, or magic links.

Once you’re authenticated, the VPN client and the company’s server create an encrypted tunnel between your device and the internal network. This allows you to safely access files, apps, and other internal systems—just as if you were in the office, connected to the company Wi-Fi.

Key benefits of using a VPN to connect multiple locations securely

We’d go as far as to say that once a business grows beyond a single headquarters, setting up office-to-office VPN connectivity isn’t just a nice-to-have—it’s essential. Why? Because it brings so many benefits to how teams work and collaborate that it becomes an operational necessity.

Top reasons to use a VPN for connecting multiple sites

Here are a few key advantages of connecting your offices through a VPN:

  • Secure data sharing: By creating encrypted VPN tunnels between your offices, you ensure that sensitive information remains protected during transfer from one location to another.
  • Consistent access to company systems: Employees in different locations—including remote workers—can securely access shared systems, services, and data as if they were all working side by side.
  • Reduced costs: Rather than paying for expensive dedicated connections between offices, a VPN allows you to safely use the public internet at a fraction of the cost.
  • Improved access management: When you connect multiple offices with a VPN, your IT team can easily manage network resources, monitor activity, and enforce strict security policies—all from one central place.
  • Controlled access: VPN gateways let you restrict which parts of the company network employees can access, making sure that everyone can only reach the resources they’re authorized to use.
  • Better collaboration: When teams can share data easily and safely across locations, working together between offices just gets smoother and more productive.

Choosing the right VPN setup for your company

Decided to connect multiple offices with a VPN? Great! Now, the next step is figuring out how to set it up. There are two main options to consider: site-to-site VPN and remote access VPN.

Each of those meets different needs and works in different ways depending on your company’s size, structure, and how your teams connect to resources. So, the setup and management will look different based on which route you take. Because of that, it’s worth taking a little time to learn about both before making a decision. Here’s what you need to know.

Site-to-site VPN

Like its name suggests, Site-to-Site VPN is about connecting entire office networks that are in different physical locations.

The way it works is by using routers or firewalls at each office, which are set up as VPN gateways. These VPN gateways encrypt and decrypt data as it travels between offices. So, data is technically moving over the public internet, but it goes through a secure tunnel from start to finish, which keeps it protected while in transit.

Once configured, these site-to-site VPN tunnels are either always active or automatically turned on when needed. As a result, devices at each location can see and access each other’s resources as if they’re on the same local network—even though they’re actually miles apart.


Remote access VPN

Remote access VPN allows individual users to connect to your company’s private network from any location.

So, unlike a site-to-site VPN, which connects multiple office networks together, here each employee’s device uses a VPN client to log in and create an encrypted connection to the company’s VPN server. Once that connection is established, the user gains access to the company’s digital resources. However, administrators can—at any point—control exactly what the user can see and do by using access controls, network segmentation, firewalls, and other security tools.

As the name implies, this setup is best suited for remote work, where employees are spread out around the world but still need secure access to the same company systems, data, and tools to do their jobs effectively. This setup can also be used to connect employees from different offices, treating each office as a remote site.

Best practices for configuring office-to-office VPN

Setting up a secure connection between offices looks different for every company—after all, no two companies have the same number of offices, countries, devices, or systems. But there are a few key things every company should do when setting up this kind of connection, and they are:

  • Properly configure all VPN gateways: Set up the right IP addresses, routing rules, and firewall permissions to make sure data travels securely between locations.
  • Use strong encryption: Ensure data is encrypted while in transit using up-to-date algorithms like AES-256 or XChaCha20.
  • Implement authentication methods: Use techniques like multi-factor authentication (MFA) to ensure only trusted users and devices can connect.
  • Monitor your VPN setup at all times: Watch out for unusual activity or connection problems to catch potential threats before they escalate.

How Nordlayer can help secure your company network

As you’d expect from a truly advanced network access security platform, NordLayer brings the best of both worlds with a secure access service edge (SASE) solution that enables the creation of a hybrid setup combining site-to-site VPN and remote access VPN.

That’s right! With NordLayer, you can create an encrypted connection between your branch offices (Site-to-Site VPN) while also making it possible for individual users to securely connect to your company’s private network (Business VPN)—simultaneously, with advanced access controls for each VPN connection.

With such flexibility, along with features like Always On VPN and support for Zero Trust policies, NordLayer makes it easy to connect multiple offices without compromising your team’s workflows.


About Nord Security
The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

About NordLayer
NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

About Version 2 Limited
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

The changing DNA of organized crime, Not-So-Secret Business Passwords, and UX/UI updates: catch up with NordPass in Q2 of 2025

Media and awards

Over the past few months, we have received quite a few awards. It’s a great honor to be recognized for our work creating advanced yet easy-to-use cybersecurity solutions.

GQ’s pick for the best password manager

To our great joy, the GQ team selected NordPass as the best overall password manager this year. GQ tests password managers based on price, ease of setup, and the quality of different features like autofill or password sharing. They noted that NordPass offers an easy-to-use interface, many features, and a good free tier.

American Business Stevie Bronze Medal

Here at NordPass, we strive to bring our users the best possible experience. So when there’s an unexpected hiccup or issue, our amazing Customer Support team is there to help 24/7. It was a great pleasure to be recognized by the American Business Stevie Awards with the Bronze Medal for Customer Support Department of the Year.

CyberTech category winner of the Global Tech Awards

Not a day goes by that we don’t think about how to improve and make cybersecurity effortless for individuals and companies. So, our team is truly happy to be recognized for excellence in the Cyber Security Technology category at this year’s Global Tech Awards. The selection criteria include technical quality, user experience, scalability, social impact, and more.

Global InfoSec Award for Passwordless Authentication

Lastly, the Global InfoSec Awards recognized NordPass for its passwordless authentication. This award celebrates NordPass’ commitment to advancing secure, password-free authentication solutions. With our passwordless authentication platform, Authopia, enterprises can enable seamless, passkey-based logins, help businesses reduce account takeover risks, and improve the user experience.

We have a passwordless login for our vault as well, so our users can access their accounts via biometrics. Additionally, NordPass supports cross-platform passkey storage and integration with identity providers like Google Workspace or Azure Active Directory.

Freshest NordPass updates and improvements

Okay, now let’s get back to the core of NordPass—the product itself—and see what improvements and updates our team has made.

Sharing Hub update

As organizations grow, the question of sharing becomes more prominent. More and more credentials are moved around teams and departments, often informally or without consistent oversight.

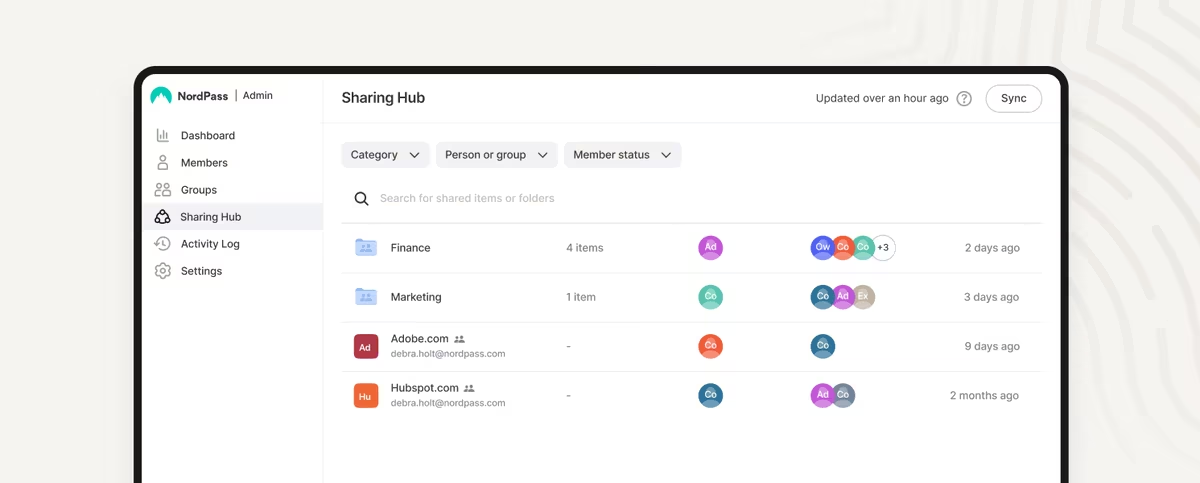
To tackle this problem, we released Sharing Hub this autumn, which included a viewing option that allowed organization Owners to see which items could be accessed and by whom, as well as who had shared or created them. This spring, we significantly improved the feature. Now, Owners can control access to all shared company credentials by granting, modifying, or revoking access rights for any shared item or folder as needed. They can also transfer ownership if required, all from a single place—the NordPass Admin Panel.


Sharing hub

What’s new with the company-wide Data Breach Scanner?

Similarly, we have made significant improvements to our tried-and-true Data Breach Scanner.

To ensure that your company gets the most from NordPass, we will now monitor your company’s domain based on the organization Owner’s email address, eliminating the need for separate verification. Note that in this case, you’ll only get notifications about the breaches but no detailed information on them. If you want to get that additional info, you’ll have to add your domain and verify it. As for domain verification, it’s now seamless and automated.

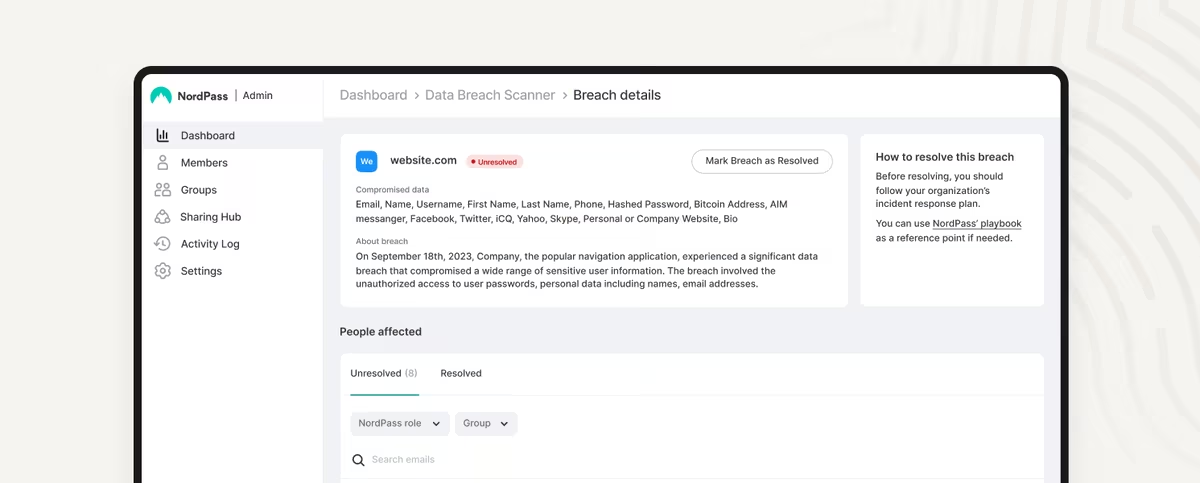
We also gave the breach report a facelift. Now, you’ll find a detailed description of the breach, the data it compromised, a list of affected organization members, and some recommendations for resolving the breach. In addition, admins can now see which breaches have been resolved and by whom.

Lastly, the “Breach details” list is now easier to navigate because it clearly distinguishes members’ statuses within the NordPass organization. It shows whether members are uninvited, suspended, or Admins, and which groups they belong to.

Data Breach

Business Account session management

From now on, organizations can set a 1-hour, 4-hour, 1-day, 7-day, 30-day, or custom time interval, after which the member session will end, and they will be logged out from NordPass. To continue using NordPass, the member will need to log in again, either using SSO or their Business Account credentials, and then verify their account with MFA, Master Password, or biometrics. For optimal security, we recommend setting the interval to 7 days. After this time, the member will need to log in again.

Filtering the Activity Log

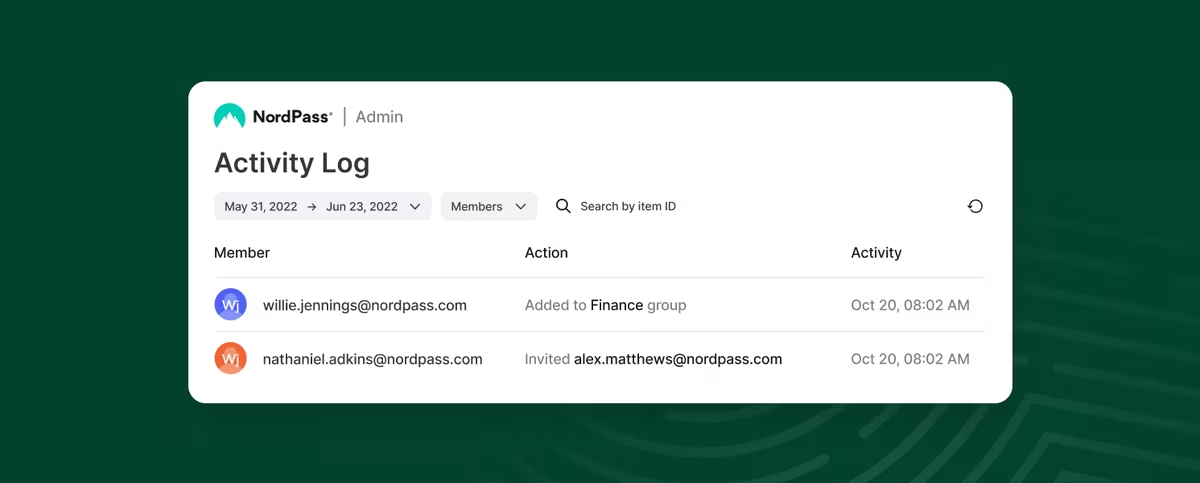
Up next is the filtering improvement for the Activity Log feature. The Activity Log lets organizations gain insight into user activities by tracking access updates and identifying unusual behavior. From now on, Admins and Owners can search the Activity Log by the item ID, allowing them to streamline security investigative processes by quickly identifying suspicious activities. This filtering option, together with filtering by member and date, allows admins to see all actions made to a particular item.

activity log

Integration with Microsoft Sentinel

By striving to build a seamless NordPass user experience, we have integrated with Microsoft Sentinel, an SIEM tool. From now on, our Enterprise customers can significantly strengthen their organization’s ability to meet compliance objectives by maintaining audit trails.

This integration allows Enterprise users to export and access NordPass activity logs alongside the data from other systems within Microsoft Sentinel. In doing so, companies can gain a holistic view of their security posture, conduct analysis, and quickly detect and respond to potential threats.

You asked, and we delivered

We are always eager to hear your feedback and improve accordingly. So, with that in mind, we ended last quarter with several user experience tweaks. Starting with the NordPass autofill icon, we have made 2 UX improvements:

  • You can now easily tell if your vault is locked thanks to the improved NordPass autofill icon. If you want to unlock the vault, simply click on the icon to open the pop-up window where you can enter your Master Password or use biometrics.

  • You can now turn off the NordPass autofill suggestions by clicking the icon. The choice will stay the same throughout the form you’re filling in.

autofill

NordPass’ interface redesign

The vault interface across all our platforms and the Admin Panel are where our users primarily engage with and monitor their cybersecurity status. Therefore, we want to provide the most user-friendly experience possible. This quarter, we made some design changes to the iOS, Android, and other platforms to give the UI a more modern look and feel, in line with our NordPass rebranding, which we revealed last year. Additionally, all these platforms have seen usability improvements.

Research and other reports

This quarter was equally rich with research and reports, ranging from our classic report on the most common passwords to a brand-new one on digital anxiety. So let’s see what we discovered:

TOP 20 Not-So-Secret Business Passwords

Together with NordStellar, we’ve analyzed the most common business passwords from 11 industries to uncover the habits behind office doors. Unfortunately, the password patterns are poor and truly not-so-secret. So poor, you might be able to guess the 3 most popular corporate passwords yourself. Yes, they’re “123456,” “123456789,” and “12345678.” If you guessed “password,” don’t worry, it’s on the list.

Our research also showed that using an email address as a password is just as common—it’s convenient, yes, but it’s one of the quickest ways to give your business credentials to hackers. Similarly, many people use their names for work-related passwords—another unfortunate practice that can expose the entire organization’s sensitive data to potential threats.

top 20 not so secret bisiness passwords

TOP 200 Most Common Passwords

Ah, and yes, what’s NordPass without our annual TOP 200 Most Common Passwords research? It’s our sixth year in a row—this time, in collaboration with NordStellar—analyzing people’s password habits. And not so shockingly, they are still bad.

We researched passwords from 44 countries that were stolen by malware or exposed in the data leaks. Because they were leaked with email addresses in most cases, we could distinguish corporate and personal credentials by domain name, gaining more insight into both areas.

Top 200 most common passwords

Digital Anxiety Report

This quarter, we tapped into a new field and released a study on digital anxiety. We wanted to see how many people struggle with it and what’s causing it. The results, or reasons for digital anxiety, are probably those that most people will relate to.

Nearly 80% of people have digital anxiety, which mostly comes from the fear of facing cybersecurity issues like account takeover, identity theft, or scams. However, mild to moderate anxiety was reported due to excessive ads or lack of internet access. As it turns out, even minor inconveniences online can take a toll on our mental well-being.

Stop reusing passwords

Do you have that one good and faithful password you’ve used since high school? Maybe it’s scaterrrboi!94, which ticks most sites’ requirements for password length and includes a special character and two numbers—why change it? Well, according to our recent survey, it turns out that it’s common to reuse passwords. Learn more about why people still reuse passwords in 2025 and why this habit poses a formidable threat to cybersecurity.

Ex-hacker: 5 cyber threats that password managers protect against

We seek to spread knowledge about cybersecurity in every possible way, and sometimes, showing the nitty-gritty behind it is just what might be needed. So this spring, we collaborated with Daniel Kelley, a reformed black hat hacker, to understand the 5 main cyberattacks that can be prevented using a password manager. These threats include phishing, credential stuffing, brute-force attacks, keyloggers, and database leaks. By revealing the inner workings of these attacks, Daniel shed light on why relying on a password manager is vital.

Cyber threats

2025 EU-SOCTA: the changing DNA of organized crime

The EU-SOCTA documented a serious shift in organized crime: it seeped into the online world, creating new hybrid and wholly virtual threats that require unprecedented strategies to tackle. These threats may be accelerating and becoming more dangerous and destabilizing.

For example, one of the biggest threats posed by serious and organized crime is the destabilization of the EU. Criminal organizations aim to reduce trust in the legal system and government by spreading violence, corruption, and illicit proceeds. They rely on digital innovations like AI to conceal their activities and make tracing crime back to its source harder.

Although the landscape painted by the EU-SOCTA might seem grim, it indicates potential future trends, allowing individuals and businesses alike to prepare for evolving risks. So, we took this opportunity to explain how Nord Security products, including NordPass, can help.

Breaking down SOCTA 2025

Bottom line

And that’s a wrap! This quarter was busy with research and product improvements. Yet one thing is clear: we’re not planning to stop this summer, so we’ll see you again in a few months to review what we’ve been brewing. Stay safe with NordPass!

About NordPass
NordPass is developed by Nord Security, a company leading the global market of cybersecurity products.

The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.

About Version 2 Limited
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

Should You Pay For Middleware Tools?

A hybrid of diverse technologies and disparate endpoints comprise the modern IT landscape. Middleware unifies and connects these systems, and today enterprises have a variety of commercial and open source middleware tools to choose from. But which middleware technologies are best for the job — and should you be paying for them?

In this blog, we give an overview of middleware, including the different types of middleware technologies, how they are used, and why teams should consider switching to open source middleware tools.

What Is Middleware?

Middleware is a broad category of software that encompasses any type of software used to connect one system to another, or one layer to another.

Middleware can be described variously as “glue”, as a conduit, or as an adapter that connects and links different systems. Some middleware also provides a platform or foundation to build applications, providing common functionality and connectivity so application development can focus on unique requirements. Common categories of middleware include web servers, application servers, content management systems, messaging and service buses, and other integration frameworks and services.

Types of Middleware Technologies and Middleware Tools

Since middleware can encompass most any software between the OS and application layers, there are many different categorizations — both based on how it is used and by location in a typical application architecture. Some common categories include the following:

Message-Oriented Middleware

One of the most pervasive pieces of middleware, message-oriented middleware (MOM), includes message queues, message brokers, and message streaming platforms. Message-oriented middleware focuses on reliably routing and delivering message-based traffic to connect disparate applications and systems. Some MOM platforms are also able to transform and translate messages to enable communication between applications written in different languages or using different protocols. MOM also helps decouple applications and enables asynchronous and decoupled communication across large architectures.

Remote Procedure Call Middleware

Remote Procedure Call (RPC) middleware is used to act as a conduit for synchronous or asynchronous service calls between different systems.

AI Agent Middleware

AI Agent middleware is software that acts as a link between AI models and the applications that use them. Applications can then benefit from AI analysis, insights, and automation. 

Application Server Middleware

Application server middleware consists of standard application servers used to deploy, run and manage enterprise applications. They often provide additional support in terms of standardizes libraries/APIs (like J2EE or .NET), and standardized configuration (security, logging, and management).

Web Middleware

Web middleware includes traditional http servers such as Apache and Nginx, used for serving static resources quickly and reliably, or acting as an intermediary between clients and application servers or services.

ORB Middleware

Object Request Broker (ORB) middleware brokers request between applications using a standardized object representation. CORBA (Common Object Request Broker Architecture) is one example of this type of middleware.

Transaction Processing Middleware

Transaction processing middleware is generally service-based and supports executing transactions across a distributed set of applications. This type of middleware allows for executing business and other processes in a step-by-step fashion with guarantees execution of the proper application steps in order and can also provide the ability to roll back a transaction if an error occurs.

Back to top

What Is Middleware Used For?

Middleware is fundamentally a bridge, and can be defined as any software that bridges two or more other systems. This can be across architectural layers — like an interface between applications and storage (a database). This can also be in the form of frameworks and APIs that provide efficient communication between or even within an application.

Middleware standardizes and simplifies integration of different components to assemble a comprehensive solution to a problem. The popularity of common middleware packages mean they are proven in production and are well supported.

Middleware can also support application development by providing prebuilt functions for integration such as single-sign-on, messaging, caching, common design pattern implementation and other common functions. Middleware is also used extensively when connecting and integrating with legacy systems — by providing adapters, APIs, transformations, and messaging, new development can happen around legacy systems rather than all at once.

Middleware connections to legacy systems can enable migration to modern architectures with higher performance and higher reliability.

Back to top

Commercial Middleware vs. Open Source Middleware

Commercial, comprehensive middleware offerings like IBM WebSphere (which includes IBM MQ) can come at an enormous price tag for organizations — especially at scale. With a sub-capacity pricing model, and a contractual delineation between license costs and support costs, larger organizations can quickly find their annual costs moving above seven figures.

There are less expensive commercial middleware options, but all commercial software (especially within large ecosystems like Red Hat, Oracle, or IBM), carries the risk of vendor lock-in. Any short-term benefits get overshadowed by the eventual cost of moving on from that ecosystem, and the potential for burgeoning contract costs from the commercial provider.

That’s not to say that open source software isn’t without costs of its own. Open source requires a high degree of expertise in order to fully utilize it, either in-house or from a third party like OpenLogic that can provide open source middleware support.

In terms of technological capability, open source software is the clear leader — with popular options like ActiveMQ, Camel, Kafka, and others that can fulfill and exceed the functionality of their all-in-one commercial counterparts. Ultimately, choosing between commercial and open source comes down to the needs of the organization, the state of their underlying IT infrastructure, and their capacity to work with and support that software.

Considering Your Middleware Options?

Read our Decision Maker’s Guide to Open Source Middleware for an overview of available options, and when to use them.

c

DOWNLOAD FOR FREE

Back to top

The Best Open Source Middleware Technologies

The best middleware technologies tend to be based on the needs of the user, but our team has a few versatile favorites we will explore in this section. 

Apache Camel

Apache Camel is the industry standard for reducing boilerplate code for complex integrations, all while maintaining features like automatic error handling, redelivery policies, and the ability to handle complex aggregations. Apache Camel is a domain-specific language that’s an implementation of the Enterprise Integration Patterns (EIPs) and helps organizations solve a range of very specific problems.

Apache Camel provides a configuration syntax and runtime to configure EIPs within your application federation layers.  By normalizing message data, providing easy transformation mechanisms, and giving developers pre-built components that manage message exchanges, nearly any endpoint imaginable can be integrated.

For developers interested in learning Apache Camel, OpenLogic offers in-depth, expert-led Apache Camel training courses. For an example of how Camel can be applied, this banking company case study is a good place to start.

Apache ActiveMQ

The Apache ActiveMQ project consists of two separate messaging technologies: ActiveMQ Classic and ActiveMQ Artemis. Both technologies are currently maintained and will continue to be for the foreseeable future. Artemis was at one point seen as the successor to Classic, but that is no longer the case. Still, Artemis is viewed as a more modern approach to messaging.

Both ActiveMQ technologies are mature and widely adopted messaging platforms, with thousands of companies relying on them. Businesses can adopt either ActiveMQ technology quickly, and their familiar concepts will be accessible to anyone comfortable with JMS. The two active communities and strong ecosystem continue to ensure long-term viability and relevance. 

Compare IBM MQ vs. Kafka vs. ActiveMQ >>

Apache Kafka

Apache Kafka is a stream processor and can be used as a message broker as well. If architecture or software requires low end-to-end latency with exceptional durability (persistence), Kafka is the piece of software to provide this and other functionality. Whereas traditional message brokers focus on a pattern of allowing consumer applications to work on one piece of data at a time, Kafka allows for the analysis of lots of individual pieces of inflight data. 

This makes Kafka an ideal candidate for implementing streaming analytics and Big Data applications. Designed at LinkedIn to scale to hundreds of millions of messages, though not as lightweight a solution as ActiveMQ, it is ideal for working on astronomically large datasets. Kafka is often used with Kafka Connect to pair with data sources and destinations.

Read Kafka Case Studies >>

Apache Tomcat

Apache Tomcat is an open source Java application server that is capable of powering enterprise-scale web applications. Though not a full-fledged JEE server, Tomcat was originally conceived as the reference implementation for the Java Servlet and Java Server Pages specifications.

Tomcat remains a fast and lightweight implementation, even relied upon in new “serverless” frameworks like SpringBoot as a runtime container because of its thin profile. For simple and lightweight Java web applications, as well as the emerging world of Java microservices, Tomcat remains the top choice for deployment.

See what’s new in Tomcat 11 >>

Apache Pulsar

Apache Pulsar was developed originally by Yahoo! as an enterprise messaging platform and is a top-level Apache Foundation project. Pulsar is a feature-rich, scalable, low latency distributed messaging and streaming platform designed for large-scale environments. Its architecture separates the message processing functions (brokers) from the message storage functions (bookkeepers), so that it can scale horizontally in either component as needed. 

Pulsar supports multiple types of messaging, including pub-sub and guaranteed delivery topics, providing functionality that otherwise requires multiple tools. Messages can be modified in flight through the use of custom functions. Pulsar also offers geo replication, enabling replication between multiple Pulsar clusters, and supports up to one million topics. Multitenancy is handled through the use of namespaces and access control policies. 

Back to top

Final Thoughts

For organizations considering how to connect their data systems, harness their streaming data, or any other number of solutions middleware can provide, don’t overlook the advantages that come with deploying open source middleware. As this blog hopefully demonstrates, open source middleware technologies can deliver considerable cost savings and more flexibility to organizations — if they have the necessary expertise in-house or partner with OpenLogic to manage them.

About Perforce
The best run DevOps teams in the world choose Perforce. Perforce products are purpose-built to develop, build and maintain high-stakes applications. Companies can finally manage complexity, achieve speed without compromise, improve security and compliance, and run their DevOps toolchains with full integrity. With a global footprint spanning more than 80 countries and including over 75% of the Fortune 100, Perforce is trusted by the world’s leading brands to deliver solutions to even the toughest challenges. Accelerate technology delivery, with no shortcuts.

About Version 2 Limited
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

The Role of Actionable Data in ITSM

The digital revolution we are immersed in is a permanent revolution. We live in an era where the ability to respond quickly, almost immediately, to changes has become an indispensable requirement for every company (and we would also say for every worker). 

In this context, data is the most precious and strategic resource: it represents the new capital (“the new oil,” as we often hear) on which to build operational efficiency, innovation, and competitiveness. 

In the field of IT Service Management (ITSM), the value of data is even more evident: it is thanks to real-time insights that organizations can make proactive decisions, optimize services, and prevent incidents. 

Be careful, though! It’s not enough to collect the maximum number of information possible: you need to transform it into Actionable Data in ITSM, that is, data ready to guide immediate and concrete actions. 

And it is precisely on this point that we have focused the continuation of this article: not yet another contribution on the abstract importance of so-called “Big Data,” but a very practical journey that starts from the advantages of Actionable Data, then focuses on their impact in ITSM, with the related challenges to face. 

From Simple Data to Actionable Data in ITSM 

The IT departments of any type of company collect enormous quantities of information every day: support tickets, performance metrics, system logs, user feedback; and much more. An enormous mass of raw data… which, however, serves little purpose if it is not “refined.” The real challenge consists in making this information immediately readable, organizing it, and contextualizing it. Only in this way can value and therefore competitive advantage be extracted from data. 

To put it another way: Actionable Data in ITSM means having processed and “deep” data that supports operational and strategic decision-making with maximum effectiveness and in the fastest possible times. 

In practice, intelligent use of data allows you to: 

  • Move from reactive to proactive incident management 
  • Optimize resource utilization and improve workflows 
  • Drastically reduce downtime 
  • Improve user experience through targeted and predictive interventions 
  • Support continuous improvement and innovation tailored to your specific needs 

And we return to these advantages in more depth in the paragraph below. 

Get the latest ITSM insights! Explore AI, automation, workflows, and more—plus expert vendor analysis to meet your business goals. Download the report now!

The Main Advantages of Actionable Data in ITSM 

From information to action: this is what happens with the breakthrough of Actionable Data in ITSM. Just above we listed some of the advantages that derive from their exploitation; here below we explore them in depth, grouping them into what seem to us the three most important cores. 

From Reactive to Proactive Management 

Real-time analysis allows identifying trends, anomalies, and weak signals that, if caught in time, allow intervention before serious problems manifest. 

Solutions like EV Observe from EasyVista, for example, allow analyzing data in real time and activating predictive alerts. 

In short, it’s the old (and always valid) adage: prevention is better than cure. Translated into more contemporary terms: moving from reactive management to a proactive approach that aims to make IT infrastructure anti-fragile and minimize the impact of incidents on business. 

Indeed, pushing the reasoning to its limit, a good exploitation of Actionable Data in ITSM significantly reduces the very number of critical incidents. 

Service Optimization 

Naturally, it’s not just about incident management. Through correct interpretation of data, it’s possible to identify bottlenecks, inefficiencies, and areas for improvement in normal IT workflows. 

It’s like having a very high-definition photograph of everything that happens in the company; a photograph that evolves from moment to moment. And this is the indispensable starting point for perfecting processes, optimizing resource utilization, and reducing downtime. 

The final result? Increased productivity and simultaneous reduction of operational costs. 

Also in this case, a practical example: a product like EV Service Manager helps optimize request management processes, improving efficiency and significantly reducing time-to-resolution. 

It’s a product that leverages the power of Artificial Intelligence systems; and this brings us directly to the next point, related to automation. 

Automation as a Trigger for Continuous Improvement 

Data is the starting point, but also the endpoint. It’s the basis on which to test, correct, and refine processes and strategies. Consequently, by constantly monitoring KPIs and operational metrics, organizations can trigger the virtuous spiral of continuous improvement to their IT services. 

And there is no continuous improvement without automation: the two sides can only reinforce each other; indeed, now we can say that one makes sense only in relation to the other. All this is valid on a large scale, on the IT macro-structure, but also on a small scale, on individual processes. 

A simple and very common example? In Customer Service systems, starting from the analysis of historical tickets, rules can be created to automatically manage recurring problems. 

Here, with a practical and absolutely everyday case, is the difference between simple data and Actionable Data in ITSM. And at this point, below, we are ready to isolate its key characteristics. 

The Key Characteristics of Actionable Data in ITSM 

We opened this blog post by immediately drawing attention to the difference between simple data and Actionable Data. However, we must be clear: it’s impossible to draw a sharp red line between one and the other. 

What can certainly be done, however, is to identify some characteristics that make data, precisely, “actionable.” Below we analyze 5 of them, choosing those that seem most decisive to us: 

1. Timeliness 

In ITSM, speed is crucial. Data must be collected, analyzed, and made available almost in real time to have real operational value. Only updated data allows for rapid decision-making on emerging criticalities, avoiding escalations that could compromise service quality. 

2. Relevance 

Not all collected data is truly useful. And utility is not measured in abstract terms. Actionable data, therefore, is always closely connected to business objectives and defined KPIs. It’s necessary to select, from the mass of available information, those truly significant for the specific ITSM context, filtering out background noise. 

All this, moreover, must be done in a largely automated manner; otherwise it becomes an immense and unsustainable job from all points of view. 

3. Accuracy 

Data quality is fundamental: errors, incompleteness, or inaccuracies can generate wrong decisions and worsen problems instead of solving them. It is therefore essential to adopt rigorous data governance practices to guarantee the reliability of the information on which IT strategies are based. Also in this case, much depends on the objectives of the individual company, the KPIs, the landscape in which it moves. 

4. Clarity and Readability 

Data must be useful to humans. Therefore, it must be presented in a clear and easily interpretable way by operational teams. Effective visualizations, intuitive dashboards, and synthetic reports help make data immediately usable, reducing the time needed for analysis and interventions. 

5. Contextualization 

Data makes sense only within a framework. To become truly “actionable,” it must be placed in a broader context: correlated to historical trends, integrated with other indicators, interpreted in light of business processes, but also of the specific productive sector in which the company is situated. Only this way can it guide truly effective choices. 

Challenges in Obtaining Actionable Data in ITSM 

Although the potential of Actionable Data in ITSM is enormous, there are several practical challenges that companies must face. Among these: 

  • Information silos. When data is distributed in separate systems that don’t communicate with each other, it becomes difficult to have a complete and integrated view of IT processes. Overcoming silos requires information integration strategies, unified platforms, and management policies that favor sharing and transparency. 
  • Lack of analytical skills. Data availability is not enough: specific skills are needed to analyze, interpret, and transform them into concrete actions. In short, the added value of human capital is needed. Investing in analytical training and, where necessary, integrating specialized figures like data analysts or data scientists becomes a priority for every modern IT team. 
  • Legacy systems. Many organizations still find themselves bound to legacy systems that don’t natively support integration with advanced analysis tools. This limits data accessibility and their valorization. 

Fundamentally, it’s a very normal and human problem of habit and resistance to change: “it’s always been done this way, why change?” The answer lies in the fact that it’s the world around us that continues to change; and standing still is equivalent to losing ground. 

Conclusions 

We live in an era of permanent digital transformation. In this scenario, data analysis is the engine of IT competitiveness. Investing in collection, analysis, and action systems based on Actionable Data in ITSM is no longer an option, but an absolute necessity for those who want to aim for efficiency, proactivity, and continuous improvement of all IT processes. 

Get the latest ITSM insights! Explore AI, automation, workflows, and more—plus expert vendor analysis to meet your business goals. Download the report now!

About EasyVista  
EasyVista is a leading IT software provider delivering comprehensive IT solutions, including service management, remote support, IT monitoring, and self-healing technologies. We empower companies to embrace a customer-focused, proactive, and predictive approach to IT service, support, and operations. EasyVista is dedicated to understanding and exceeding customer expectations, ensuring seamless and superior IT experiences. Today, EasyVista supports over 3,000 companies worldwide in accelerating digital transformation, enhancing employee productivity, reducing operating costs, and boosting satisfaction for both employees and customers across various industries, including financial services, healthcare, education, and manufacturing.

About Version 2 Limited
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

AVD Nerdio Cost per User vs Oracle VDI TCO: How Thinfinity Saves You 40% or More

As desktop virtualization becomes foundational to hybrid work strategies, many enterprises turn to Azure Virtual Desktop (AVD) with Nerdio for its Microsoft-native capabilities. But beneath the surface, named-user licensing, layered infrastructure costs, and limited automation often result in higher-than-expected total cost of ownership (TCO).

Thinfinity VDI on Oracle Cloud Infrastructure (OCI) offers a smarter, more flexible alternative: a platform that leverages concurrent user licensing, aggressive automation, and lower cloud infrastructure pricing to reduce costs by up to 40–50% — all without sacrificing enterprise features.

Licensing Models: Nerdio vs Thinfinity — Key Differences

Nerdio Licensing Explained

Nerdio adds automation and management tools on top of Azure Virtual Desktop. Its licensing model includes:

  1. Microsoft AVD access rights – typically included via Microsoft 365 E3/E5 or RDS CALs.
  2. Nerdio Manager licensing – priced per named user or active user per month, typically:
    • $10–$14 per user/month
    • Each user who logs in that month triggers a charge, even if used once
    • No concurrency discount — licenses required for all users, all month

This model becomes expensive for organizations with:

  • Shift-based usage (e.g. call centers)
  • Occasional access roles (e.g. executives, QA/testers)
  • Unpredictable user patterns

Thinfinity Licensing Explained

Thinfinity Workspace licenses by concurrent user:

  • $10 per concurrent user/month (starting price)
  • Unlimited named users
  • Licenses required only for the peak number of simultaneous sessions

This is significantly more efficient for most organizations, especially those with fluctuating usage or low concurrency patterns.

In typical VDI deployments, peak concurrency is only 50–60% of the total user base. That translates to 40–50% fewer licenses — and less waste.

Comparison of VDI pricing models: Nerdio (Per-user, Higher Cost, Rigid Licensing) vs Thinfinity (Concurrent, Lower Cost, Flexible Licensing).

Infrastructure: Azure vs Oracle Cloud (OCI)

Beyond licensing, the underlying cloud infrastructure cost is another TCO driver. Here’s a direct comparison:

ResourceAzureOracle Cloud (OCI)Savings
4 vCPU / 16 GB VM~$140/month (D4_v5)~$77/month (E4.Flex) / $38 (Ampere A1)Up to 70% cheaper
100 GB Premium Disk~$8.10/month~$4.25/month~47% cheaper
Egress TrafficFirst 100 GB free, then ~$90/TB10 TB/month free, then ~$8.50/TBOver 90% cheaper

OCI’s pricing is more transparent and offers greater flexibility, including burstable and ARM-based instances — ideal for bursty VDI workloads like QA or developers.

Why Automation Matters for Cloud VDI Cost Control

Automation isn’t just a productivity booster — it’s essential for controlling costs.

Without automation:

  • Idle VMs may run for hours or days
  • Powered-off VMs still accrue storage and network costs (e.g., in Azure)
  • IT teams overprovision for peak usage “just in case”

💡 According to cloud optimization studies, idle VMs can inflate costs by 30–50%.

Automation helps by:

  • Starting/stopping VMs based on schedule or usage
  • Automatically deallocating or destroying idle machines
  • Scaling resources up/down in real-time

How Thinfinity uses automation to optimize Cloud VDI spending: VM Start/Stop Schedule, Deallocate Idle Machines, Real-time Resource Scaling.

Automation Comparison

FeatureAVD (Native)AVD + NerdioThinfinity on OCI
Auto Start/StopBasicEnhanced via UINative & role-aware
Autoscaling by ConcurrencyLimitedSession-host basedSession-aware, real-time
Destroy Idle Machines❌ No⚠️ Only stops VMs✅ Full destroy & rebuild
Idle Session Timeout❌ Manual policy✅ Configurable✅ Built-in & enforced
Cost Optimization Feedback❌ None✅ Estimator✅ Telemetry + policy-based
Cloud CompatibilityAzure onlyAzure onlyOCI, hybrid, multi-cloud

Thinfinity enables automated full-cycle VM lifecycle control, cutting cloud spend and operational overhead with every idle desktop it shuts down or destroys.

Case Study: 1,500-User Bank Deployment

Profile:

  • Industry: Financial Services
  • User Count: 1,500
  • User Segments:
    • Call Center – 600 users (60% concurrency)
    • Developers – 300 users (60%)
    • QA – 300 users (60%)
    • Management – 300 users (30%)

Licensing Cost Comparison

TeamNamed UsersPeak ConcurrentAVD + Nerdio (@$10/user)Thinfinity (@$10/user)
Call Center600360$6,000/month$3,600/month
Developers300180$3,000/month$1,800/month
QA300180$3,000/month$1,800/month
Management30090$3,000/month$900/month
Total1,500810$15,000/month$8,100/month
Annual——$180,000$97,200

Licensing savings = $82,800/year

Cloud Infrastructure Comparison (810 concurrent VMs)

CategoryAVD on AzureThinfinity on OCI
Compute~$110,000/year~$66,000/year
Storage (1 TB)~$8,000/year~$4,250/year
Egress (10 TB)~$8,000/year~$1,000/year
Total Infra$126,000/year$71,250/year

Infra savings = $54,750/year

Total TCO Comparison

CategoryAVD + NerdioThinfinity + OCIAnnual Savings
Licensing$180,000$97,200$82,800
Infrastructure$126,000$71,250$54,750
Total TCO$306,000$168,450$137,550/year (~45%) ✅

Why Enterprises Choose Thinfinity on OCI

  • 💰 40–50% lower TCO by combining concurrent user licensing with Oracle Cloud’s lower infrastructure costs
  • ⚙️ Automation-first architecture eliminates idle resources and cloud overspend through policy-driven VM lifecycle management
  • 🖥️ Purpose-built for virtual desktops and applications — supports session-based, 1-to-1 dedicated, persistent or non-persistent desktops, and even GPU-accelerated workloads
  • 🌐 Fully browser-based access with no client install required, enabling fast, secure access from any device
  • 🔐 ZTNA-Native with integrated support for MFA, SSO (SAML/OAuth), RBAC, and hybrid or multi-cloud deployments

Diagram illustrating Thinfinity OCI advantages: ZTNA-Native, Browser-Based Access, Virtual Desktops, Automation Architecture, Lower TCO.

Take the Next Step

If you’re currently running AVD + Nerdio or planning a VDI deployment, it’s time to explore a more cost-effective model.

About Cybele Software Inc.
We help organizations extend the life and value of their software. Whether they are looking to improve and empower remote work or turn their business-critical legacy apps into modern SaaS, our software enables customers to focus on what’s most important: expanding and evolving their business.

About Version 2 Limited
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.

The Role of Immutability and Air-Gapping in European Data Protection Strategies

European data protection is undergoing a quiet but radical shift. Once centered on legal compliance and checkbox auditing, it is now a high-stakes game of cybersecurity resilience. The rise of sophisticated ransomware, targeted attacks on backup systems, and the rapid expansion of cloud and IoT infrastructure have left organizations vulnerable, even those that believe they are prepared.

Regulatory evolution, like the GDPR and the new Data Act, reflects this new reality: data must be protected, recoverable, reliable, and continuously available.

This post explores two critical technologies that have emerged as strategic defenses in this environment: immutability and air-gapping. For European businesses facing a growing cyber threat landscape, they are increasingly essential to both compliance and continuity.

The Expanding Web of European Data Regulations

The EU’s data protection framework continues to evolve in scope and complexity:

  • GDPR emphasizes privacy and security. Article 32 mandates the ability to promptly restore availability and access to personal data in the event of a technical or physical incident.
  • ISO/IEC 27001 now includes enhanced cloud and SaaS protection measures, targeting resiliency in modern infrastructure.
  • The Data Act, applicable from September 2025, shifts the conversation toward accessibility, fairness, and transparency in data usage. It mandates secure and user-controlled access to data from connected devices, raising the bar for secure data handling.

These regulations are not mutually exclusive. Together, they push organizations toward architectures that can retain data securely, enable user access and deletion, and maintain business continuity even in a crisis.

Why Backups Alone No Longer Cut It

Backups have traditionally been a fallback option, essential but passive. Unfortunately, attackers have caught up. A 2024 report on cyberattacks and ransomware shows that over 2 million cases of breaches were recorded from 556 publicly disclosed breaches in the EU.

Modern ransomware now encrypts production data and actively seeks out and destroys backup files and infrastructure. For example, some ransomware strains include scripts designed to locate Veeam or Hyper-V backups and corrupt or delete them. Others exploit admin credentials to access and erase snapshots or backup volumes. Once this happens, even the most comprehensive backup strategy is rendered useless.

This is where immutability and air-gapping enter the equation.

What Is Immutability?

Immutability is the ability to store data in a way that cannot be altered, deleted, or overwritten for a defined retention period. Data kept on immutable storage stays exactly as it is—tamper-proof and time-locked once written.

Key Benefits:

  • Ransomware protection: Attackers cannot modify or delete immutable backup files.
  • Compliance-ready: Meets retention requirements under GDPR, financial, and healthcare regulations.
  • Audit integrity: Immutability ensures logs and data are preserved without risk of tampering.

How It Works:

  • On-premises: WORM-enabled NAS or object storage.
  • Cloud: Amazon S3 Object Lock, Microsoft Azure Immutable Blob Storage.
  • Backup software: Veeam, Commvault, and others now support immutable backup repositories.

What Is Air-Gapping?

Air-gapping, particularly with relation to the internet, is the process of separating a system or network from unprotected networks. In data security, it refers to either physically (offline) or logically (network-segmented with rigorous access restrictions) storing backup copies in an environment totally separate from any production network.

Types of Air-Gapping:

  • Physical: Offline tapes or disks, manually disconnected from the network.
  • Logical: Isolated systems or networks with strict access controls, segmentation, or one-way data transfer mechanisms.

Key Benefits:

  • Ultimate isolation: Prevents lateral movement of malware to backups.
  • Survivability: Data remains safe even in the case of a full production environment compromise.
  • Resilience during disasters: Ensures recovery capacity even when networks are down or compromised.

Comparison Table: Traditional Backups vs. Immutability vs. Air-Gapping

Feature Traditional Backups Immutability Air-Gapping 
Ransomware Protection Low High Very High 
Compliance Support Basic Strong (supports audit trails) Strong (ensures data isolation) 
Recovery Reliability Uncertain (can be tampered with) High (unalterable copies) High (offline or isolated backups) 
Network Exposure Always online Online but locked Offline or segmented 
Deployment Complexity Low Moderate Moderate to High 
Cost Low to Moderate Moderate Moderate to High 
Use Case Fit General, low-risk environments Healthcare, finance, and legal sectors Critical infrastructure, manufacturing 

Together, they provide layered protection. Immutable backups protect against tampering, while air-gapping ensures backups remain unreachable by attackers.

Use Cases in European Business Environments

SaaS Providers and Cloud Services 

Companies hosting customer data under GDPR must ensure availability and recoverability. Combining immutable snapshots with logically air-gapped storage helps meet resilience and compliance requirements.

Manufacturing and IoT-Driven Sectors 

With the Data Act mandating user access to IoT-generated data, manufacturers must store and protect vast volumes of telemetry. Immutability ensures these datasets remain accurate and auditable; air-gapping protects against targeted OT attacks.

Healthcare and Public Sector 

These sectors are highly regulated and often targeted by ransomware. Immutability secures patient records against tampering, while air-gapping ensures continuity even during a breach.

Agriculture and Smart Infrastructure 

Farmers using precision agriculture tools generate sensitive location and environmental data. Air-gapped storage can help protect this data from being exploited, while immutability ensures it remains accurate for subsidies, audits, or sustainability reports.

Preparing for the Future: Security Meets Regulation

The Data Act is pushing organizations to open up their data, but doing so without compromising security will be the real challenge. With the EU emphasizing accessibility and user rights, businesses must find ways to share data without increasing exposure.

Immutability and air-gapping provide the foundational safeguards to enable this. They ensure that data is unaltered even if it is widely shared. And even in cases of network breaches, a secure, offline recovery path exists.

In this way, these technologies are not just about cyber defense. They are enablers of digital trust, the cornerstone of Europe’s data-driven future.

Final Thoughts

European data protection strategies are evolving toward a model that assumes breach readiness as much as it assumes legal compliance. Immutability and air-gapping are central to this paradigm. When implemented correctly, they help businesses meet their obligations under GDPR, ISO 27001, and the Data Act and ensure that data can survive the threats that regulations can’t predict.

Security now means continuity. In Europe’s digital future, continuity requires architecture built for the worst day, not just the best intentions.

About Storware
Storware is a backup software producer with over 10 years of experience in the backup world. Storware Backup and Recovery is an enterprise-grade, agent-less solution that caters to various data environments. It supports virtual machines, containers, storage providers, Microsoft 365, and applications running on-premises or in the cloud. Thanks to its small footprint, seamless integration into your existing IT infrastructure, storage, or enterprise backup providers is effortless.

About Version 2 Limited
Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.

Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.